Generated 14/09/2026, 10:17. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources6
Tweets / X9
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
9 items
_RastaMouse @_RastaMouse
11 Sept, 18:55 · core
0.68
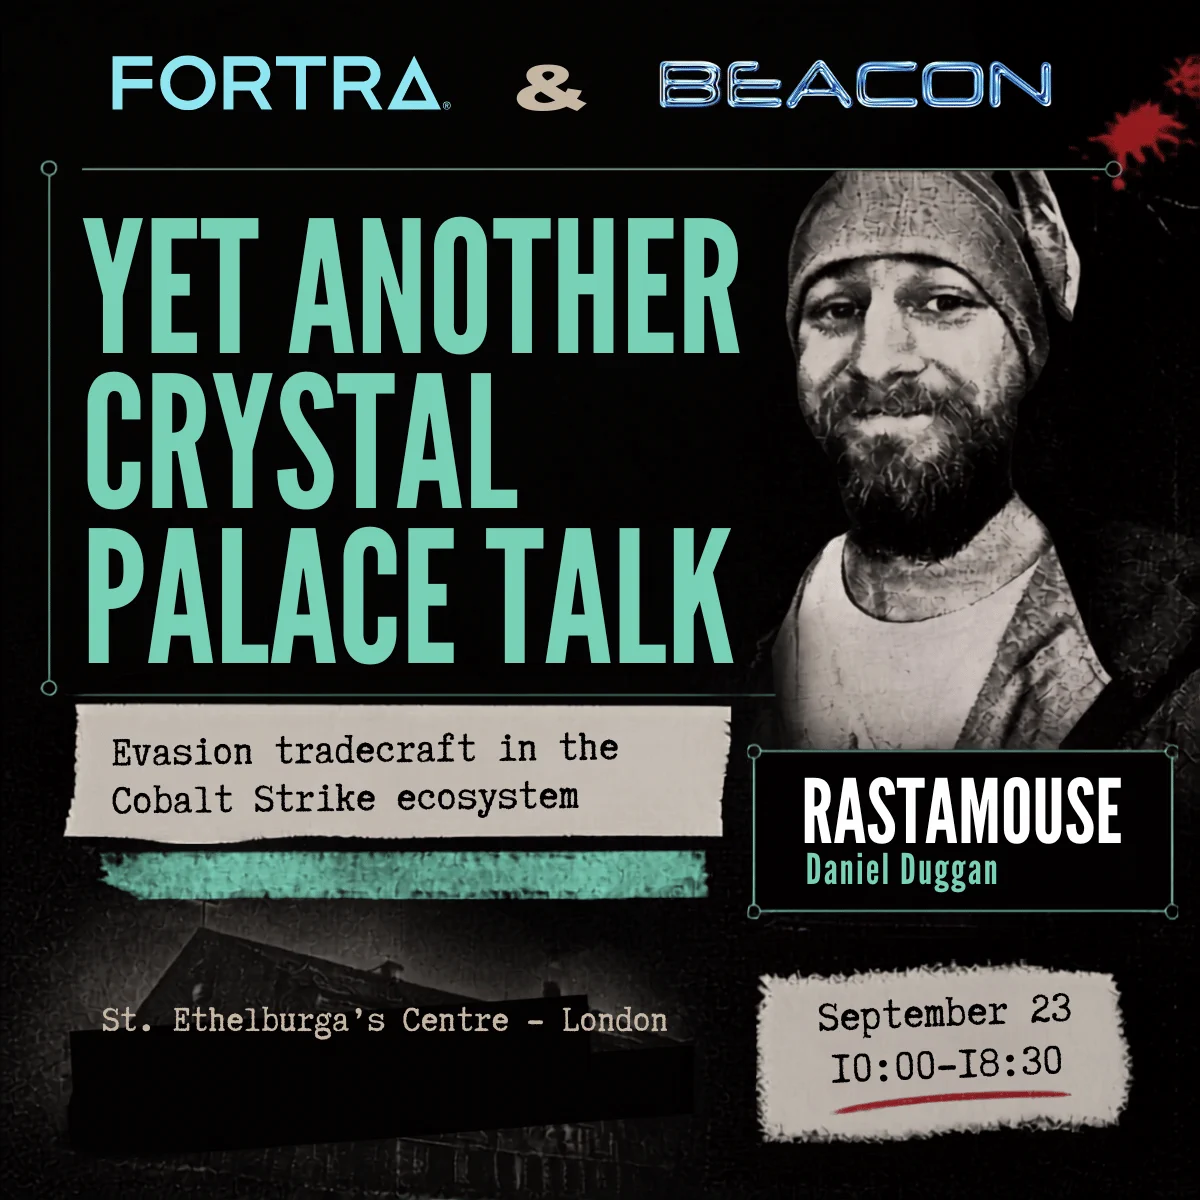
lmao is there not a better picture of me We're looking forward to Beacon 2026, where RastaMouse will present "Yet Another Crystal Palace Talk: Evasion Tradecraft in the Cobalt Strike Ecosystem". https:// info.fortra.com/beacon-2026 St Ethelburga's, London, UK September 23, 2026
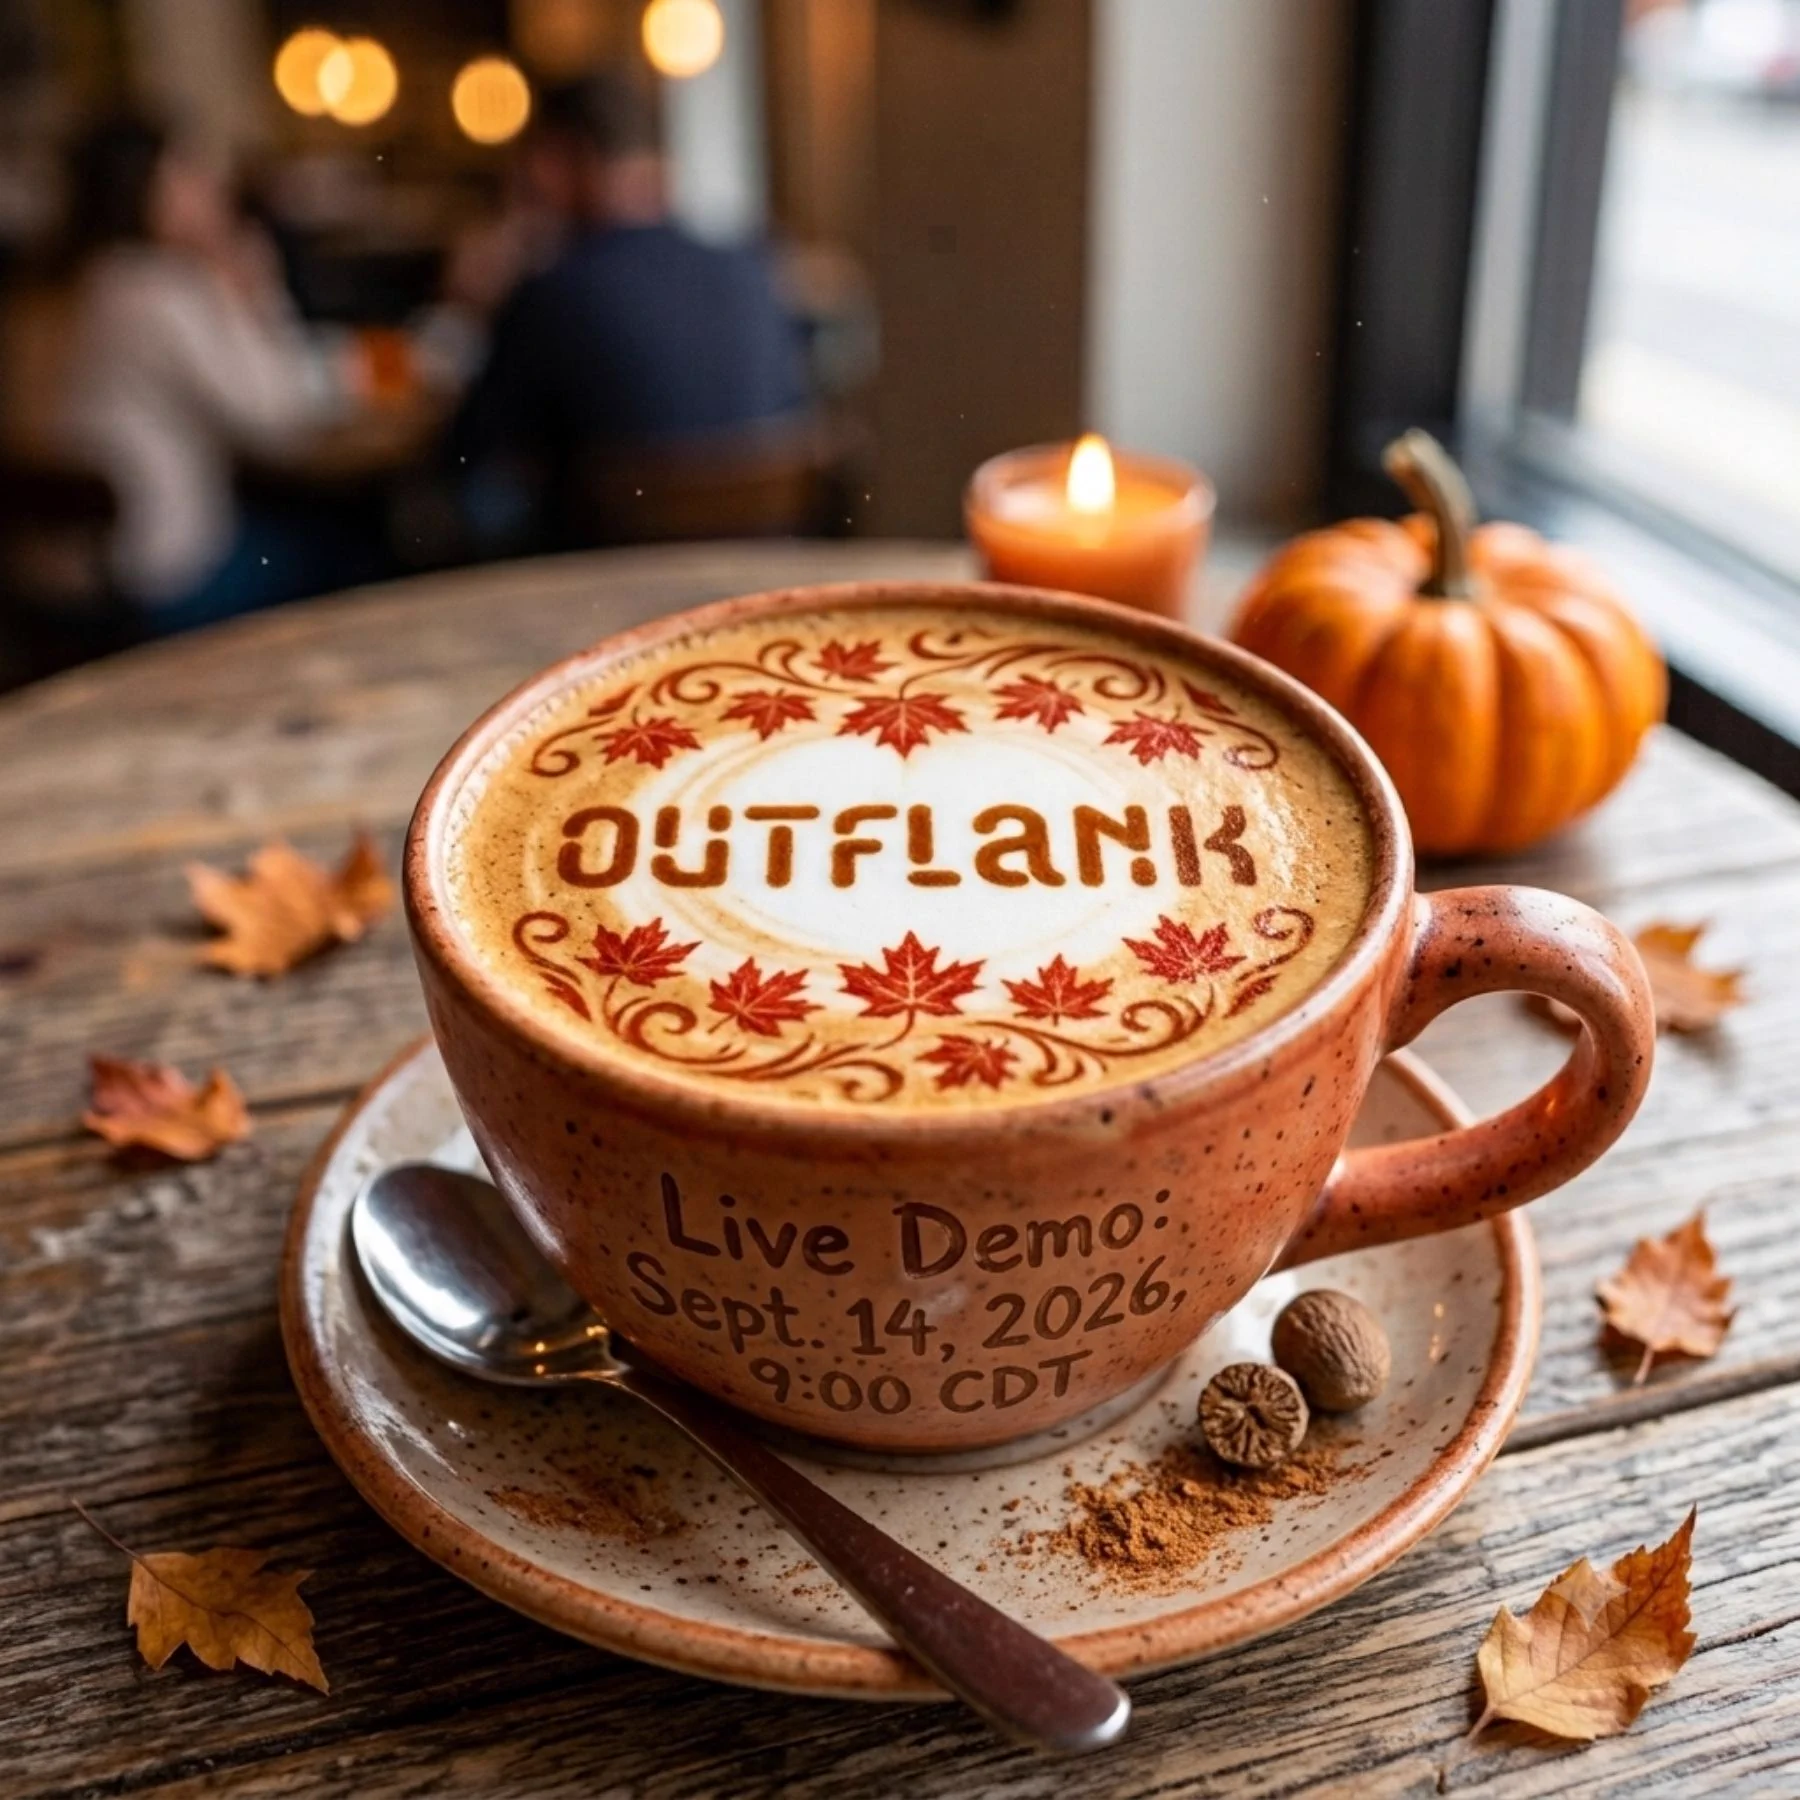
See what we're brewing at Outflank! No, it's not pumpkin spice security, but new tooling and tradecraft are always on the menu for OST. Join us on Sept 14 at 9:00am CDT for a live demo of our evasive offensive toolset for red teamers. Register now: https:// register.gotowebinar.c
> be me > get dm > "smelly i found goop" > wtf i love goop (malware) > sends like to GitHub > download > look inside .zip > instantly, at the blink of an eye, i recognize it > SmartLoader every single time, without fail, this is precisely how the SmartLoder malware campaign
hi @S3ntago What have you done here? I do not think this was an easy bug to exploit gitlab has been audited so many times Can you share the technical analysis ?
The DOJ restrained $52M in crypto from the Xinbi Guarantee scam marketplace in one day, four APTs shared a zero-day exploit kit targeting Windows and Chrome, and the NSA, CISA, and FBI accused at least six Chinese AI firms of extracting billions of tokens from Claude, GPT,
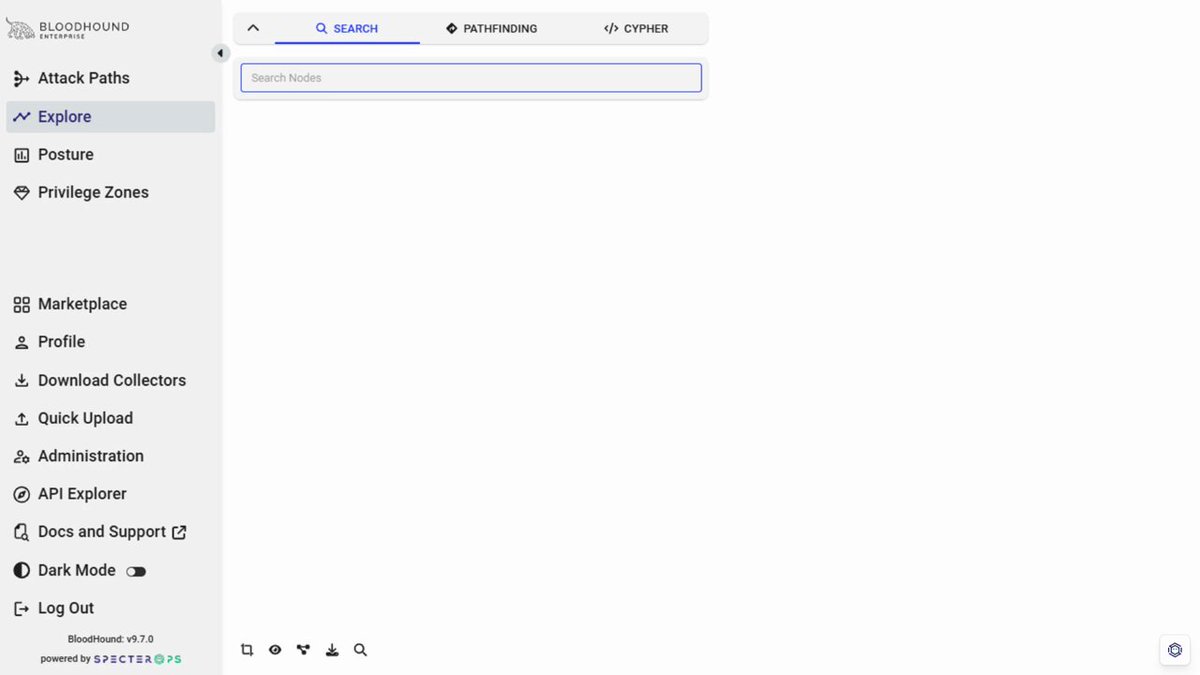
This works for all node types, and current built-in nodes can be found here: https:// ghst.ly/4cFpm1m, or under the respective extension (e.g., Github, Okta, etc.) here: https:// ghst.ly/4ip7MCw : 2/2
This is this particular SmartLoader payloads configuration GitHub. This link is safe to view. It is very silly. ae.log is the configuration SmartLoader uses. dec.log I couldn't figure out. It looks like it has another .exe inside of it encrypted and encoded as ASCII, but I
Working on my first ever video on goop (malware) reverse engineering and analysis. It is extremely ghetto, has lots of filler photos with pictures of cats I have saved on my desktop as I explain some concepts. I also don't have a fancy mic, a fancy machine, ... or anything
Posted by Ellenor Bjornsdottir on Sep 10 Hi Jeff, One and a half small nits: In this context, the correct replacement is «which», not «it». «Which» is - in this instance… | Posted by Solar Designer on Sep 13 It could be, but I see little similarity other than missing Date header and the use of an LLM. These could be fun to investigate, but …
OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers
The "major malicious attack" that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published by researchers Spencer Kitt…
How Threat Actors Are Turning Trusted AI Platforms Into an Attack Surface
Threat actors are abusing trusted AI platforms to host malicious content, poison search results, and trick users into installing malware. Huntress examines campaigns tar…
1.00general · 11 Sept, 15:33rapid7.comResearch
The Fraud Ecosystem: A Transition From Known Marketplaces to a Fragmented Environment
Introduction The surge in emerging threat actors directly correlates with the rapid escalation of victim counts and stolen financial resources. Simultaneously, this grow…
PaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited Flaws
PaperCut on Thursday released a new security maintenance release that replaces all previously published emergency patches that were pushed to address two security flaws …
Papercut AI Swarm Attack Heralds Changes for Cyber Kill Chain
From creating lab environments for staging and testing agentic attacks to reconnaissance to lateral movement and exfiltration, the most innovative attackers are widely i…