Generated 18/08/2026, 09:47. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources3
Tweets / X12
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
12 items
TheDFIRReport @TheDFIRReport
17 Aug, 19:05 · core
0.64
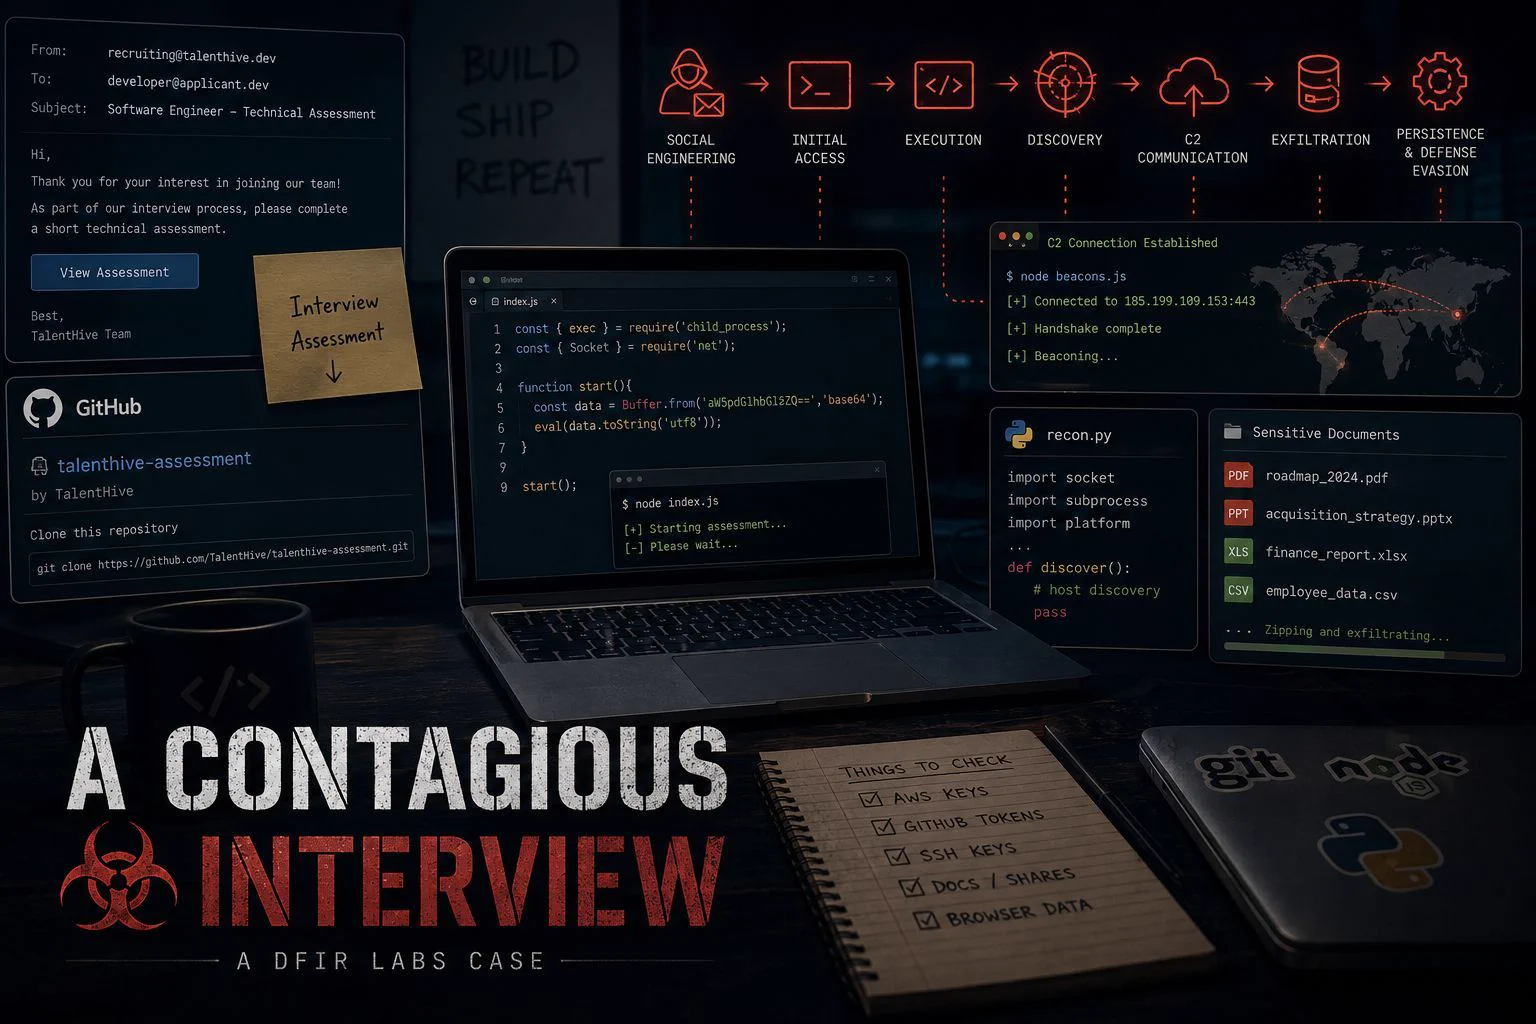
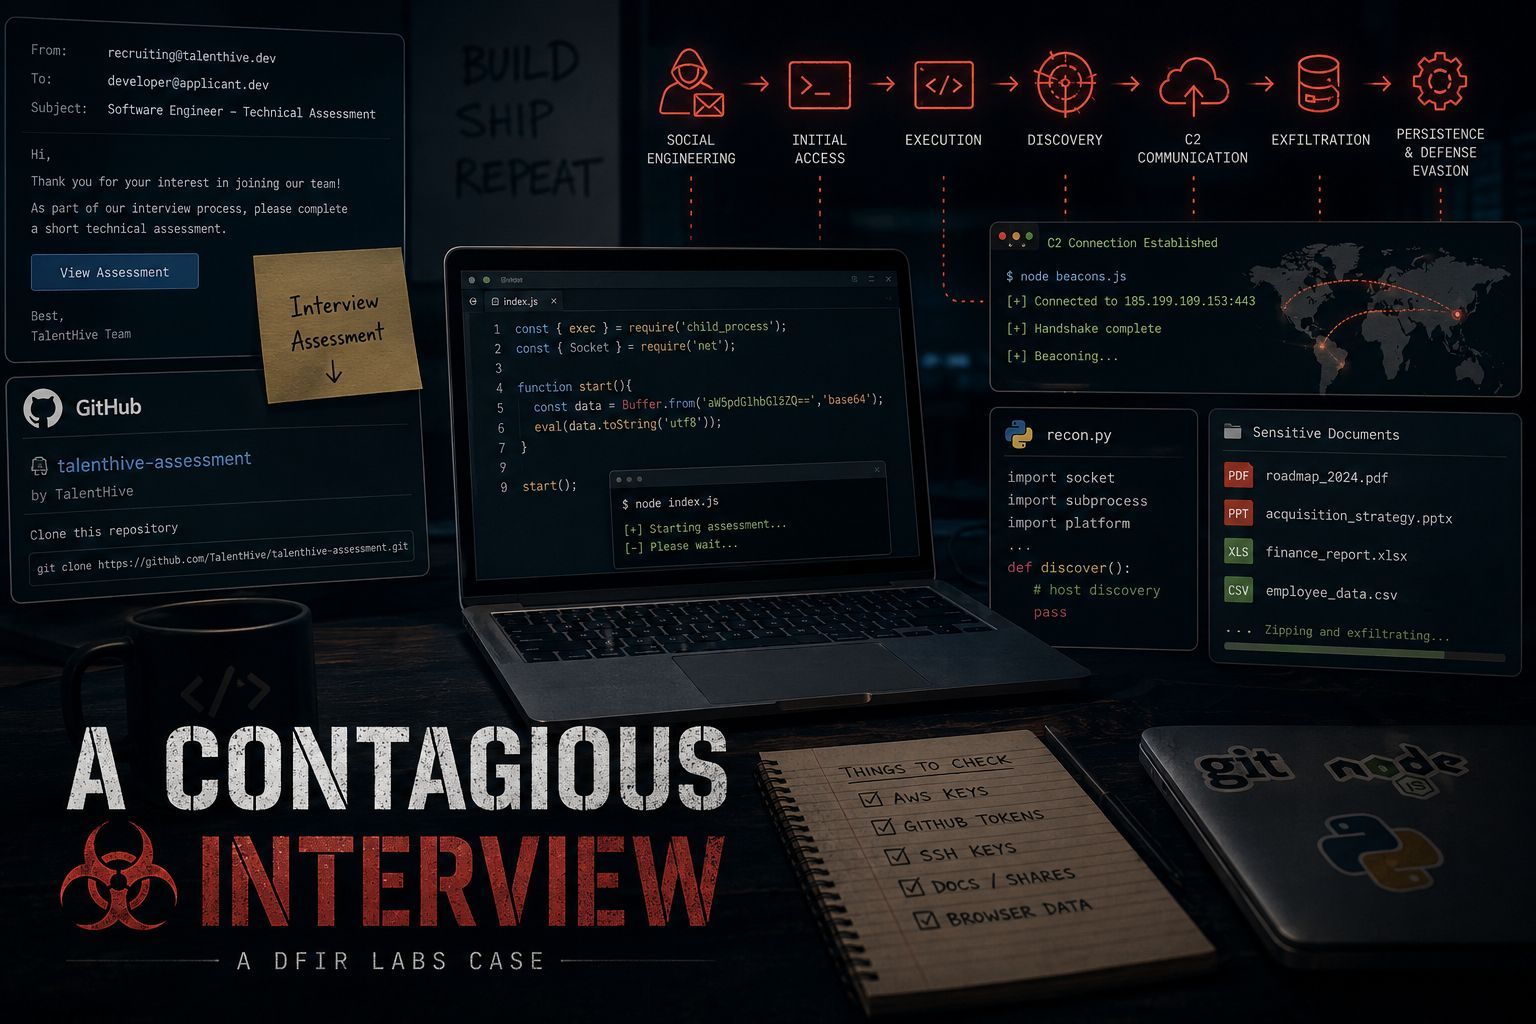
New DFIR Labs case: A Contagious Interview, Private Case #38413 A routine 'hiring assessment' turns into an endpoint compromise when a developer is social-engineered into cloning a malicious GitHub repo. Trace the campaign through obfuscated Node.js, Python payloads, C2, host
Also, it can be a 1,000,000,000x ROI if you exploit a drain bug in a DeFi protocol only few people know this, the ROI for $200 gpt/claude subscription is 1000x in cyber security.
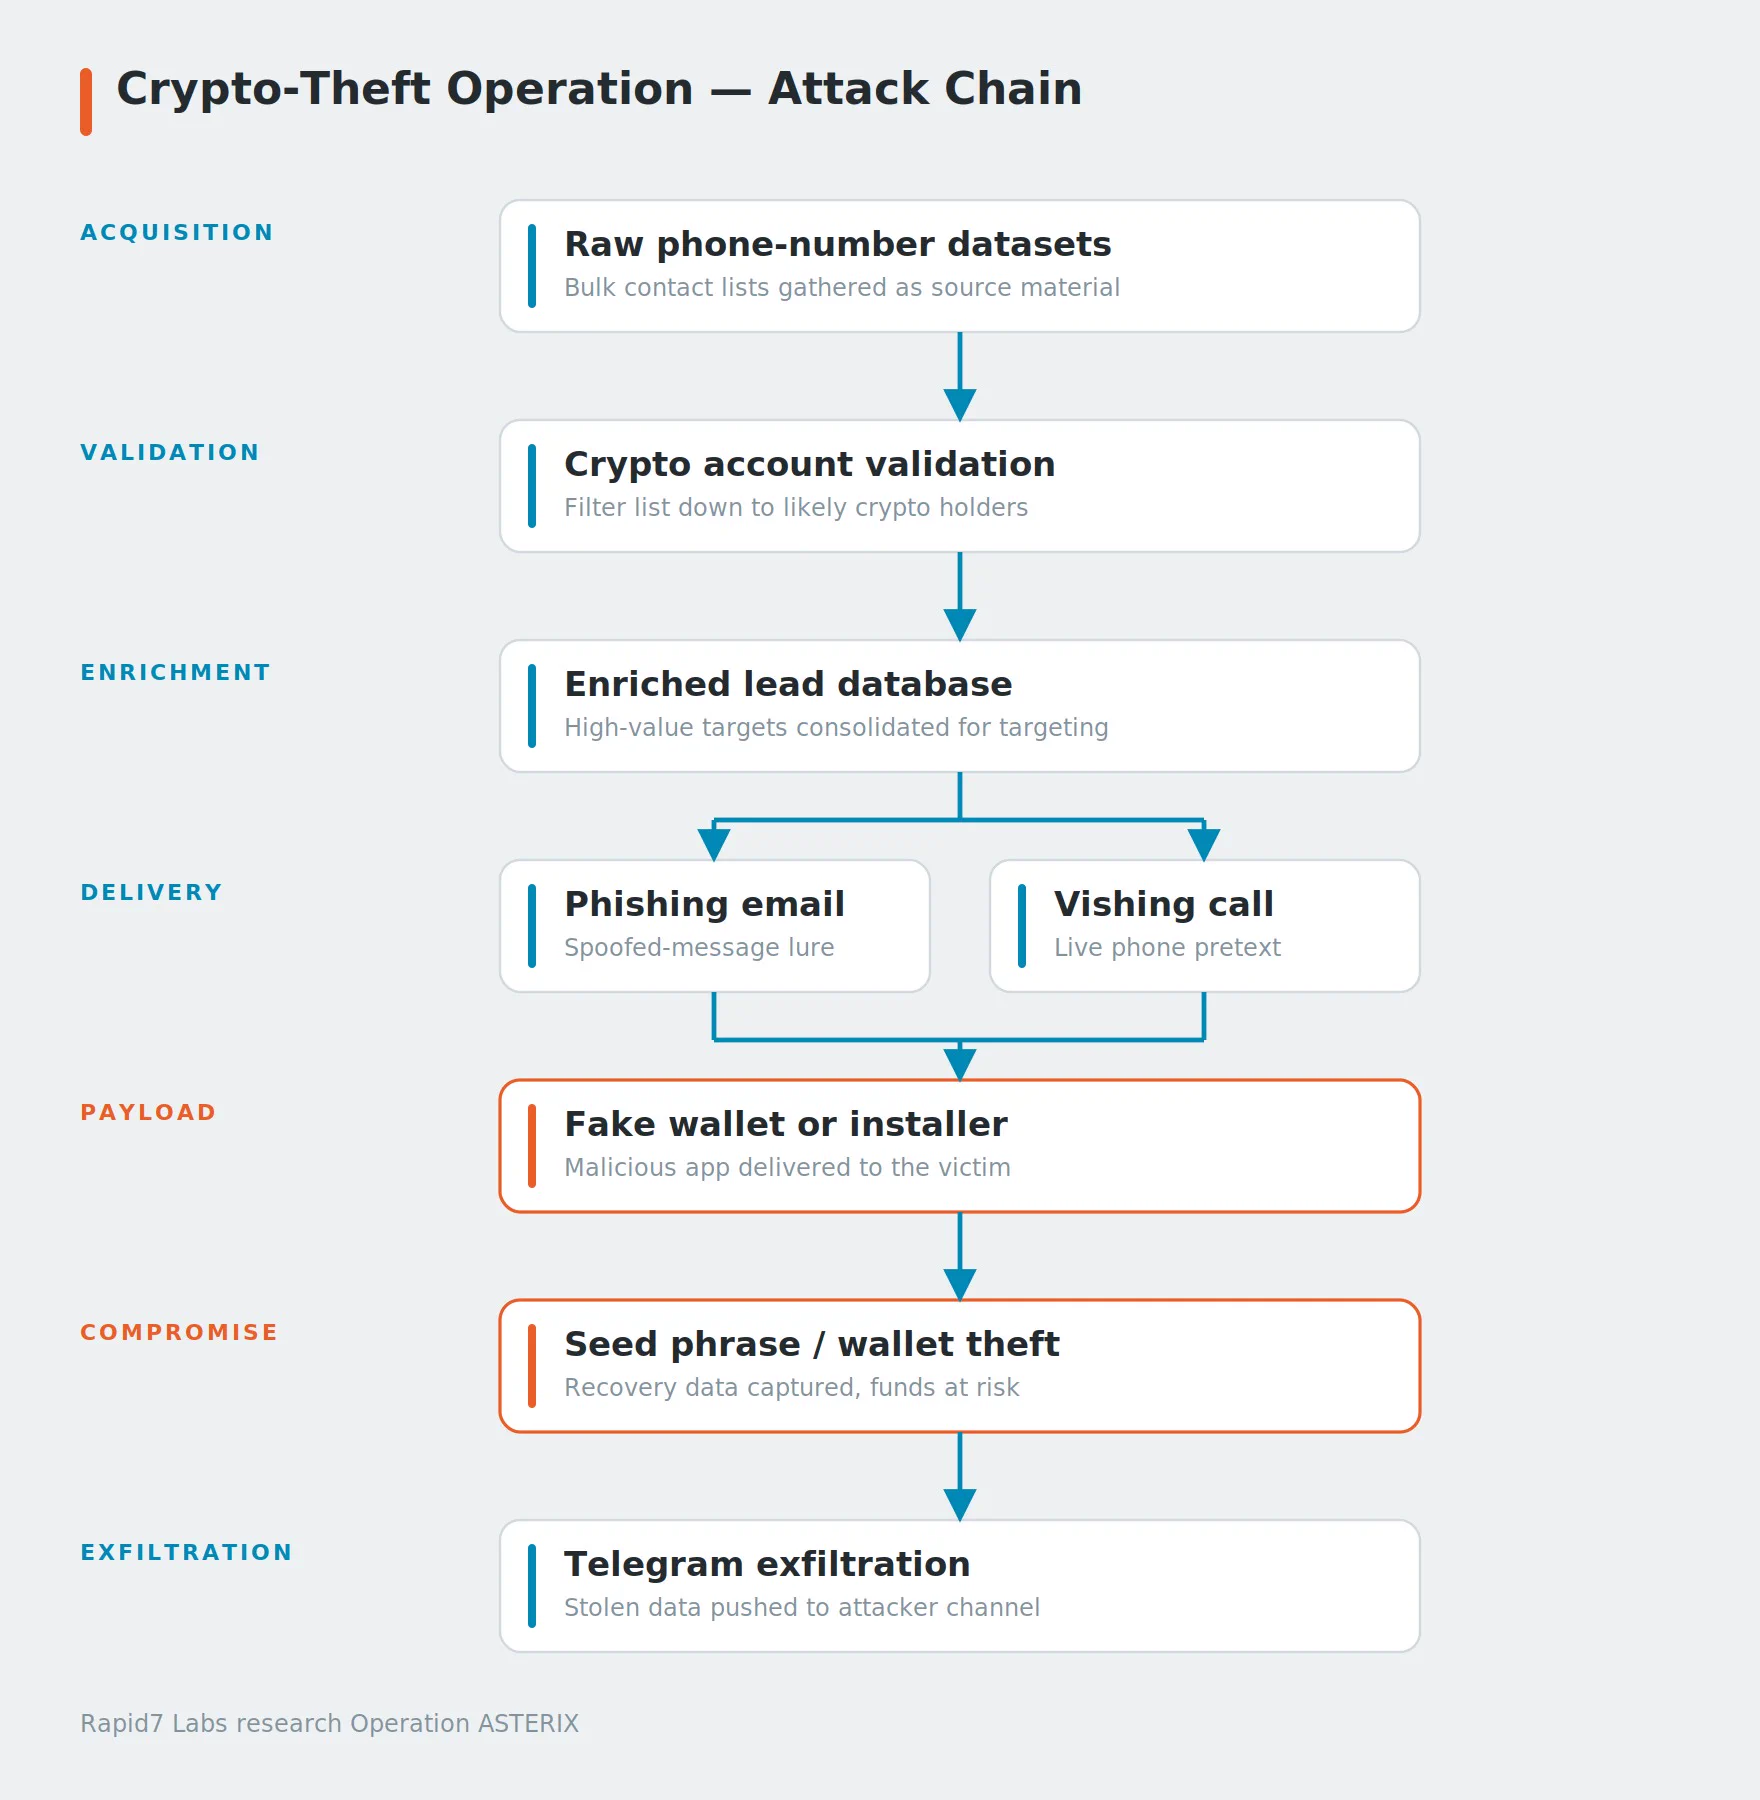
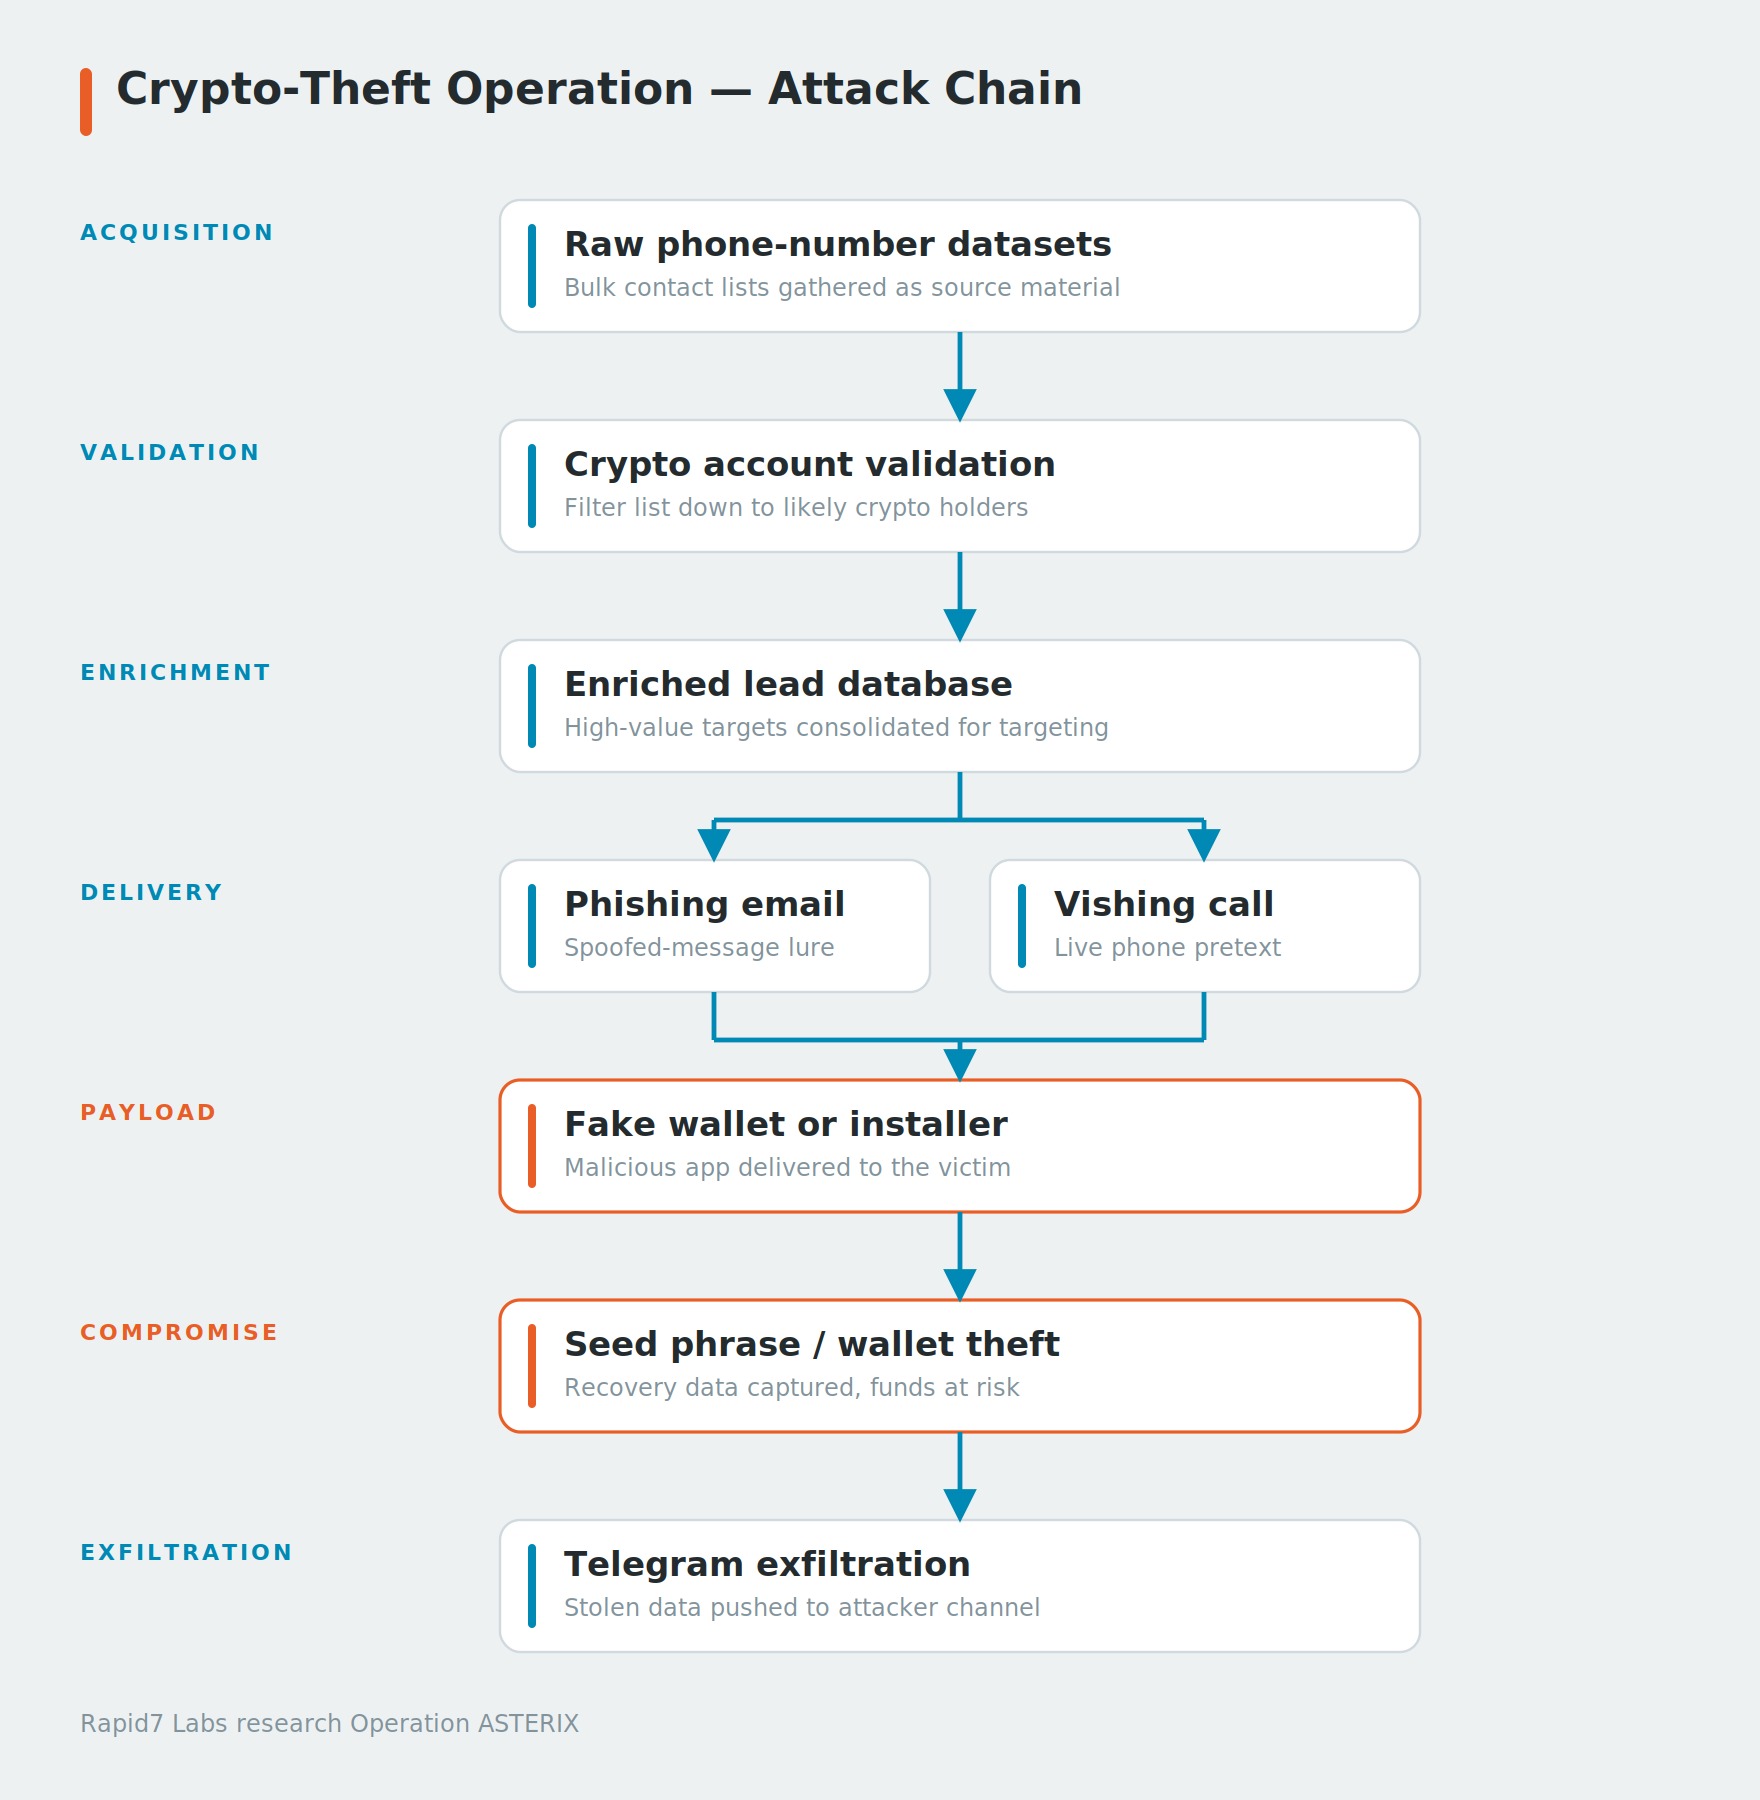
Rapid7 Labs recently uncovered a crypto scammer's working environment via a misconfigured web directory, exposing raw phone-number datasets, phishing panels, voice-dialing scripts, counterfeit wallet builds, and more. Full technical analysis here: https:// r-7.co/4xban7K
One compromise. A much bigger blast radius. Software Supply Chain Security for Red Teamers explores how attackers abuse trust across the software supply chain & the defenses designed to stop them. Start learning: https:// academy.specterops.io/software-suppl y-chain-security-for-
We just launched @HackingHub’s latest course: “ @CaidoIO for Hackers” Learn to maximize Caido: from intercepting and replaying traffic to fuzzing, workflows, plugins, and chaining real bugs. 18 modules. 52 lessons. Hands-on labs. Lifetime access. Enroll
Karanbir Singh, CrowdStrike VP of Product, Cloud Security, explores what’s new and what’s next for Falcon Cloud Security. As cloud-conscious adversaries evolve their tradecraft and AI reshapes the security landscape, he’ll share where the market is headed, how Falcon Cloud
Business logic flaws are where AI security testing gets humbled. No CVE to match, no pattern to grep for, just workflows that behave badly in ways only context reveals. @ehrishiraj talks through what LLMs can and can't do here on the latest Application Security Weekly. Listen
Can we teach AI to reason through detection evidence before making a triage verdict? Our latest research says yes. We’ve developed a reasoning-enabled triage model that significantly outperforms general-purpose models when evaluating real-world Windows endpoint detections. By
Are your security tools missing threats hiding under the radar? Watch our latest video to learn how Cisco Talos Threat Hunting combines AI and expert human analysis to uncover sophisticated adversary activity that traditional detection methods often miss: https:// youtu.be/8yUXRI
Or even the AI companies doing cool Offsec work? Who are the team's you'd say are doing the coolest stuff in the AI RedTeam space at the minute? I'm struggling to keep track of where all the cool releases are coming from
⚡ Weekly Recap: VMware Exploits, Windows 0-Day, MCP Attacks, Browser Hijacks and More
The expensive attacks are not always the clever ones. This week had plenty of proof. Exposed services got hit, old bugs found fresh use, browser sessions became attack p…
1.00exploit · 17 Aug, 01:42seclists.org
Re: Fwd: OpenZFS Linux open zpool manipulation and escapes via unprivileged userns
Posted by Aaron Rainbolt on Aug 16 Holy AI agent braindump, Batman. Is there perhaps a standard vulnerabiilty report version of this? Or a GitHub repo that can be cloned…
0.99general · 17 Aug, 13:58thehackernews.com
How MCP Servers Can Expose Enterprise Secrets
MCP servers can expose enterprise secrets through plaintext configuration files, over-permissioned access and prompt injection, often before security teams even know the…