Generated 25/08/2026, 09:43. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources2
Tweets / X13
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
13 items
Unit42_Intel @Unit42_Intel
24 Aug, 17:06 · secondary
0.57
Identity phishing via collaboration tools exploits trust in internal channels. Attackers send direct messages linking to proxy servers to harvest credentials and MFA tokens in real time. Read our research to protect your workforce: https:// bit.ly/4gKbTHW
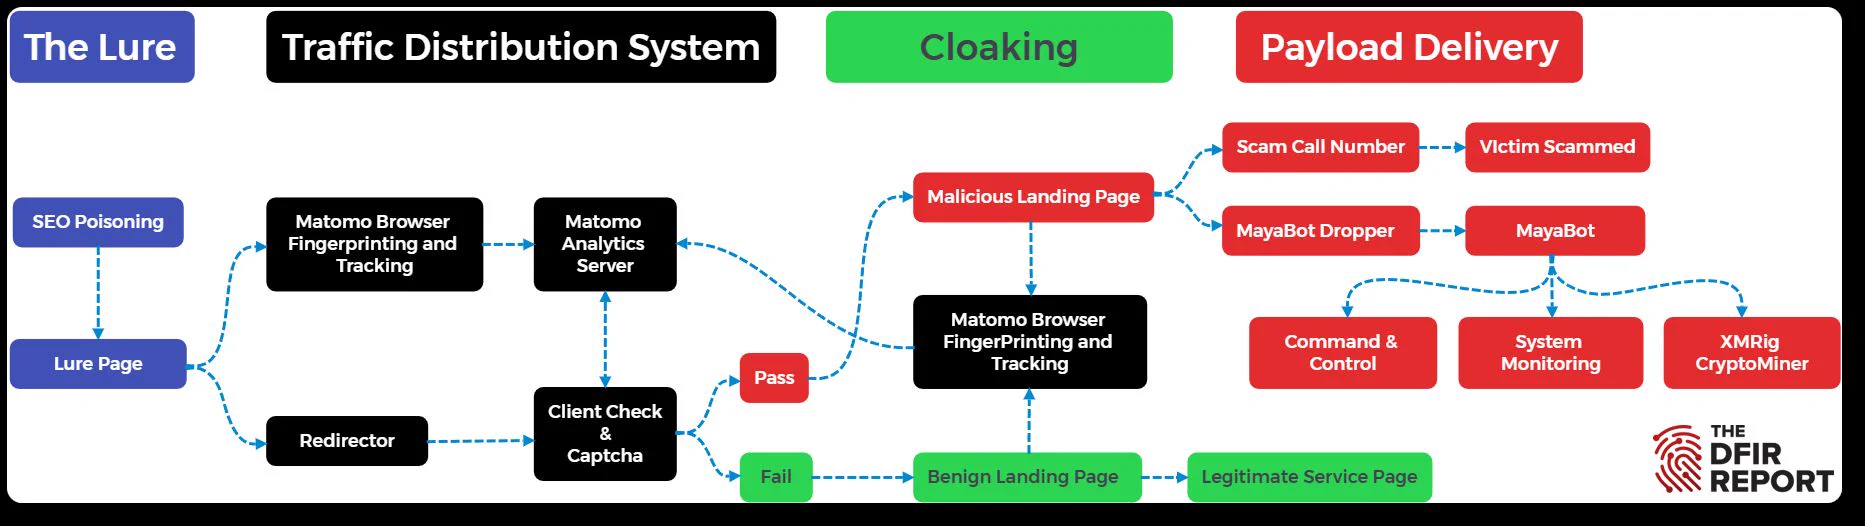
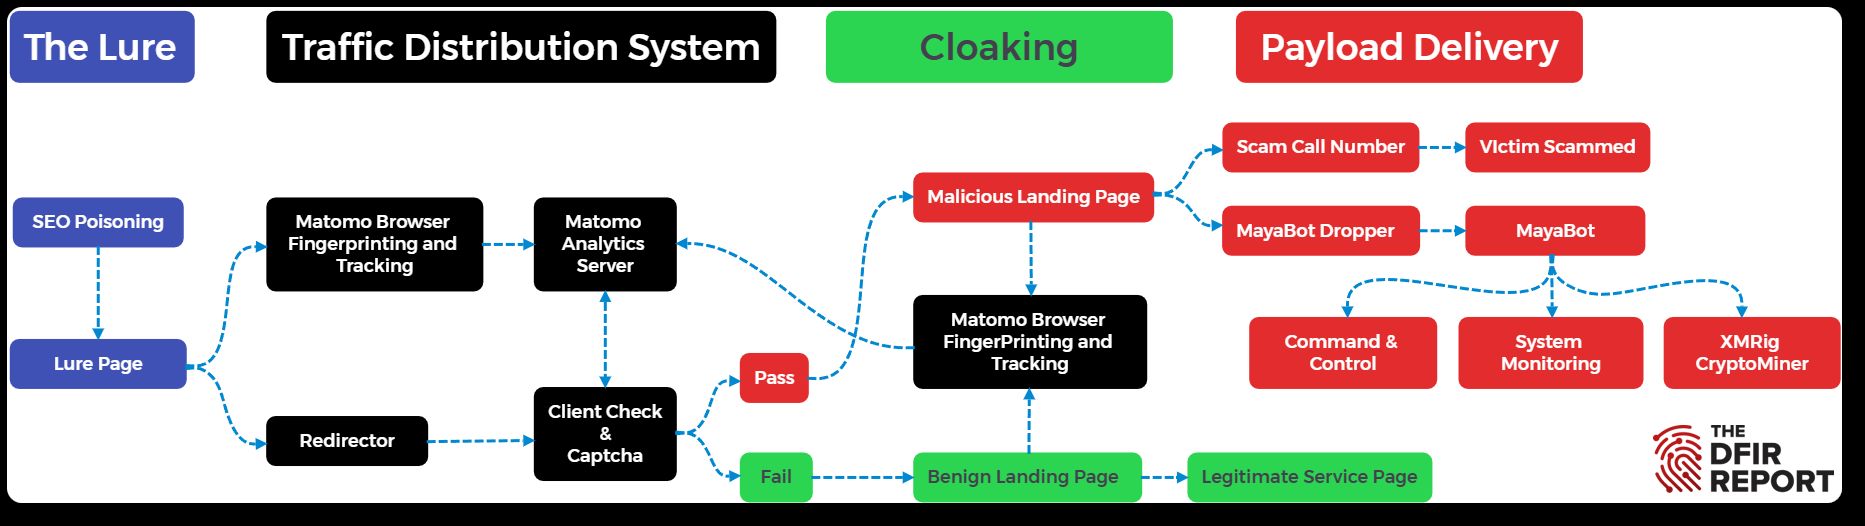
New report: BengalSEO Part 1: Anatomy of the Operation We are mapping BengalSEO, a sprawling SEO poisoning and tech-support-scam operation running since at least 2015 out of Rajasthan, India, and the custom malware behind it, MayaBot. Part 1 breaks down the full anatomy: a
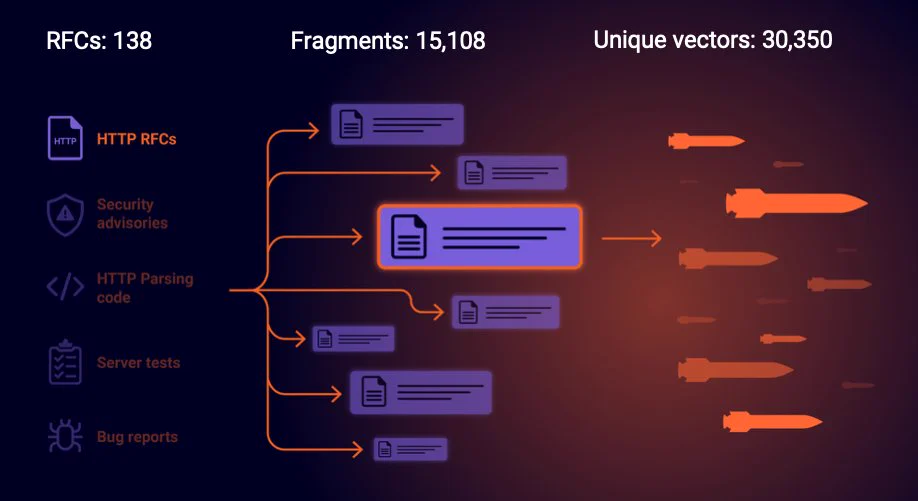
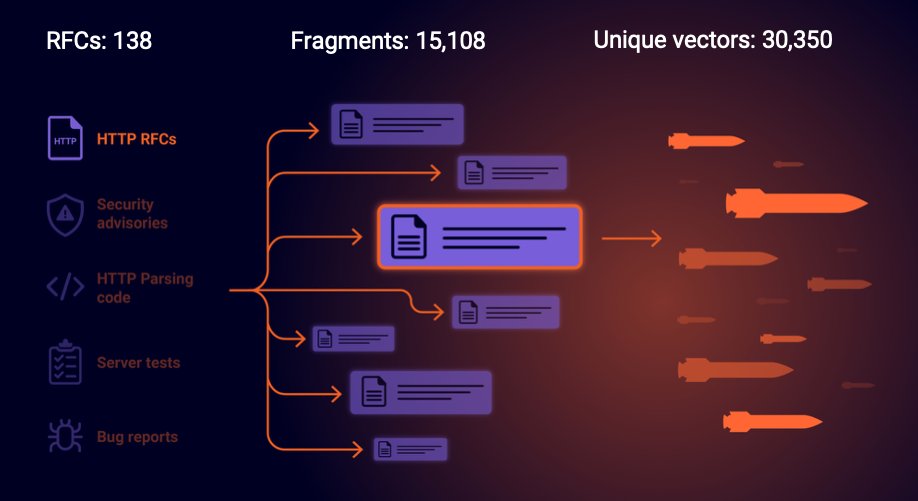
Next month I'll present my latest research live at @SEC_T_org in Stockholm, Sweden! This will be the final live edition of "Can AI Do Novel Security Research? Meet the HTTP Terminator". It's also my first time attending SEC-T, can't wait to meet you all!
What's the worst thing an attacker could do with a list of hardware wallet customers? Our first thought was phishing. Then Kendrick (and Claude) pointed out something we hadn't considered: physical theft.
As a person who has actively told a company to "fuck right off" when asked to perform a "psychometric evaluation" (not sure if this was the answer they wanted)... If a company ever tests you like this... RUN!! SITUATION BREWING: Anthropic is asking prospective employees in cultur
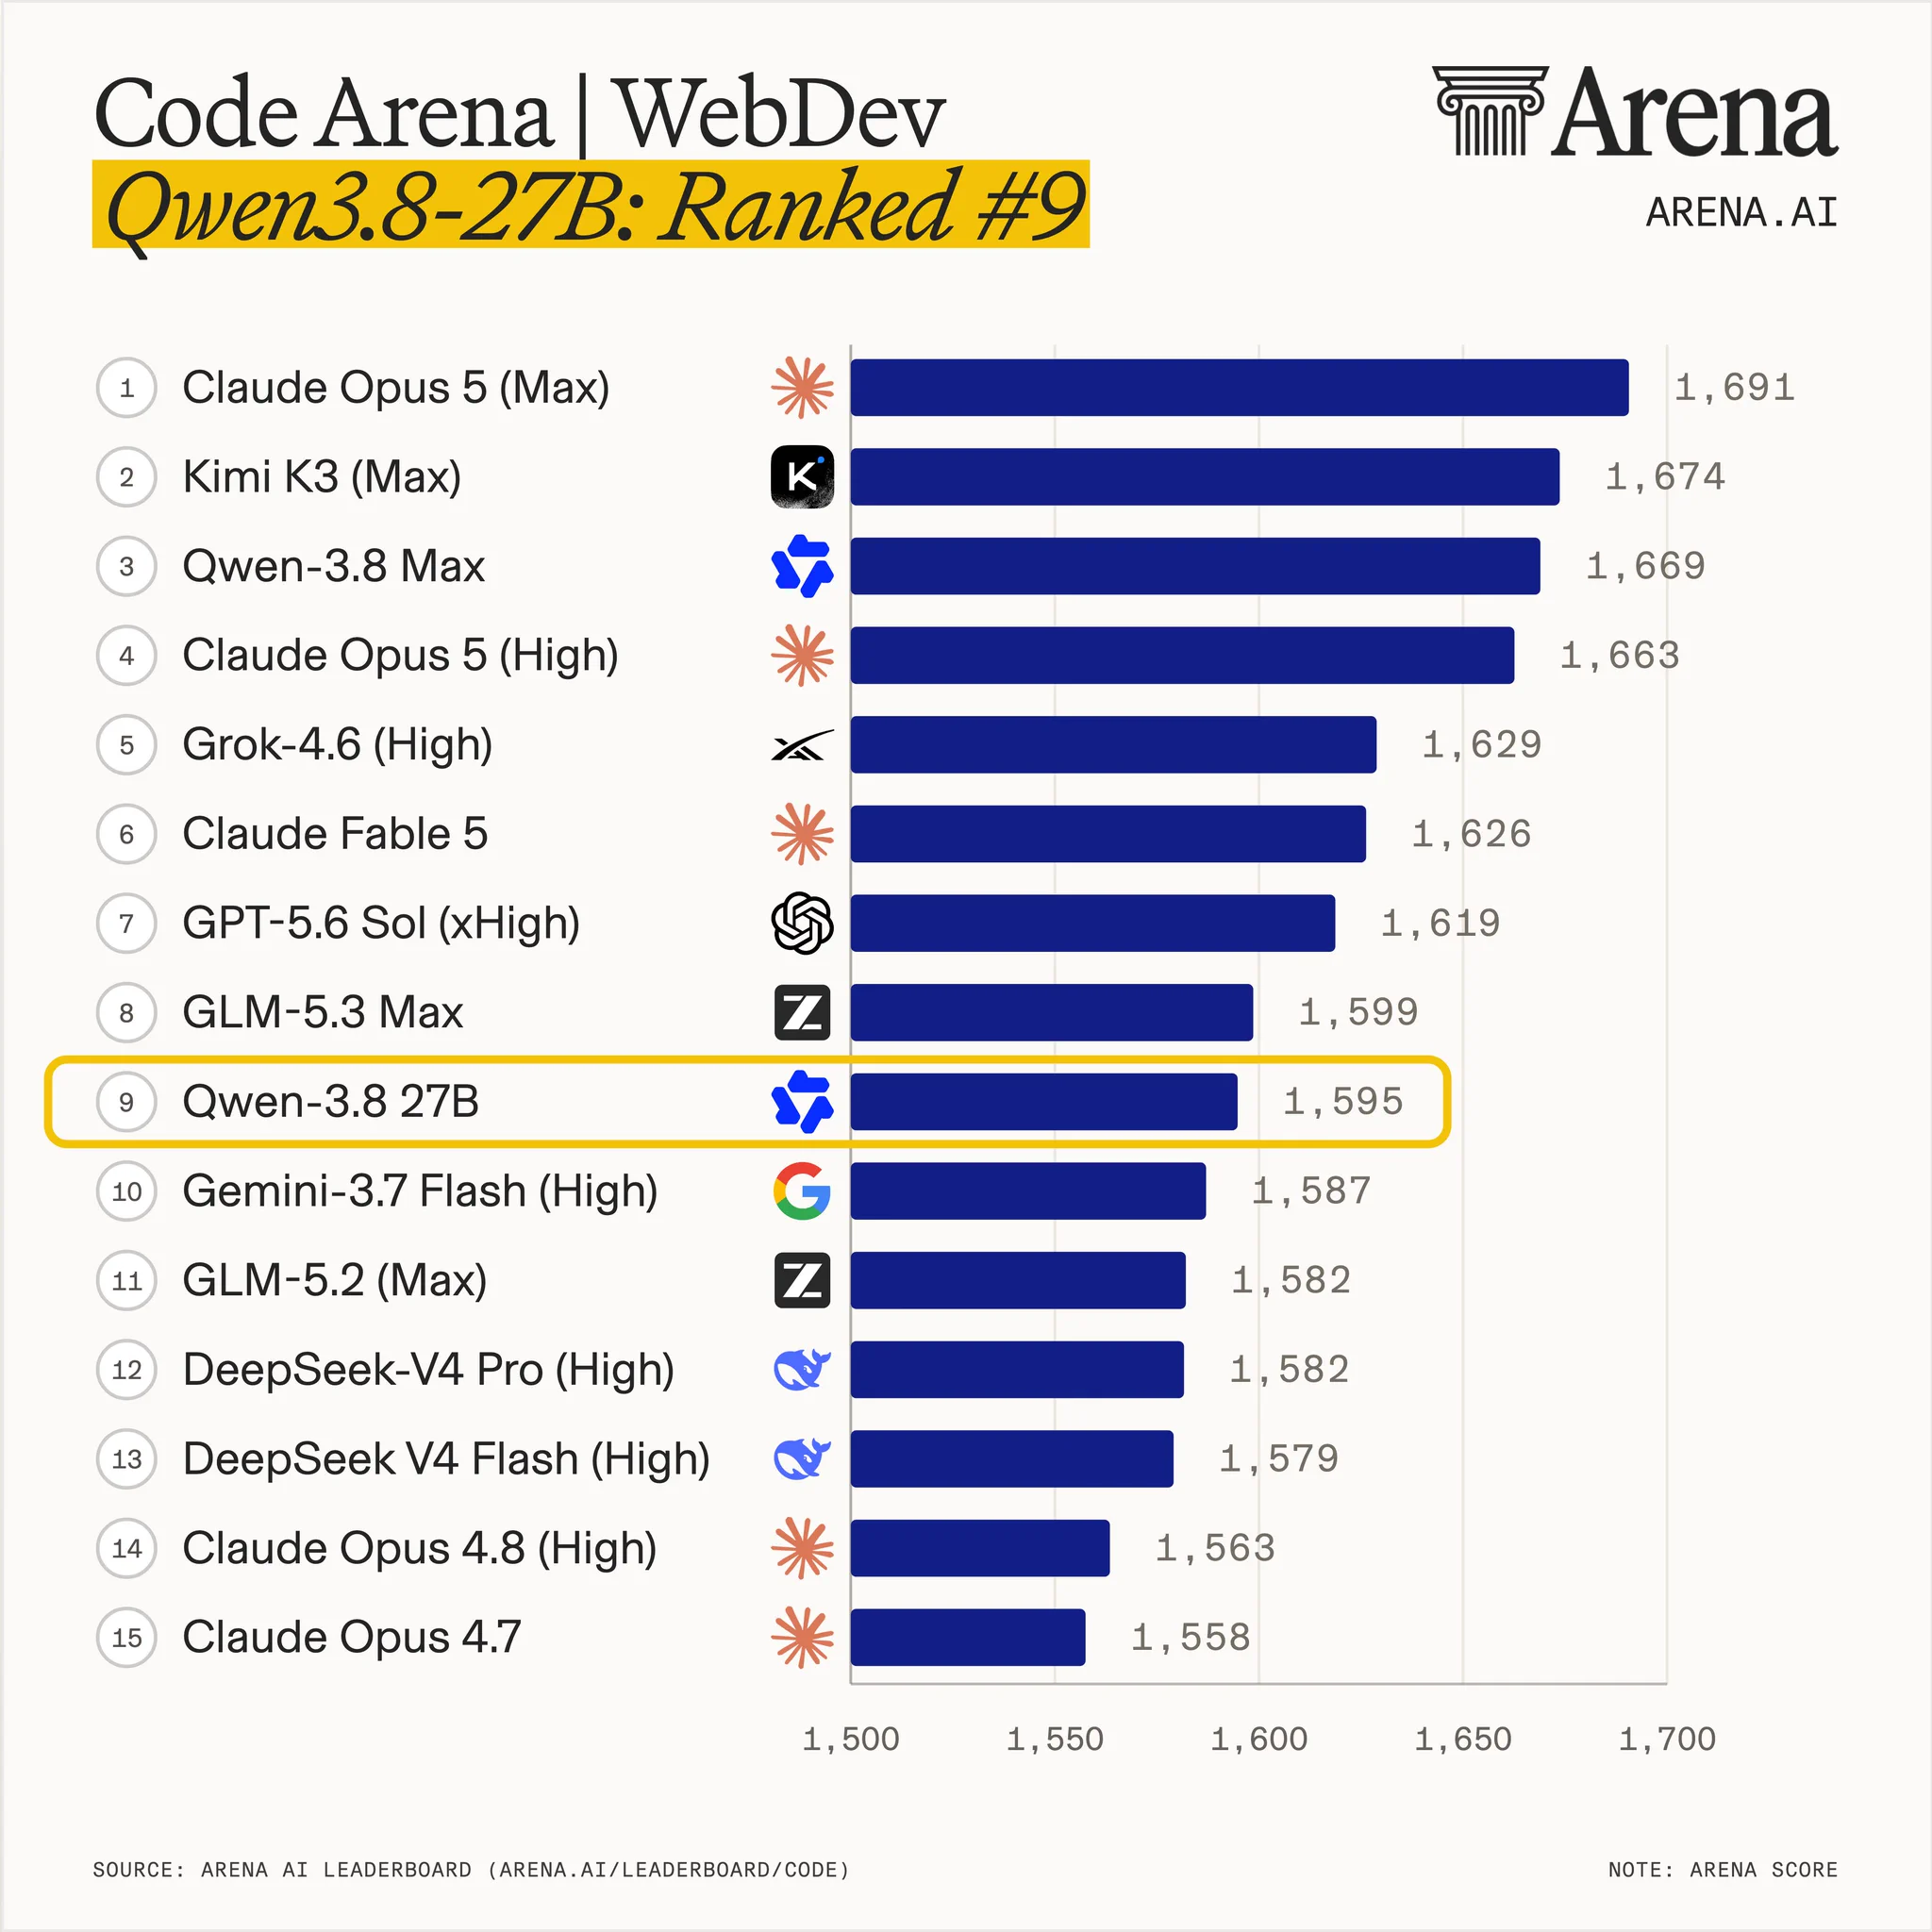
Open weight models killing it in the rankings, that is awesome Qwen3.8-27B by @Alibaba_Qwen just landed in Code Arena: WebDev at #9 overall with 1595 pts. The 27B variant ranks even higher in these categories: - #6 Consumer Product (1587) - #7 Brand & Marketing (1627) - #8 Gaming
Finally got to sit down with @wunderwuzzi23 and he walked me through one of his bugs. CSP bypass to exfil data out of Microsoft Copilot, made persistent with memory poisoning. new episode is live https:// youtu.be/3LulhVjbT0E
It's CHALLENGE O'CLOCK! Capture the flag before Monday the 31st of August Win €400 in SWAG prizes We'll release a tip for every 100 likes on this tweet This month's challenge was brought by us! https:// challenge-0826.challenges.intigriti.io
Posted by Solar Designer on Aug 23 Hi, Anmol Bakshi brought the below with original Subject line saying "BusyBox dpkg applet: OS command injection -> root RCE (CWE-78)" …
0.89exploit · 24 Aug, 07:34seclists.org
Re: Re: Emacs zero-click local command execution via TRAMP
Posted by Sam James on Aug 23 nightmare.yeah27 () aceecat org writes: https://gitweb.gentoo.org/proj/emacs-patches.git/tree/emacs/27.2/17_all_tramp.patch https://gitweb.…