Generated 24/08/2026, 09:41. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources7
Tweets / X8
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
8 items
TheDFIRReport @TheDFIRReport
21 Aug, 19:35 · core
0.86
Train your AI on what attackers actually do, not a simulation. AI Training Ground gives you over 100 real intrusions, system and network logs, memory dumps, malware, and IOCs, capturing real threat-actor actions well beyond initial access: lateral movement, credential theft,
Keycloak is vulnerable to a critical unauthenticated account takeover (CVE-2026-18963) I reproduced the bug locally; interesting one (power of LLM, I think) https:// github.com/keycloak/keycl oak/issues/51833 …
The U.S. charged 17 Iranians for stealing $3.4B in intellectual property, Medusa ransomware crossed 500 critical infrastructure victims, and a critical Windows IKE RCE flaw is now being actively exploited in the wild. This is the Good, Bad & Ugly.
Picked up the @opencode Go plan ($5 then $10 a month), nice way to play around with open source models and see what they can do vs the big two. The multipliers are useful to look out for as well, smashing Muse Spark 1.2 for my new blog post! https:// opencode.ai/go
Some people live this stuff. Just sayin. Inspired by @uwu_underground … @arcanuminfosec is releasing our first EP! Our Prompt Injection Taxonomy (PIT) EP has three tracks! 1. Prompt Injextion 2. </system> 3. Link Injection Lullaby SoundCloud Link in comment, enjoy!
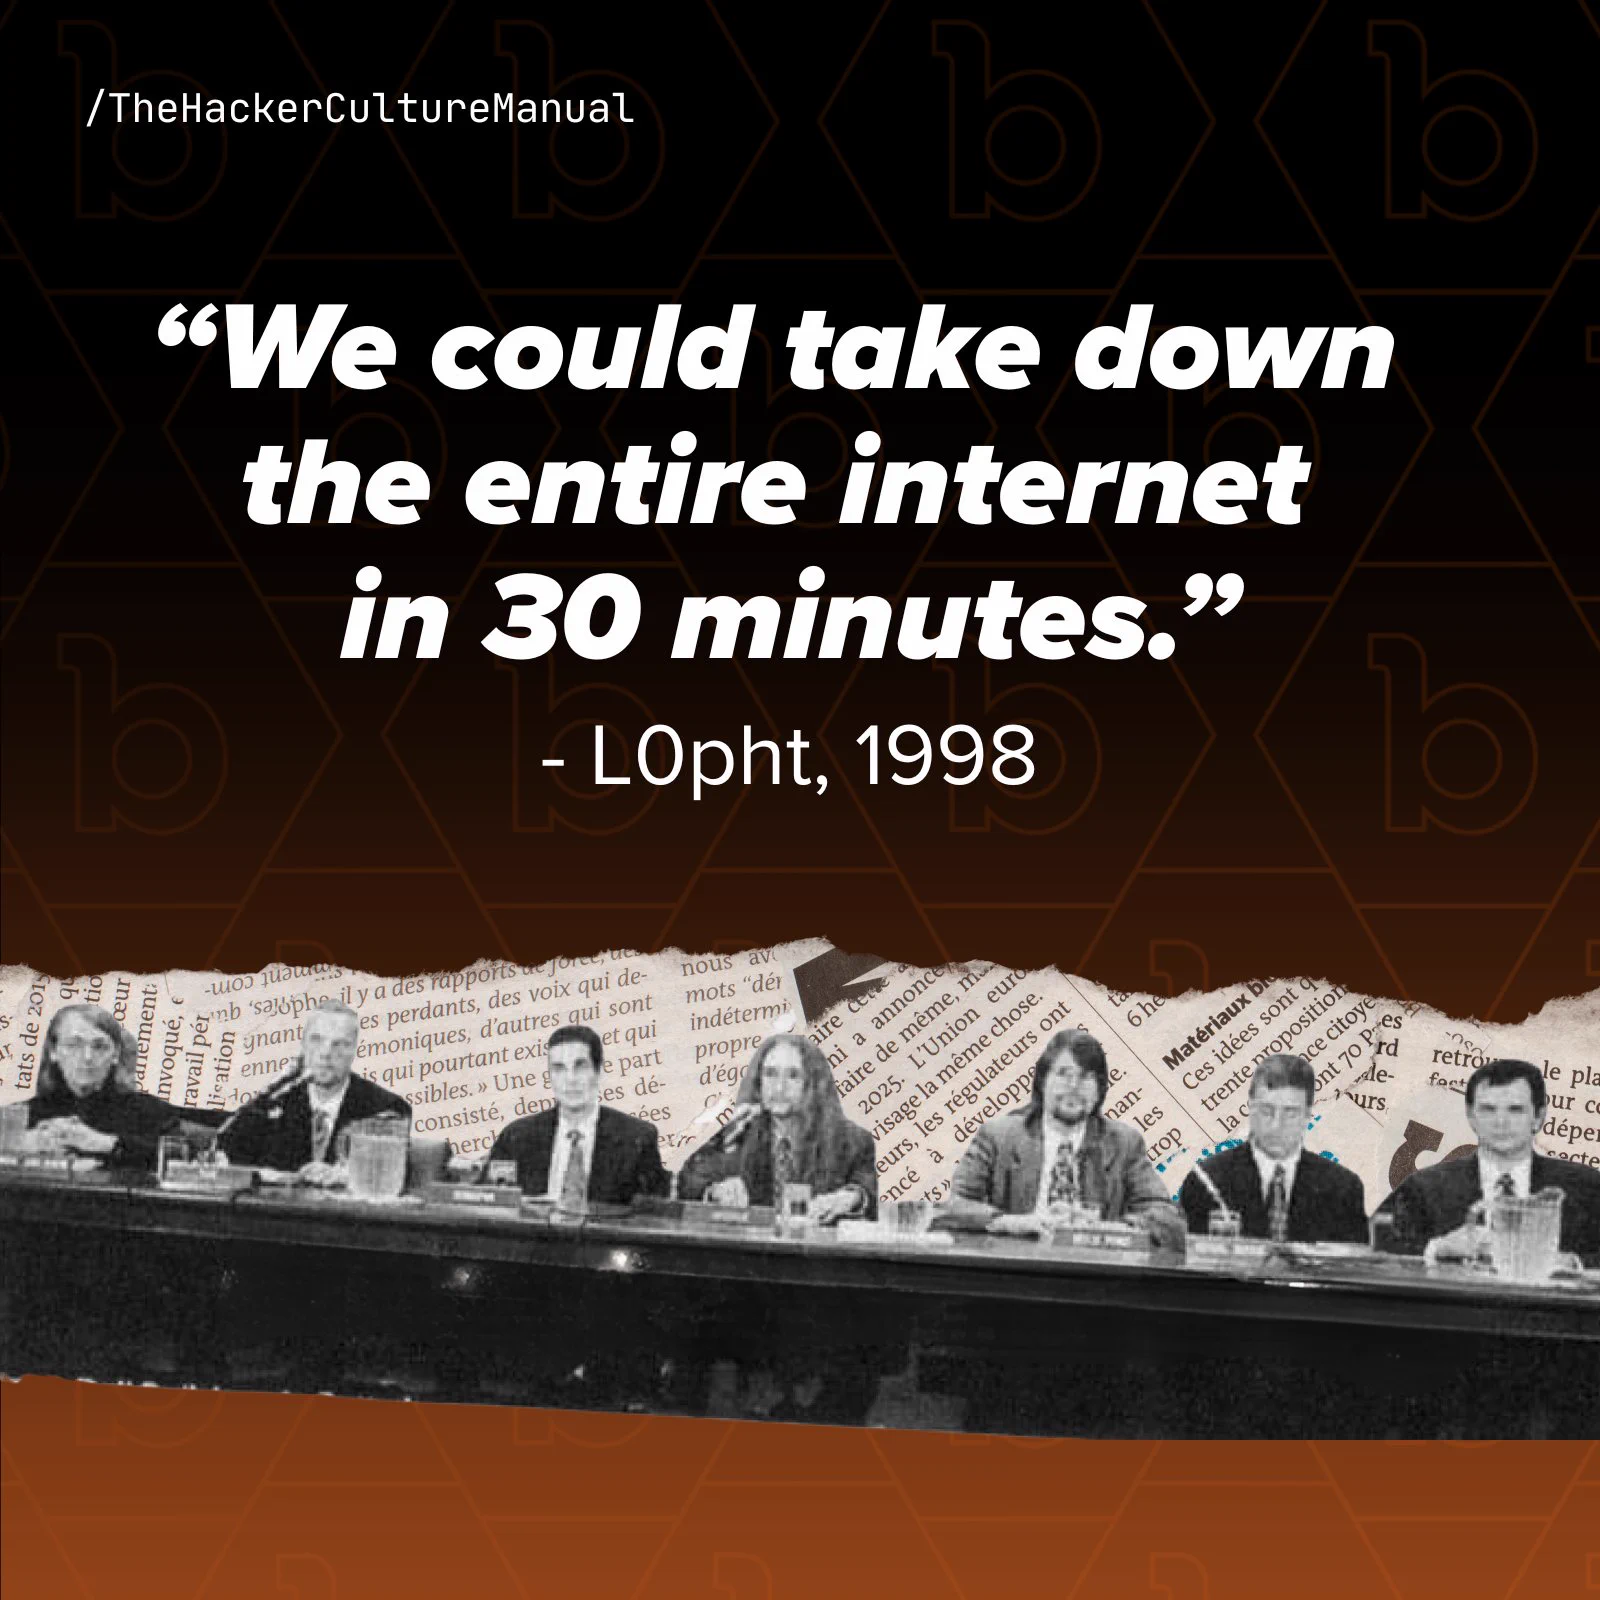
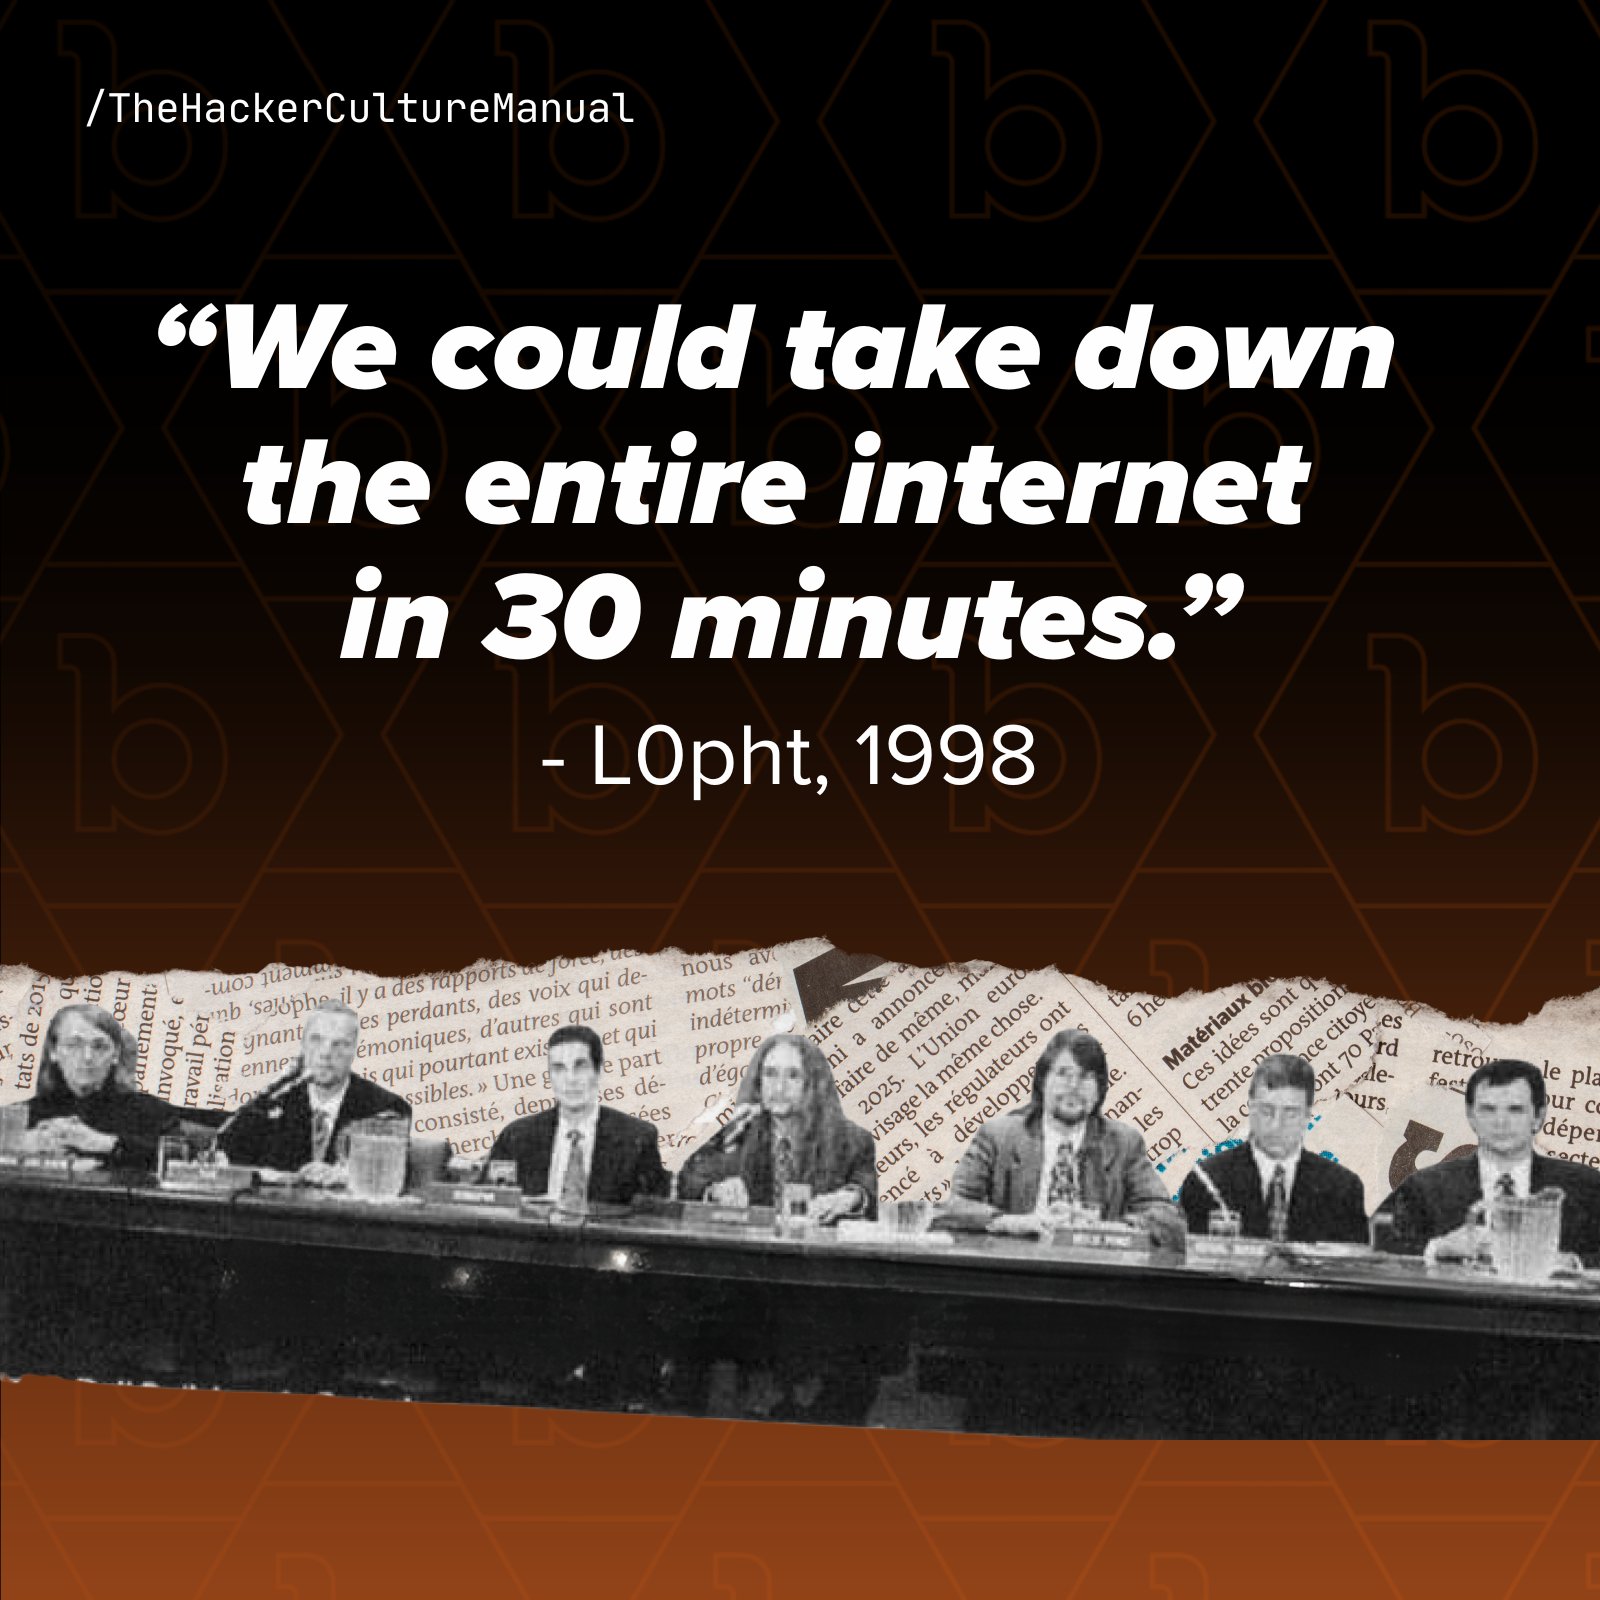
The most effective hack in history was not a fancy technical exploit, it was a congressional testimony. In 1998, members of L0pht sat in front of the US Senate and told them they could take down the entire internet in 30 minutes. They did this to encourage the government and the
Last days of summer, first look at what's new in OST. We're closing out the season with a live look at Outflank Security Tooling on August 24th. Register now: https:// register.gotowebinar.com/register/77419 30108235047765?source=X …
New SynkLoader malware pushed in Microsoft Teams phishing campaign
A previously unknown malware family dubbed SynkLoader is being distributed in Microsoft Teams phishing campaigns to steal credentials via a fake lock screen. [...]
Microsoft patches critical Entra ID vulnerability (CVE-2026-69836)
Microsoft has patched a critical remote code execution vulnerability (CVE-2026-69836) in Entra ID, initially reported to have been exploited in the wild. Entra ID is Mic…
Microsoft patches max severity code execution, privilege escalation flaws
Microsoft has patched a maximum-severity vulnerability in the Entra ID identity and access management (IAM) platform that has been exploited in attacks. [...]
1.00influence_op · 21 Aug, 12:03euvsdisinfo.eu
From denial to exploitation: how the Kremlin has adapted its climate disinformation
In the latest wave of climate-related narratives spread by the Kremlin, climate change is a vehicle to reinforce familiar disinformation tropes: the alleged authoritaria…
Microsoft Patches Exploited Entra ID Vulnerability
A total of 22 patches were releaased, a majority for code execution, privilege escalation, and information disclosure vulnerabilities. The post Microsoft Patches Exploit…
Microsoft Entra ID Flaw (CVSS 10.0) Exploited in Wild, Allows Remote Code Execution
Microsoft on Thursday warned of a maximum-severity security flaw in Entra ID that it said has been exploited in the wild, but noted that no customer action is required. …
0.95exploit · 22 Aug, 08:062 mentionsseclists.org
Re: Emacs zero-click local command execution via TRAMP
Posted by Sean Whitton on Aug 21 Bas Alberts of the GitHub Security Lab discovered a local command execution vulnerability in GNU Emacs 30.2 onwards, and possibly earlie… | Posted by nightmare . yeah27 on Aug 21 Emacs has no security releases; do we have any idea if this will be fixed in Emacs 31?