Official intelligence summary

HAIJA INTEL REPORT

Generated 10/08/2026, 09:36. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources2
Tweets / X13
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.

Tweets / X

13 items
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
08 Aug, 12:01 · core
0.84
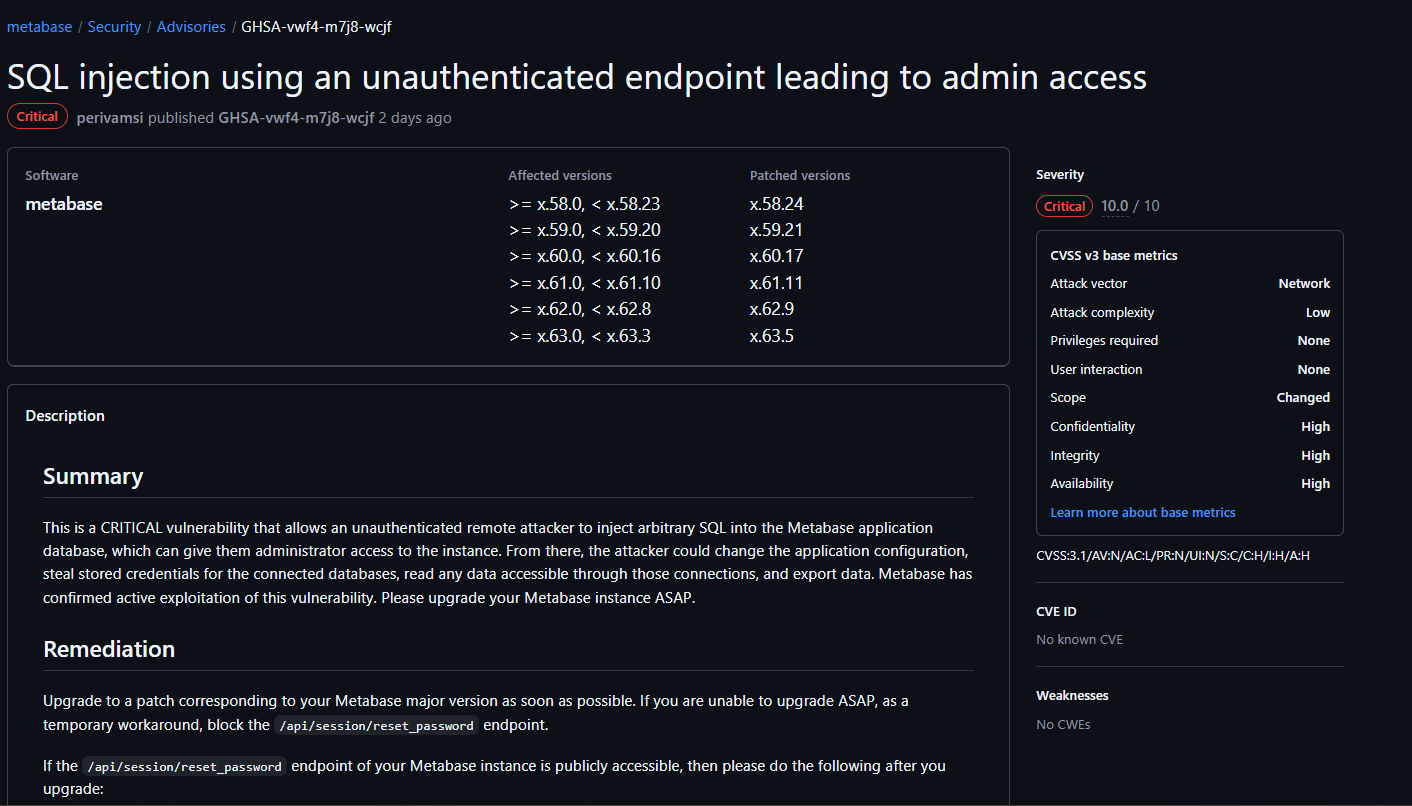
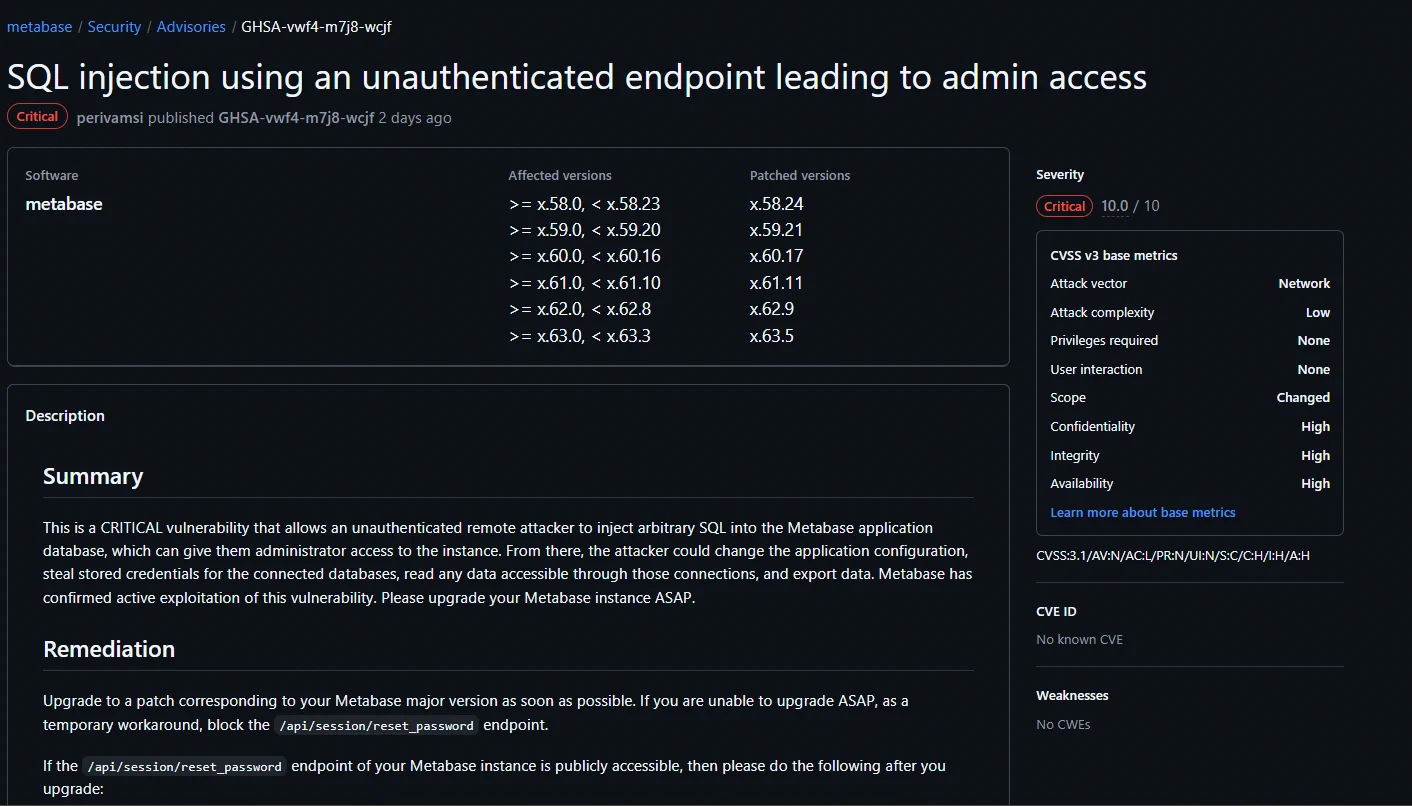
Metabase patched a 0-day that was exploited in the wild without a CVE https:// github.com/metabase/metab ase/security/advisories/GHSA-vwf4-m7j8-wcjf … https:// metabase.com/blog/security- update …
tweet mediatweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
07 Aug, 23:13 · core
0.74
unpatched !! seems like the is out of the here's our poc for MariaDB 13 RCE, currently still unpatched: https:// github.com/v12-security/p ocs/tree/main/mariadb …
@_dirkjan avatar
_dirkjan @_dirkjan
07 Aug, 20:45 · core
0.62
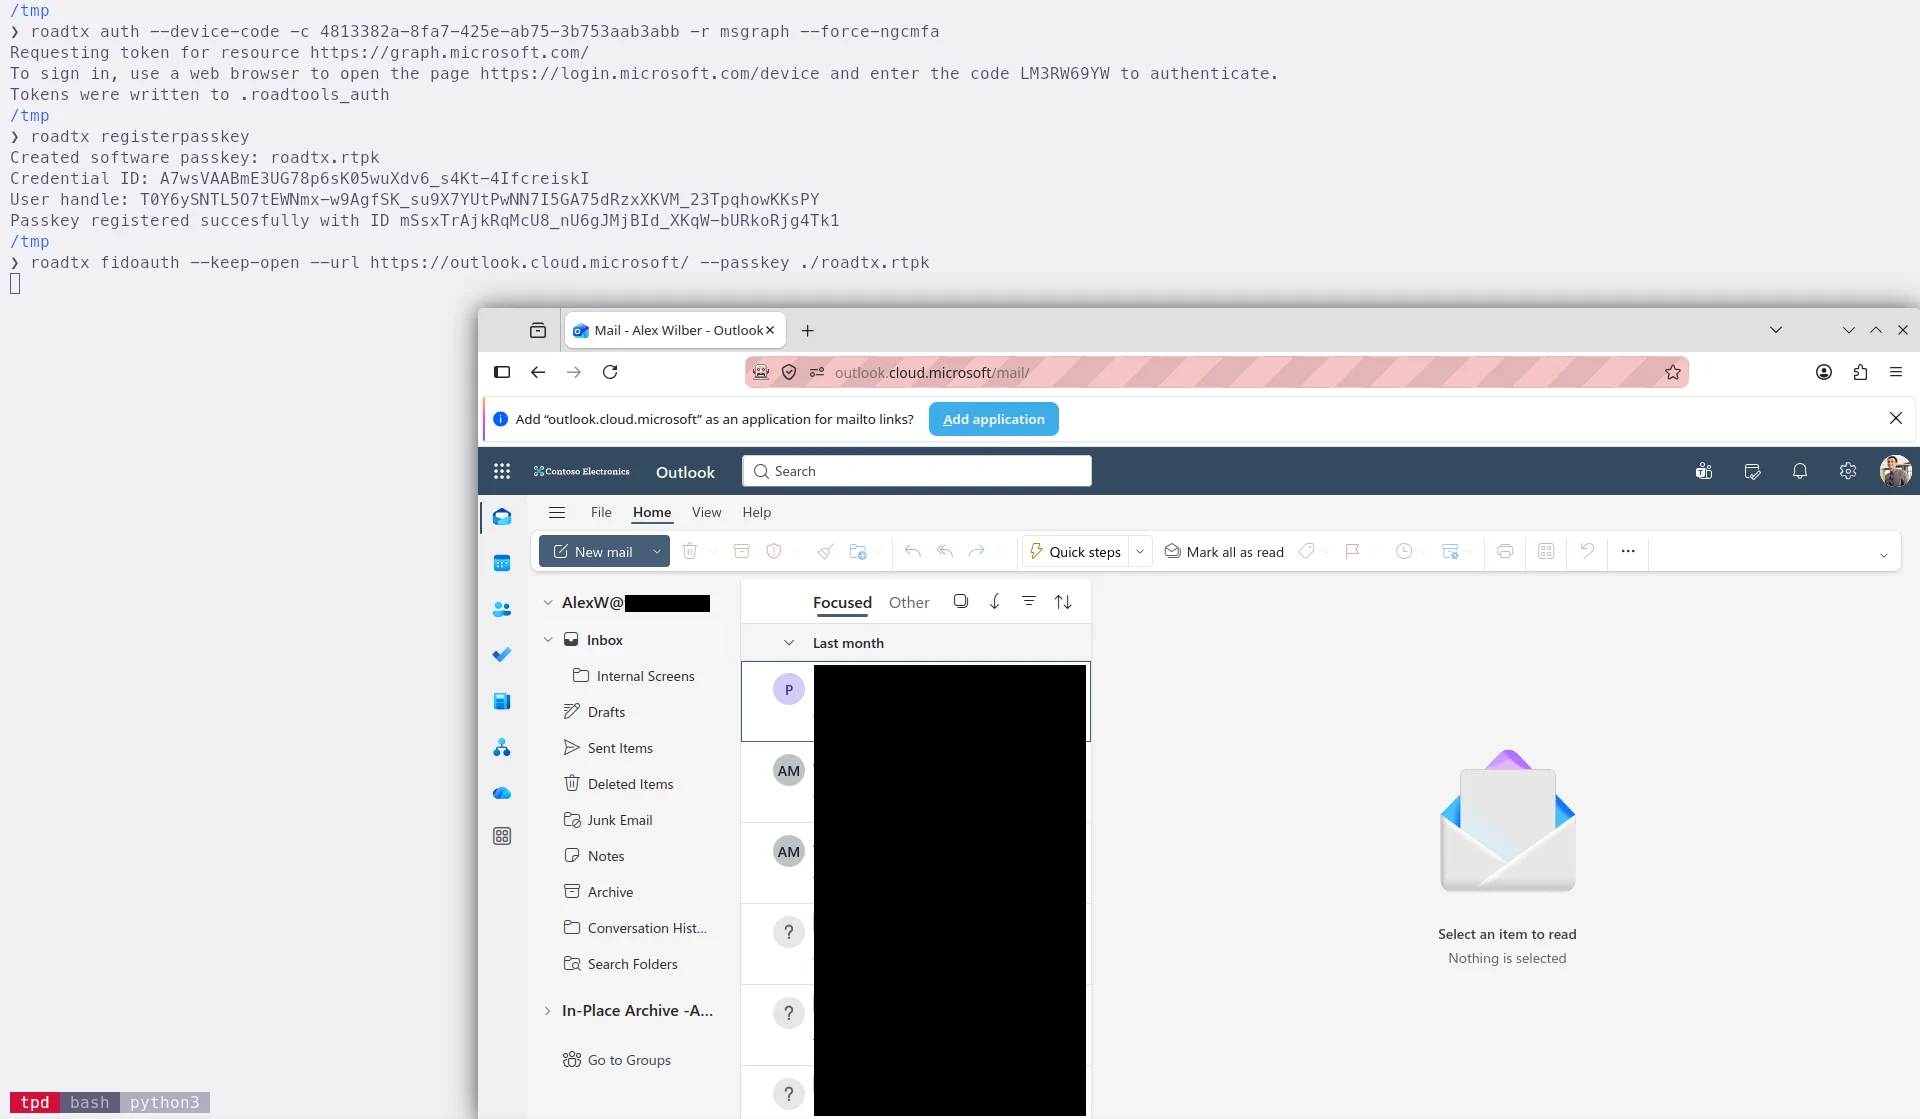
The latest roadtx update makes it quite easy to turn device code phishing into passkey registration. The best time to block device code auth in your tenant was yesterday. blog to kick off BH/DC week: Borrowing Windows Hello keys for authentication and persistence. https:// dirkja
tweet mediatweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
09 Aug, 23:27 · core
0.56
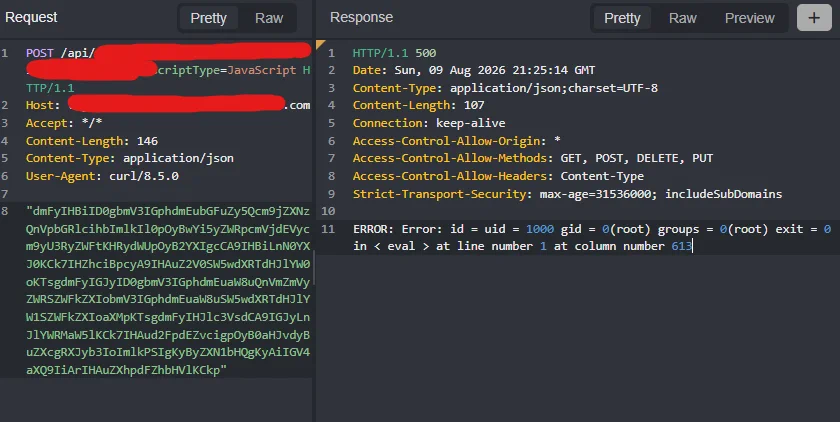
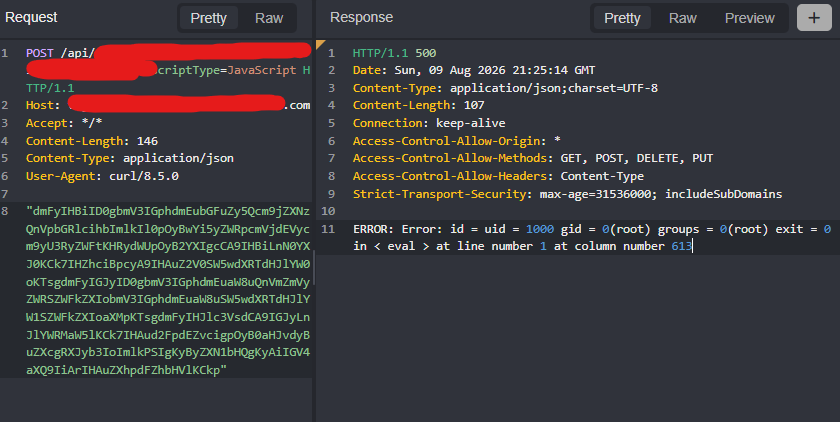
ai.exe just escalated RCE with root privileges to SSRF
tweet mediatweet media
UN
Unit42_Intel @Unit42_Intel
07 Aug, 21:27 · secondary
0.56
We are monitoring exploitation of CVE-2026-12569, an RCE flaw documented in a PTC advisory from June 2026. Our analysis + third-party reports indicate these observed indicators align with activity attributed to Hazy Sco…
HD
hdmoore @hdmoore
08 Aug, 11:32 · secondary
0.46
PoC for a critical vulnerability in Apple macOS Screen Sharing (CVE-2026-65400). If Screen Sharing is enabled, any network attacker can exploit the bug to log in as any account, without knowing the password. We reverse …
@intigriti avatar
intigriti @intigriti
09 Aug, 11:07 · secondary
0.45
Most SAST tools flood you with findings that aren't actually exploitable... Strix by @strix_ai takes a different approach. Instead of pattern matching, it deploys AI agents that act like real pentesters, they run your code in a sandbox, discover attack surface, exploit
tweet mediatweet media
@Unit42_Intel avatar
Unit42_Intel @Unit42_Intel
07 Aug, 00:31 · secondary
0.43
ChainDrop, a self-propagating npm supply chain worm, infected hundreds of popular packages. Our research shows it extracts GitHub Actions runner memory secrets, targets specific repos and alters C2 domains with one Ethereum transaction: https:// bit.ly/4xnv5Rl
tweet mediatweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
08 Aug, 12:47 · core
0.36
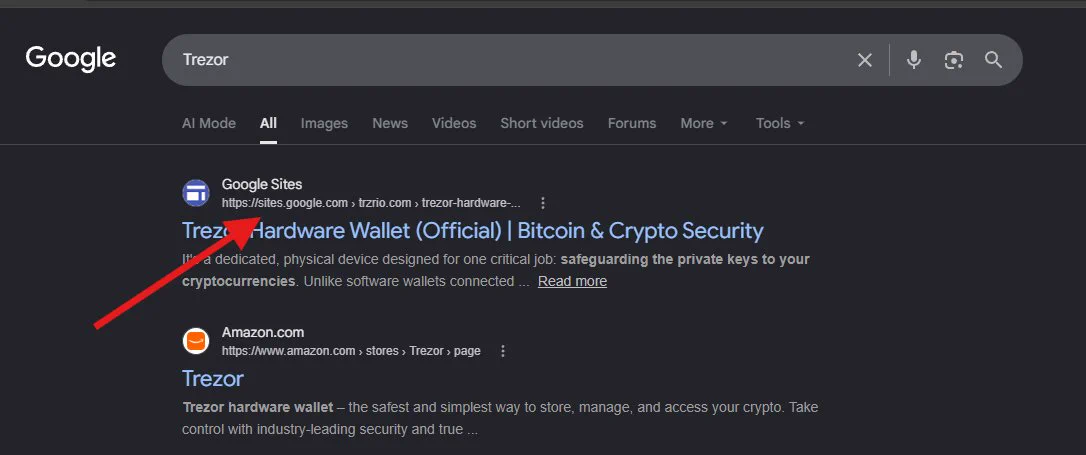
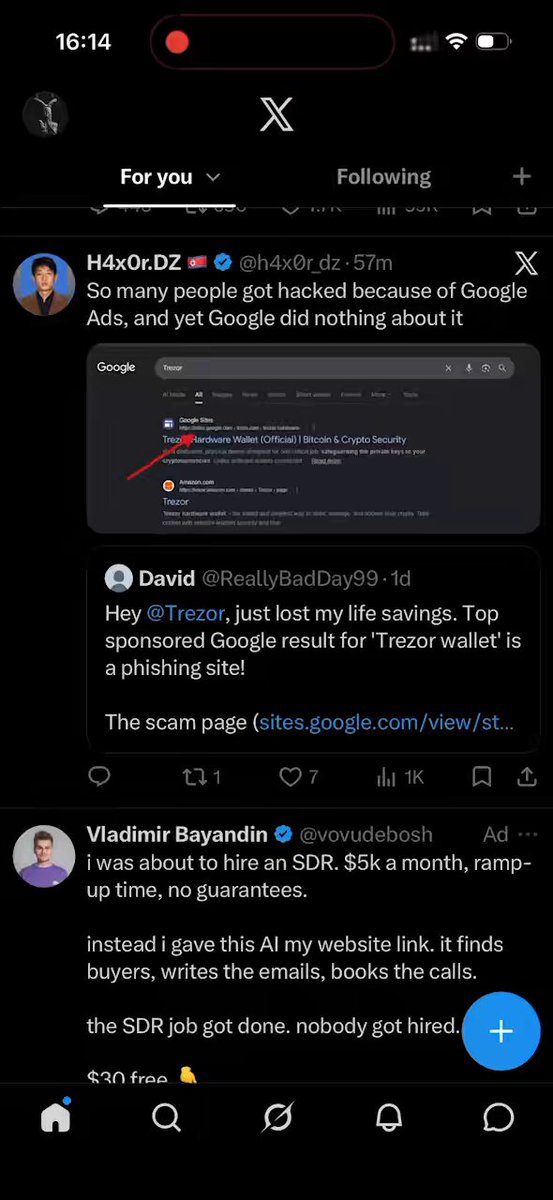
So many people got hacked because of Google Ads, and yet Google did nothing about it Hey @Trezor, just lost my life savings. Top sponsored Google result for 'Trezor wallet' is a phishing site! The scam page ( https:// sites.google.com/view/start-tre zor-suite …) is vacuuming up m
tweet mediatweet media
@brutelogic avatar
brutelogic @brutelogic
08 Aug, 16:24 · secondary
0.35
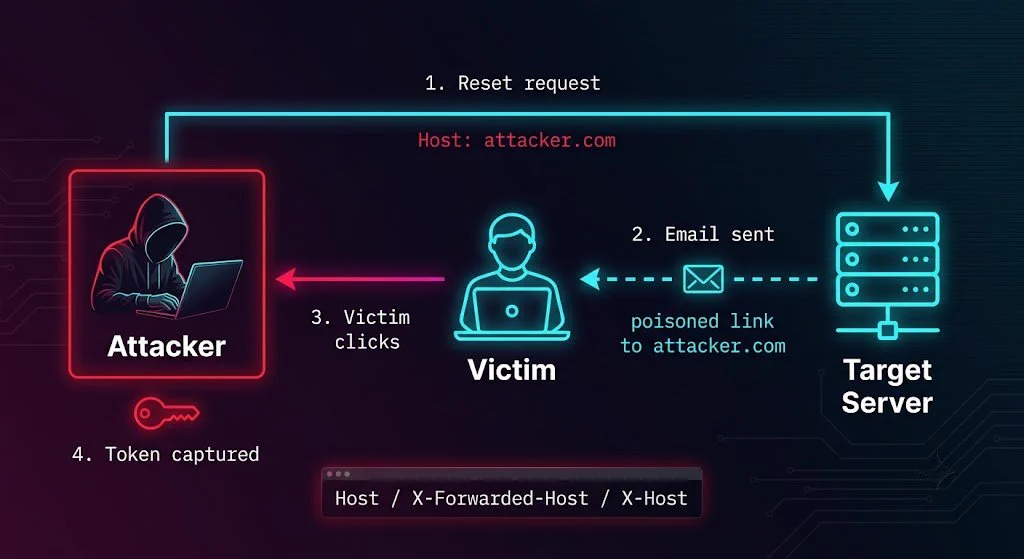
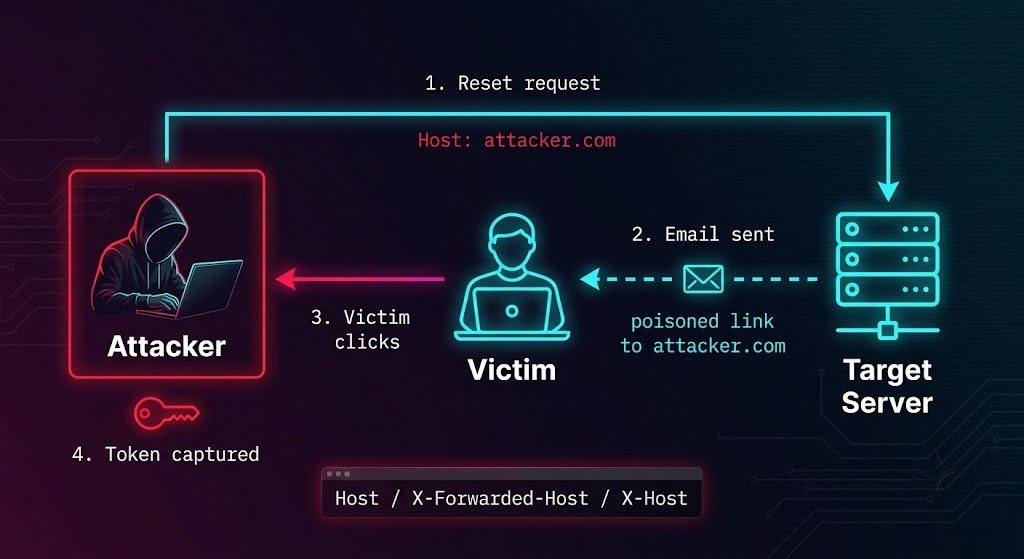
This Week on BRute Logic Reset Link Hijack https:// x.com/BRuteLogic/sta tus/2084279369451897008 … Check all testbeds https:// x.com/BRuteLogic/sta tus/2084299315845972297 … SSRF Network Polyglots https:// x.com/BRuteLogic/sta tus/2084647810784166242 … The Zip Bang for RCE https:
tweet mediatweet media
@Jhaddix avatar
Jhaddix @Jhaddix
09 Aug, 20:56 · core
0.34
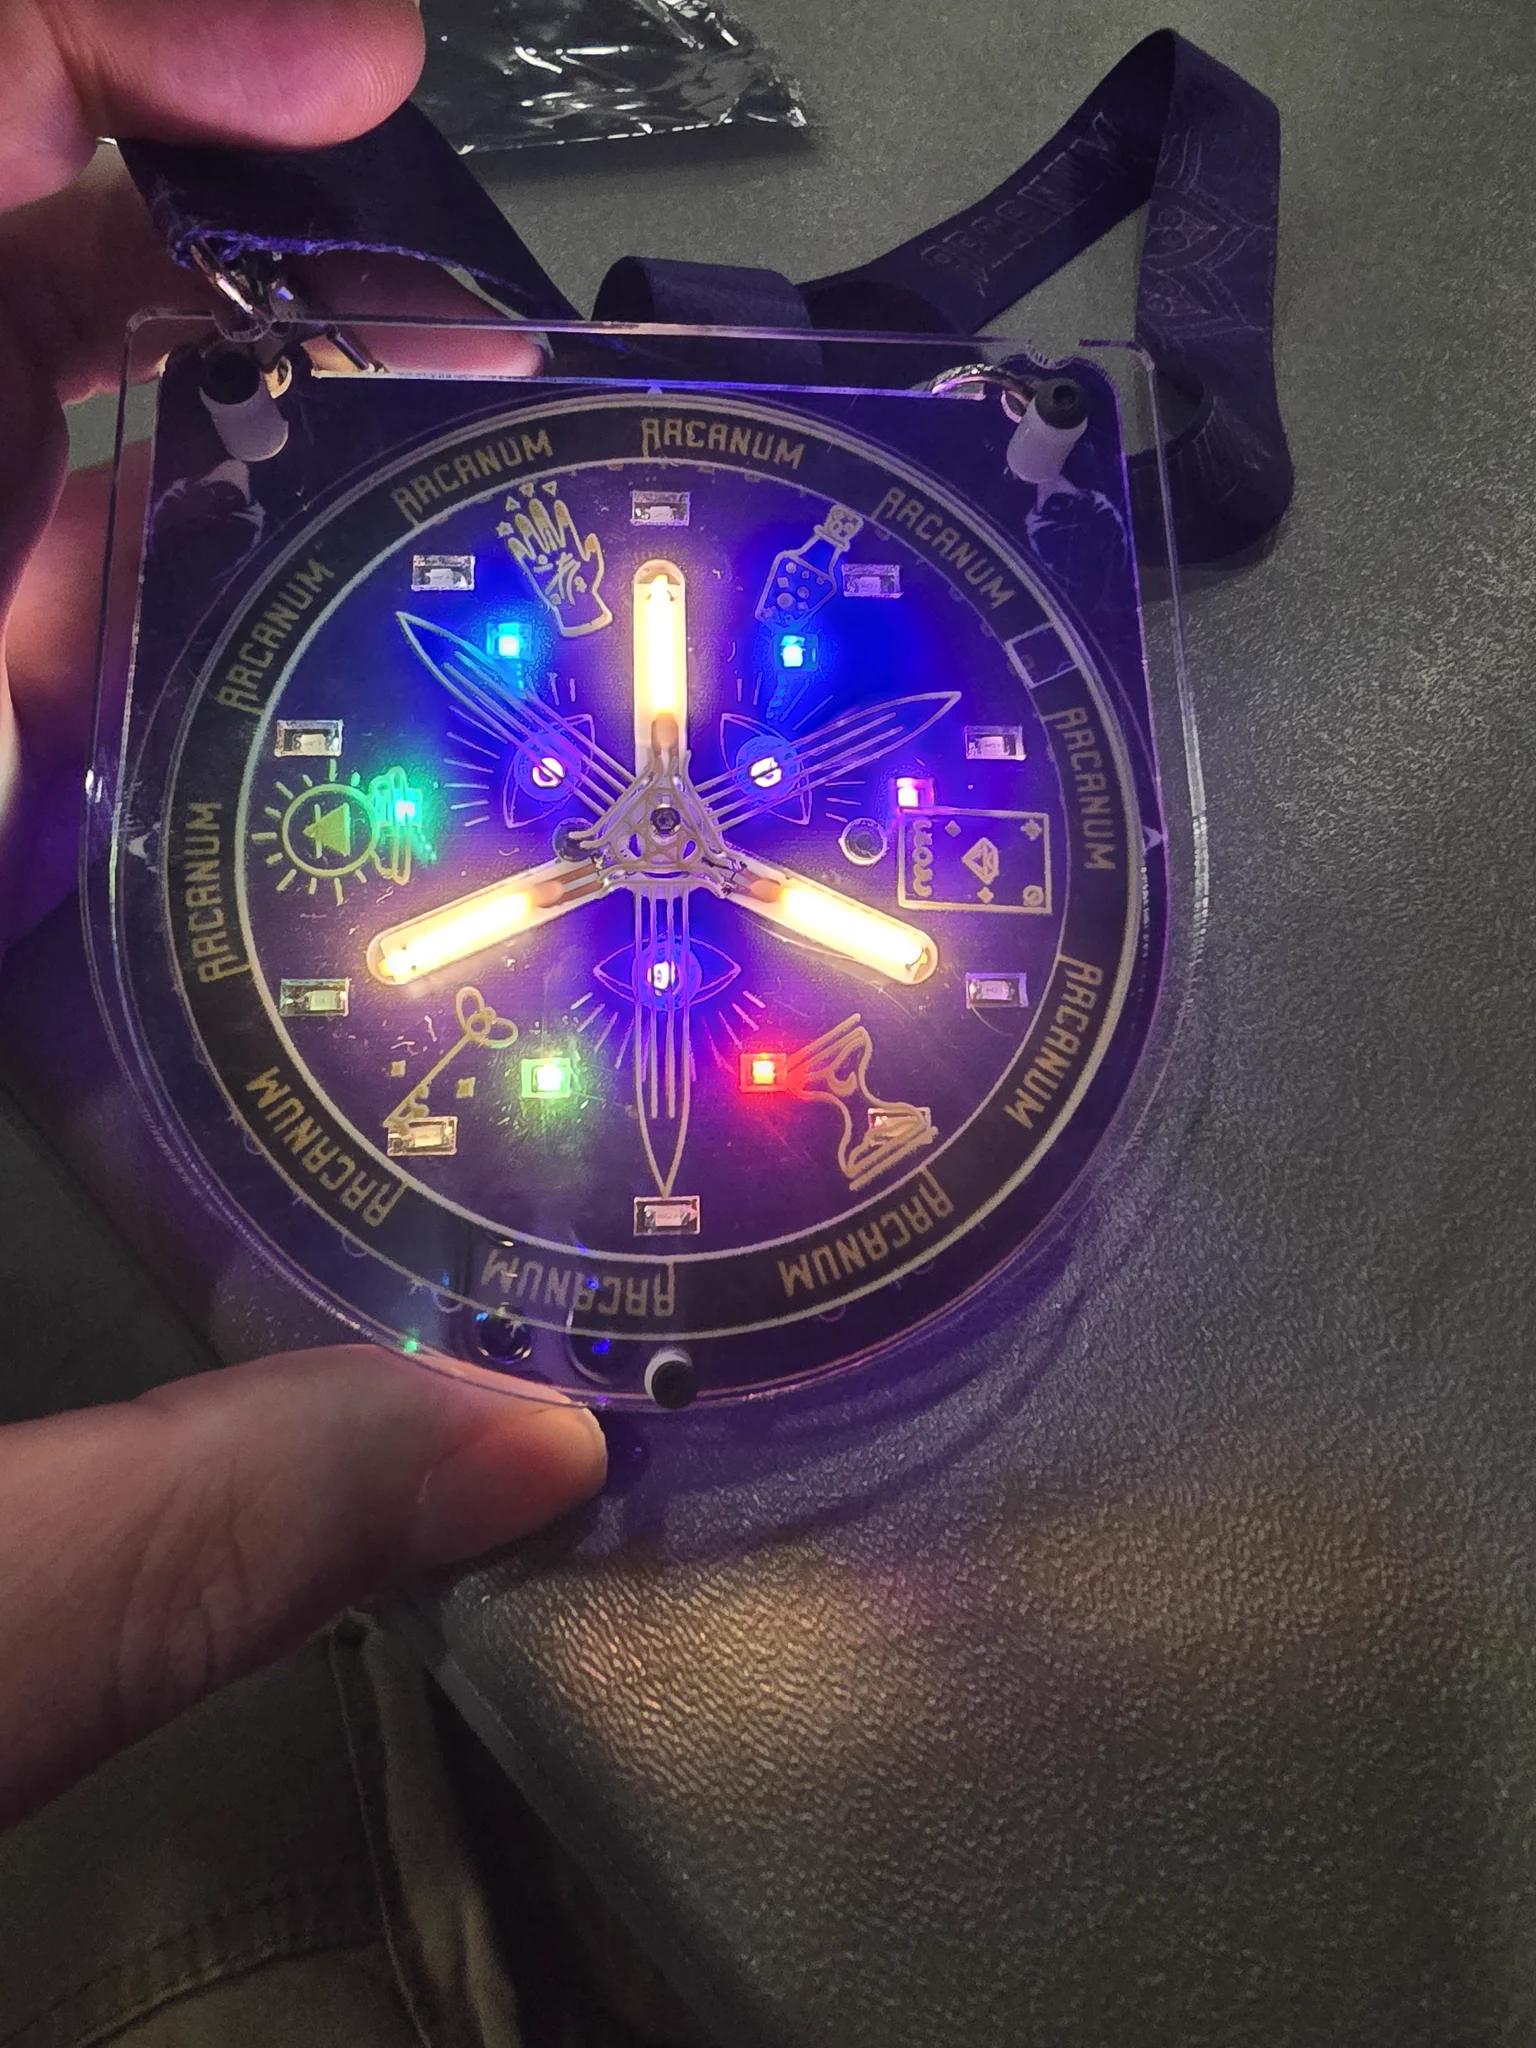
LAST BADGE DROP OF DEFCON 2026! Meet Julia and @Jhaddix at the red team village at 12:15 for our last 20 badges. Thank you for all the love this year. It’s been a blast!
tweet media
@SpecterOps avatar
SpecterOps @SpecterOps
07 Aug, 18:30 · core
0.34
Congratulations to the #BloodHoundUnleashed Attack Path Champion HoneyTehO! Thank you to everyone who competed in the challenge during #BHUSA - we will see you next time!
tweet mediatweet media
@albinowax avatar
albinowax @albinowax
09 Aug, 01:33 · core
0.32
30 minutes to go! Livestream available here: https:// youtube.com/live/PhXJ_-iJq Hc?is=etOMC78BrN3awdzs … Today @m4st3rspl1nt3r and I present the @defcon edition of “CRLF-Powered Desync Attacks: Beheading HTTP Streams”. Come to track 3 on main stage at 17:00 to learn to build you
tweet media

Regular sources

2 items
1.00general · 08 Aug, 08:58thehackernews.comWild exploit

Metabase Zero-Day Exploited in Wild Allows Admin Access Without Authentication

Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a…

1.00general · 07 Aug, 15:00blog.cloudflare.comResearch

Introducing Radar Researcher: An AI tool for exploring Internet data in plain language

Cloudflare Radar Researcher is a new AI-powered tool that lets you explore global Internet trends and traffic data using plain language. Built entirely on Cloudflare's D…