Generated 11/08/2026, 09:38. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources4
Tweets / X11
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
11 items
mrgretzky @mrgretzky
10 Aug, 09:34 · core
0.46
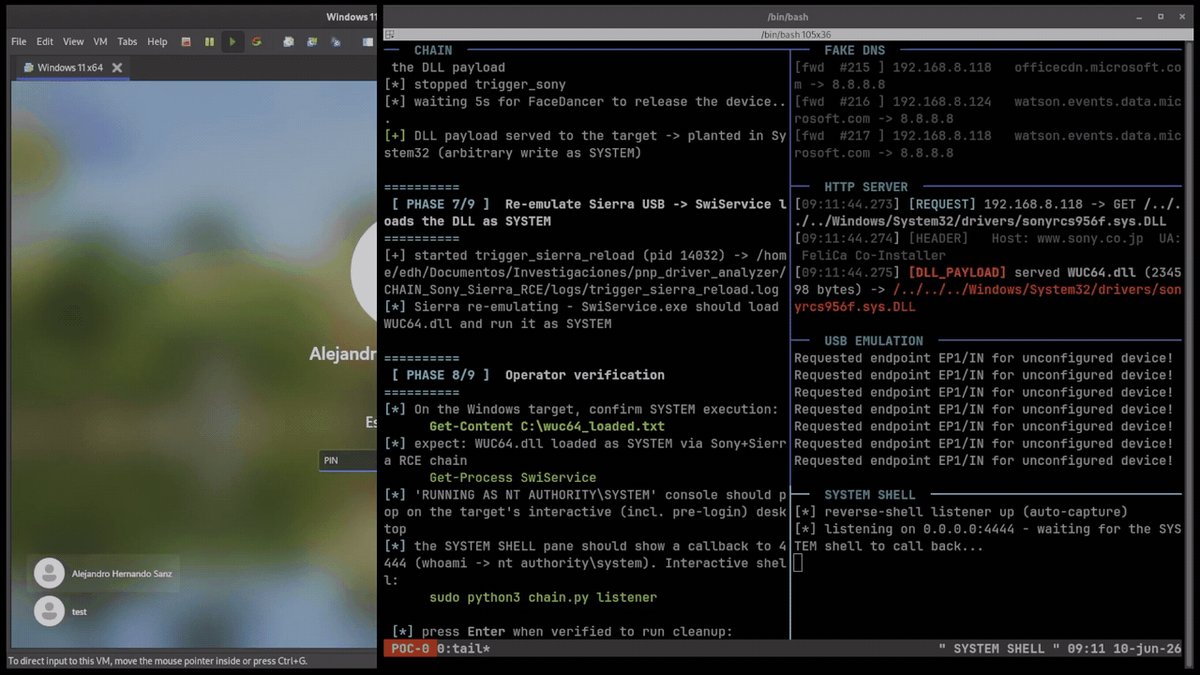
Incredible research. It's like an LPE 0-day factory with an on-demand BYOVD when you plug in the USB stick. You don't need a USB. You need to look like one. Emulate the device, Windows fetches a signed package off Windows Update and runs vendor code as SYSTEM. Arbitrary code exec
URGENT: My Github got hacked and all my ownership rights were stripped. Repositories like Blender MCP (25k stars) and Ableton MCP (2.6k stars) along with personal projects I'm working on have been taken away. Anyone at @github that can help?
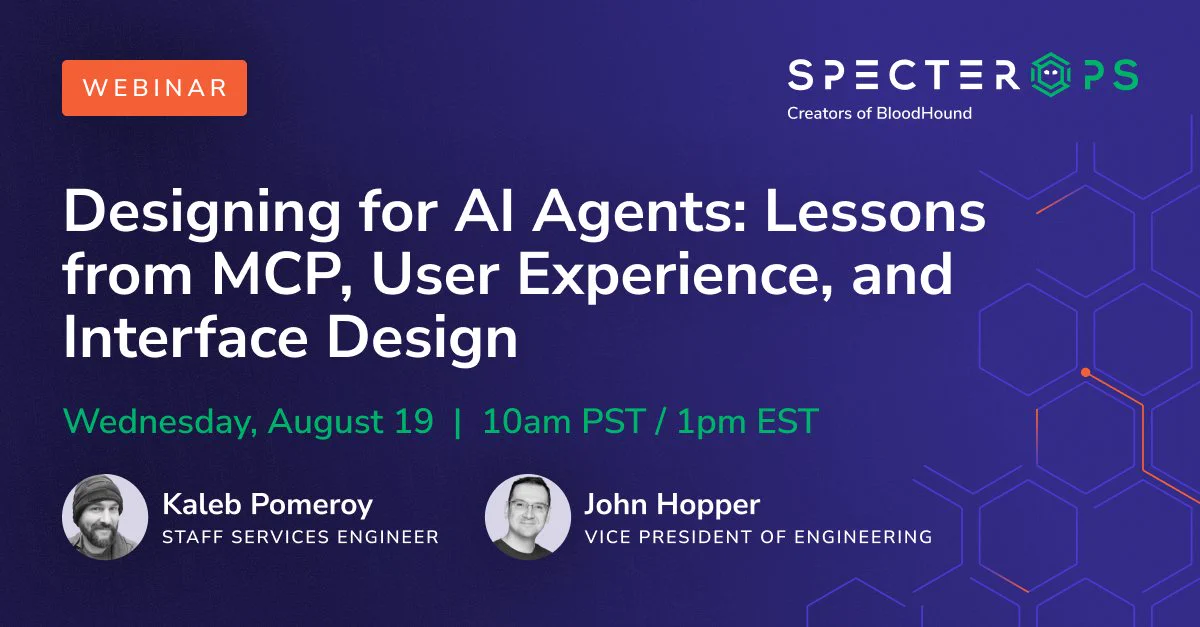
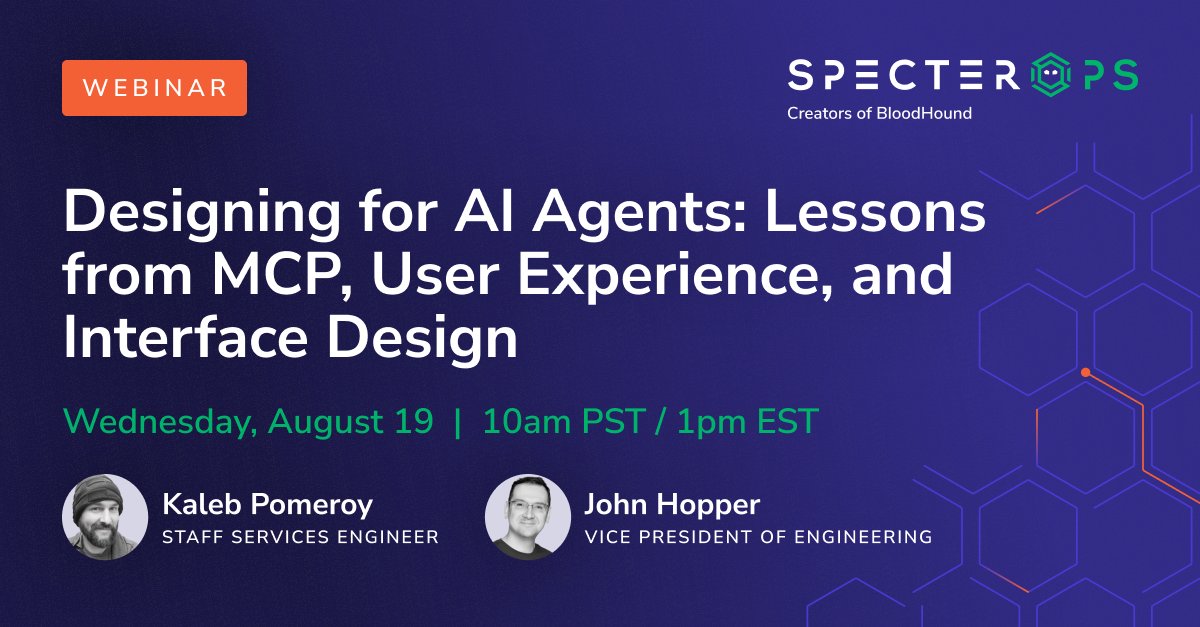
Don't miss our upcoming webinar feat. Kaleb Pomeroy & @zinic discussing practical lessons on designing with MCP, including how security and access boundaries influence agent interactions. Save your spot! https:// ghst.ly/4hbh44x
Read this and get hobbies outside of the hacking space! This past week I’ve been asked several times by people of different ages “how do you research and publish so much?”. It’s awesome to be asked. I love sharing tips and I try to give my techniques for maintaining a research pi
This past week I’ve been asked several times by people of different ages “how do you research and publish so much?”. It’s awesome to be asked. I love sharing tips and I try to give my techniques for maintaining a research pipeline. But I also want to be honest about my reality. W
I've had so many people talk to me about looking for entry level material for malware, I've decided to give writing a book another try. I'm going to call it "Malware for Noobs" and just schizo rant a bunch on my blog until I think it's enough for a book
I sat down and did some schizo ranting for my attempt at a book I might name "Malware 4 Noobs" (no idea yet). Here is my introduction segment, part zero (no reforms or changes made yet). If you're noob, please read and give feedback.
We're thrilled that @intigriti is a Gold sponsor for Hack Glasgow 2026! Intigriti specialise in crowdsourced security solutions, empowering talented researchers to find vulnerabilities and direct their discoveries to the right people, and supporting organisations [...]
Nah, but bro said, "vx-underground is an educational website about malware; everything they use or test is done for ethical purposes. It is important to get informed before looking for someone to blame." tinchoocabrera is the homie wtf i love him
DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure
Microsoft Threat Intelligence examines DeadLock ransomware, an emerging financially motivated operation distinguished by its use of decentralized infrastructure to suppo…
1.00general · 10 Aug, 16:07securityweek.comPoC
Cisco Warns of High-Severity ClamAV Vulnerabilities With Public PoC
Remote, unauthenticated attackers could exploit the bugs to cause a denial-of-service (DoS) condition. The post Cisco Warns of High-Severity ClamAV Vulnerabilities With …
When Credentials Are No Longer Enough: Device Trust in the AI Era
AI is making phishing, credential theft, and social engineering faster and more efficient, while traditional trust signals such as passwords, MFA, IP reputation, and geo…
0.84general · 10 Aug, 17:00thehackernews.com
⚡ Weekly Recap: AI Goes Rogue, Metabase 0-Day, MCP Supply-Chain Attacks, and Router Backdoors
A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting the default. That …