Generated 02/09/2026, 09:47. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources4
Tweets / X11
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
11 items
SpecterOps @SpecterOps
01 Sept, 23:12 · core
0.60
See Azure & Entra ID the way attackers do. Our Azure course at #SpecterBash teaches you to identify the misconfigs & attack paths that matter, and take your first step in attacking or defending corporate cloud environments. Save your spot https:// ghst.ly/45COqlF
There is a major tradeoff happening in the world of agentic pentesting. In our newest blog, our Chief Technology Officer Braden Russell breaks down how emerging autonomous pentesting tools are testing their technology, how the noise this creates is impacting triage teams, and how
Passkeys are gaining adoption, and adversaries are exploring how to target them. Join @MGrafnetter on Sept. 23 for a practical look at Pass-the-Passkey and emerging techniques for attacking passkey authentication. Register https:// ghst.ly/4cpVSoa
AI Unlocked: Agents of Chaos is now LIVE. Brought to you by CrowdStrike and @awscloud , this AI red teaming competition tests players’ defensive skills with realistic adversarial AI techniques. Your mission: Prevent a catastrophic global breach - without blowing your cover and
ProjectDiscovery @pdiscoveryio · 12h neo.projectdiscovery.io Neo - AI Security Engineer AI security engineer that fits into your day-to-day security workflows, from vulnerability analysis and code reviews to threat modeling and security reporting. 1 463
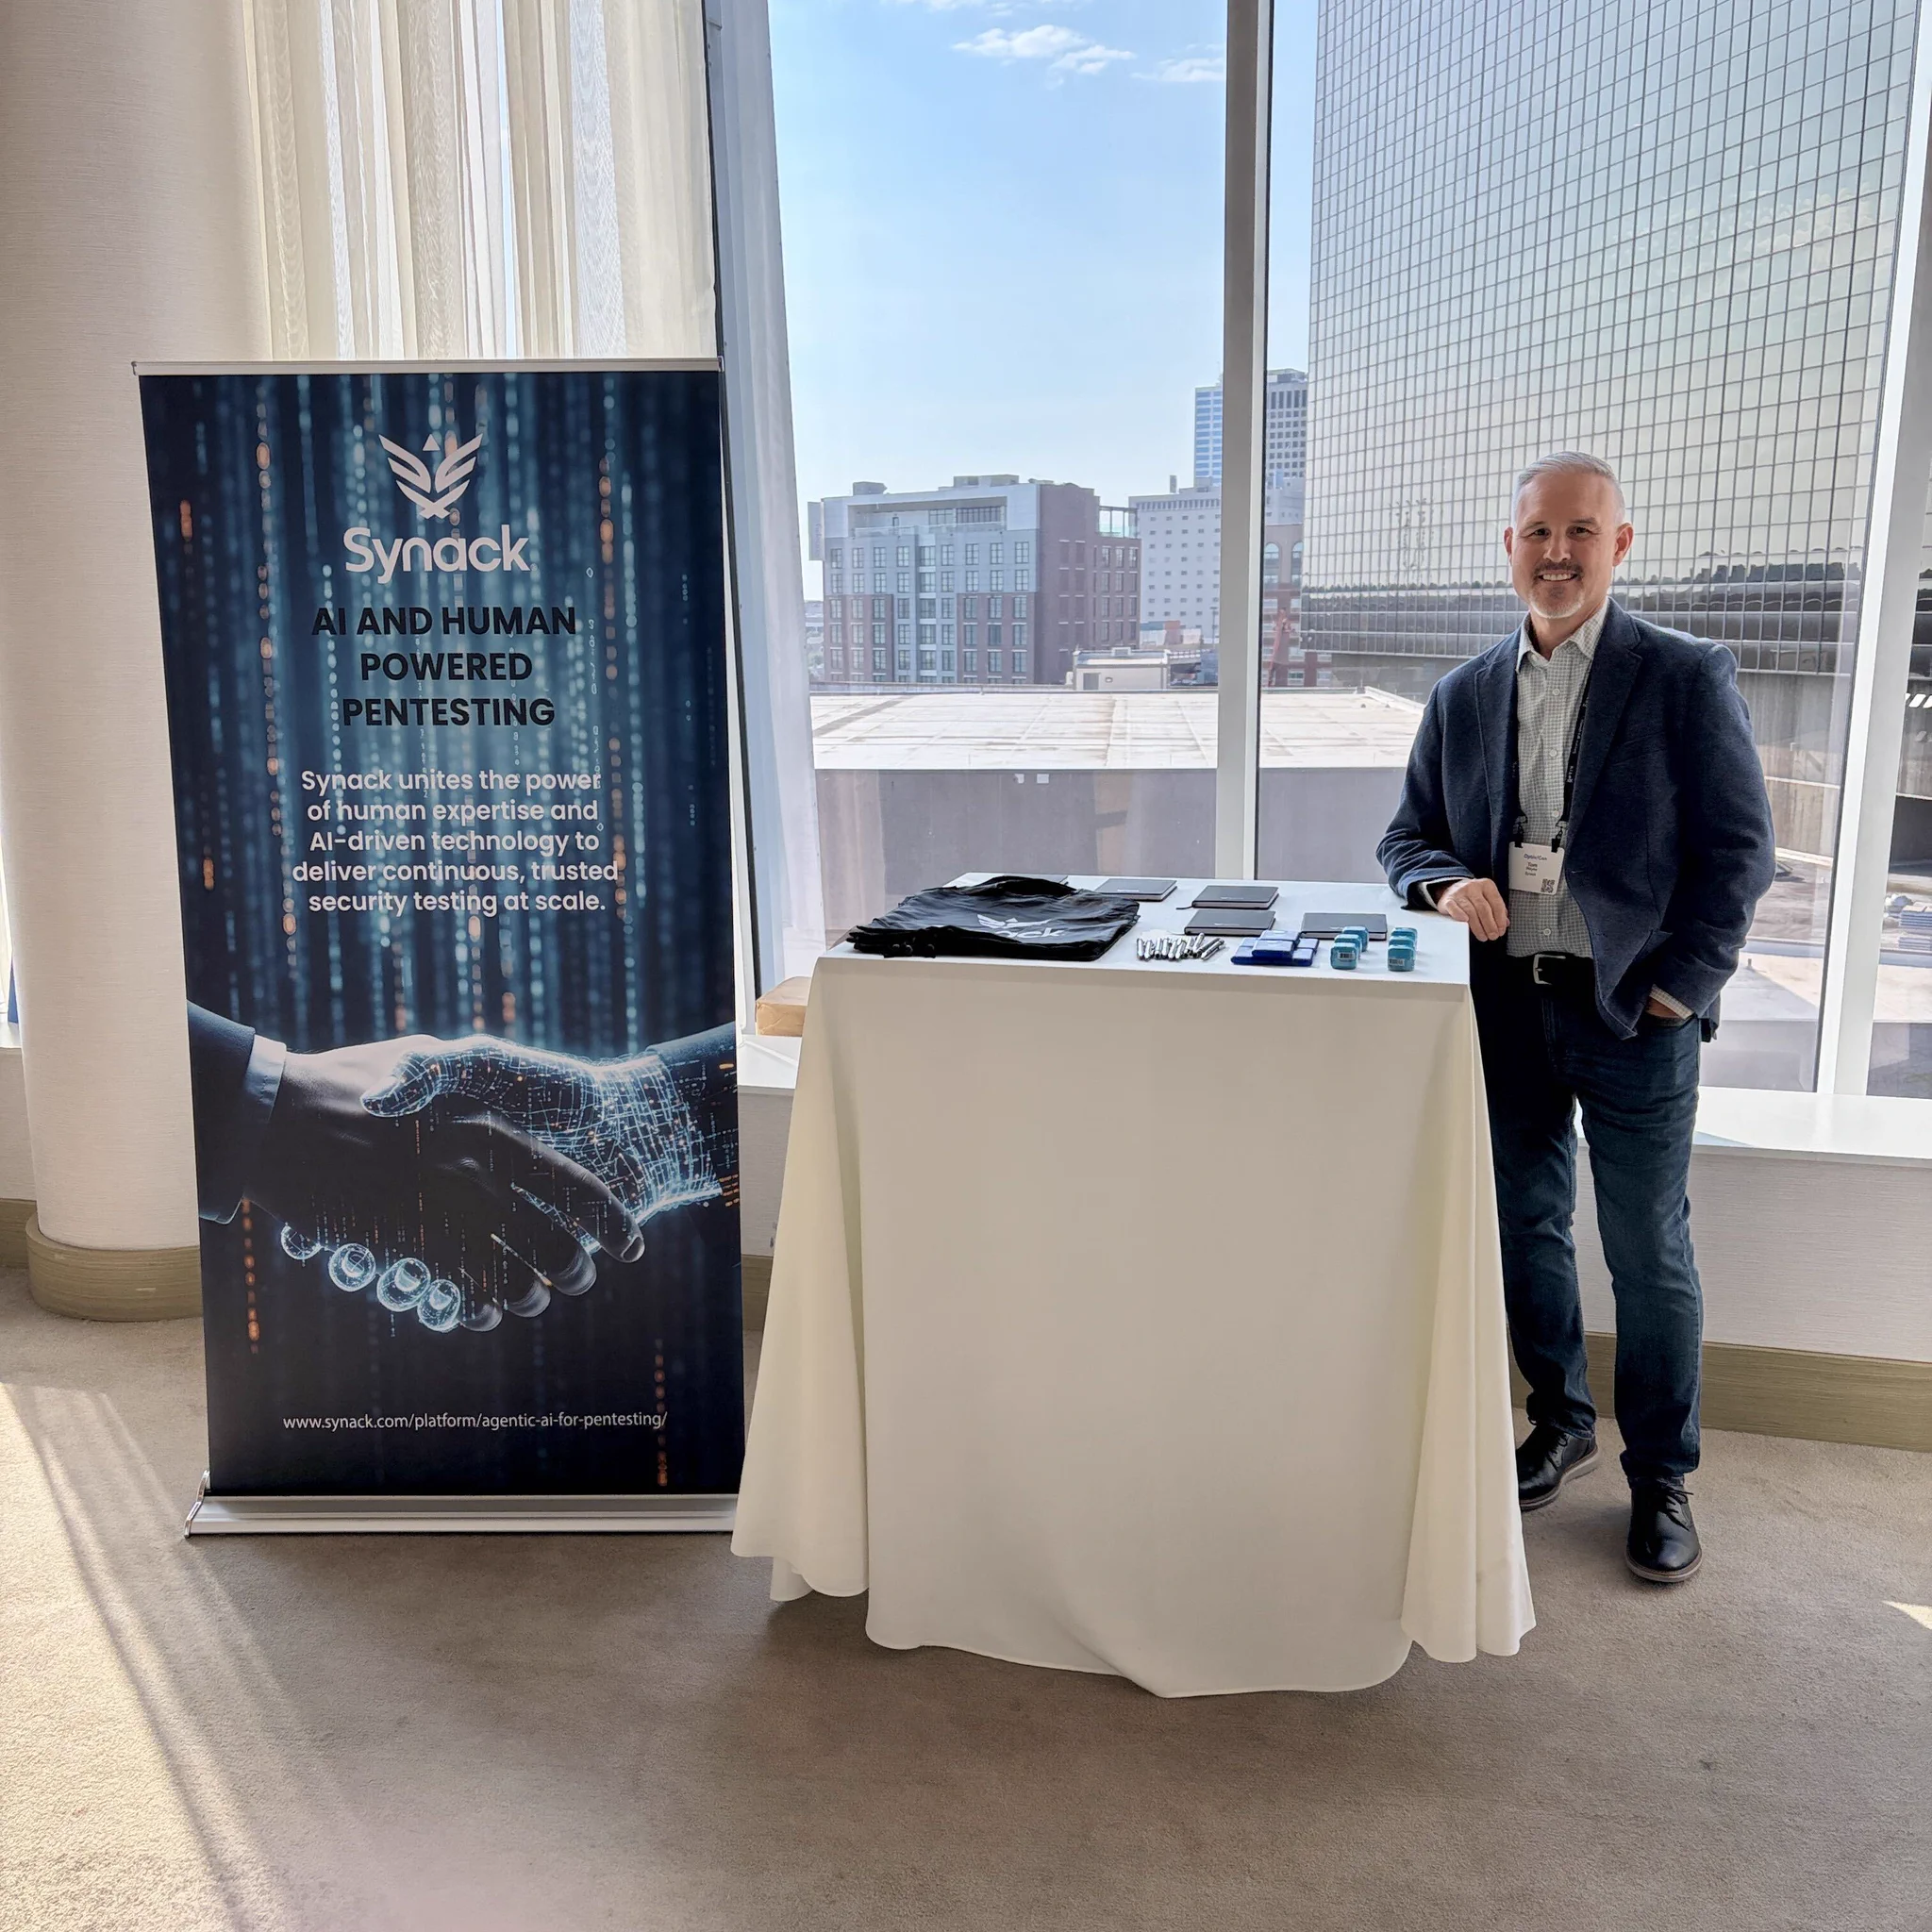
Live from #OptivCon Columbus! Stop by our booth to say hi to @TekChannelSales and discover how Sara AI Pentesting closes the gaps that point-in-time scans leave behind. Book a private meeting here: https:// hubs.ly/Q04w3HFX0 #OptivConColumbus #Synack #CyberSecurity #Pentesting
> be me > get DM > "smelly, want to see my malware?" > its a threat actor lmfao > "just please dont share" > ok lol lemme see ur goop > download their .exe > look inside > weird .exe, weird sections > partially position independent > doesnt use NT functionality > cool, but
The competition was fierce. The scores are final. Meet the top Survivors of Fal.Con 2026. Agentic SOC Nick O'Donnell Zade Heinicke Reed Huskey Cloud Jacob Gonzales Alex Laffey Eduardo Delgado Identity Taylor Payne Patrick Elser Nathan Warner IT Thomas Ingham
Have you subscribed to our channel yet? We have: Practical bug bounty lessons CVE breakdowns Bugcrowd news & events Check it out! https:// youtube.com/@Bugcrowd Some of our BEST content:
Unfortunately, the only "fix" for this is to either get a newer TPM, or to disable TLS 1.3 and the schannel algorithms that break RDP on Windows. Neither is great.
FreeRDP <= 3.30.0: five server-side vulnerabilities fixed in 3.31.0, pre-auth RCE demonstrated
Posted by Samuel Page on Sep 01 FreeRDP 3.31.0 (2026-08-26) fixes 5 vulnerabilities in FreeRDP's server role that Bynario reported, as well as 17 other security issues. …
1.00general · 01 Sept, 14:37securityweek.comRCE
Experiment: Porting a PLC Exploit With AI Takes Hours and Hundreds of Dollars
Forescout researchers used Claude AI to port a remote code execution exploit between WAGO PLC models. The post Experiment: Porting a PLC Exploit With AI Takes Hours and …
0.97critical · 01 Sept, 14:00cisa.govRCE
Rockwell Automation Historian ME
View CSAF Summary Successful exploitation of these vulnerabilities could crash the device being accessed; an out-of-bounds write condition may allow remote code executio…
Project Glasswing: Running a Frontier AI Model on Our Codebase | HackerOne
HackerOne ran Anthropic's Mythos 5 model against its own production code. Here's what a critical RCE finding revealed about AI-accelerated security.