Official intelligence summary

HAIJA INTEL REPORT

Generated 04/09/2026, 10:09. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources3
Tweets / X12
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.

Tweets / X

12 items
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
03 Sept, 03:16 · core
0.42
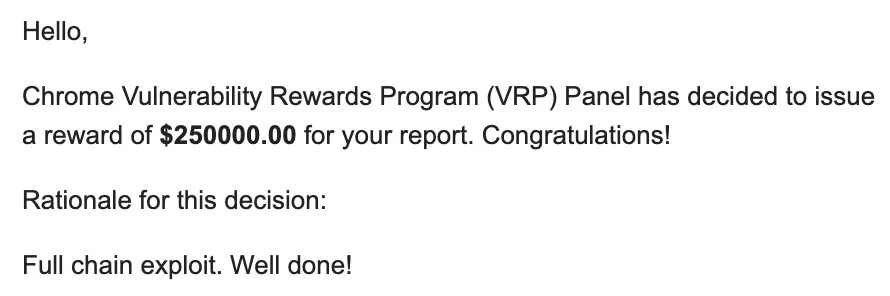
$250,000 for a Chrome exploit chain is still a very low bounty btw This just in: XBOW's Native Team has claimed the first Chrome Full Chain Exploit Bonus this year. Only four will be awarded in 2026. ⚡️
tweet media
@SentinelOne avatar
SentinelOne @SentinelOne
03 Sept, 23:24 · secondary
0.32
We are expanding Wayfinder Frontier AI Services with @OpenAI 's Daybreak models: adding AI-powered code risk analysis and compromise assessment so teams can find and close truly exploitable threats fast. Rolling out now in private preview, with broader availability to follow.
@vxunderground avatar
vxunderground @vxunderground
03 Sept, 19:45 · secondary
0.32
If you're curious on how to get into goop (malware) research, it's simple. 1. Don't panic 2. Bring your computer to Apple Bees, really get to know her 3. Ask about her hobbies and interests 4. Don't ask her about her ex-BF 5. Use the staff of Sheogorath to place the computer in
tweet mediatweet media
@Sysdig avatar
Sysdig @Sysdig
03 Sept, 16:01 · secondary
0.31
Cloud attacks go from initial access to business impact in 10 minutes or less. For large enterprises, a single hour of downtime costs over $100,000. For finance and healthcare, $5 million per hour. The 10-minute window isn't a security problem. It's a business problem.
tweet mediatweet media
@pdiscoveryio avatar
pdiscoveryio @pdiscoveryio
03 Sept, 20:30 · secondary
0.29
Confirmed findings with a working proof of concept. That's what a good night's rest looks like for Emma Sleep's security team 😴
tweet mediatweet media
@vxunderground avatar
vxunderground @vxunderground
03 Sept, 06:10 · secondary
0.29
FalconFlank : Crowdstrike Falcon 0day LPE is now public https:// github.com/MSNightmare/Fa lconFlank …
tweet mediatweet media
@SpecterOps avatar
SpecterOps @SpecterOps
03 Sept, 20:46 · core
0.28
Don't miss @MGrafnetter at #HIPConf! His session next week will explore attacks against KDS Root Key scenarios and unveil a new technique for attacking DPAPI-NG in Windows that can decrypt secrets protected with SID Protectors. https:// ghst.ly/4gx3N5w
tweet mediatweet media
@intigriti avatar
intigriti @intigriti
03 Sept, 18:09 · secondary
0.22
Most support chatbots have evolved into fully autonomous agents that can help you with almost anything... And that comes with additional risk ☝️ Our latest article, based on @intidc 's talk at Bug Bounty Village during DEF CON 34, breaks down the full attack surface in AI
tweet mediatweet media
@nahamsec avatar
nahamsec @nahamsec
03 Sept, 21:04 · core
0.20
If you want to try it out: https:// app.grayswan.ai/arena/challeng e/hazard-hunt-q3 …
@nahamsec avatar
nahamsec @nahamsec
03 Sept, 21:04 · core
0.20
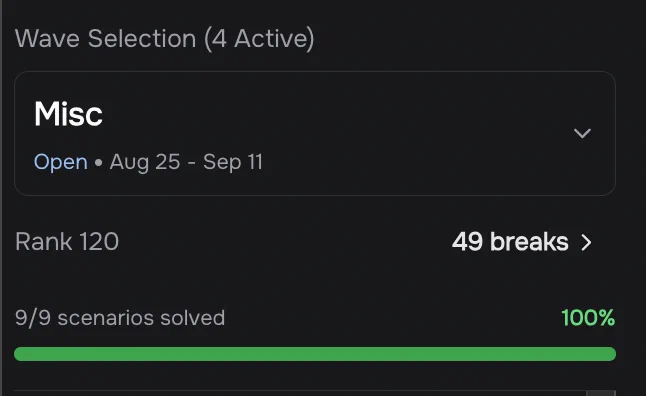
I just solved my first challenge in @GraySwanAI 's Hazard Hunt 🤯
tweet media
@outflanknl avatar
outflanknl @outflanknl
03 Sept, 17:00 · core
0.20
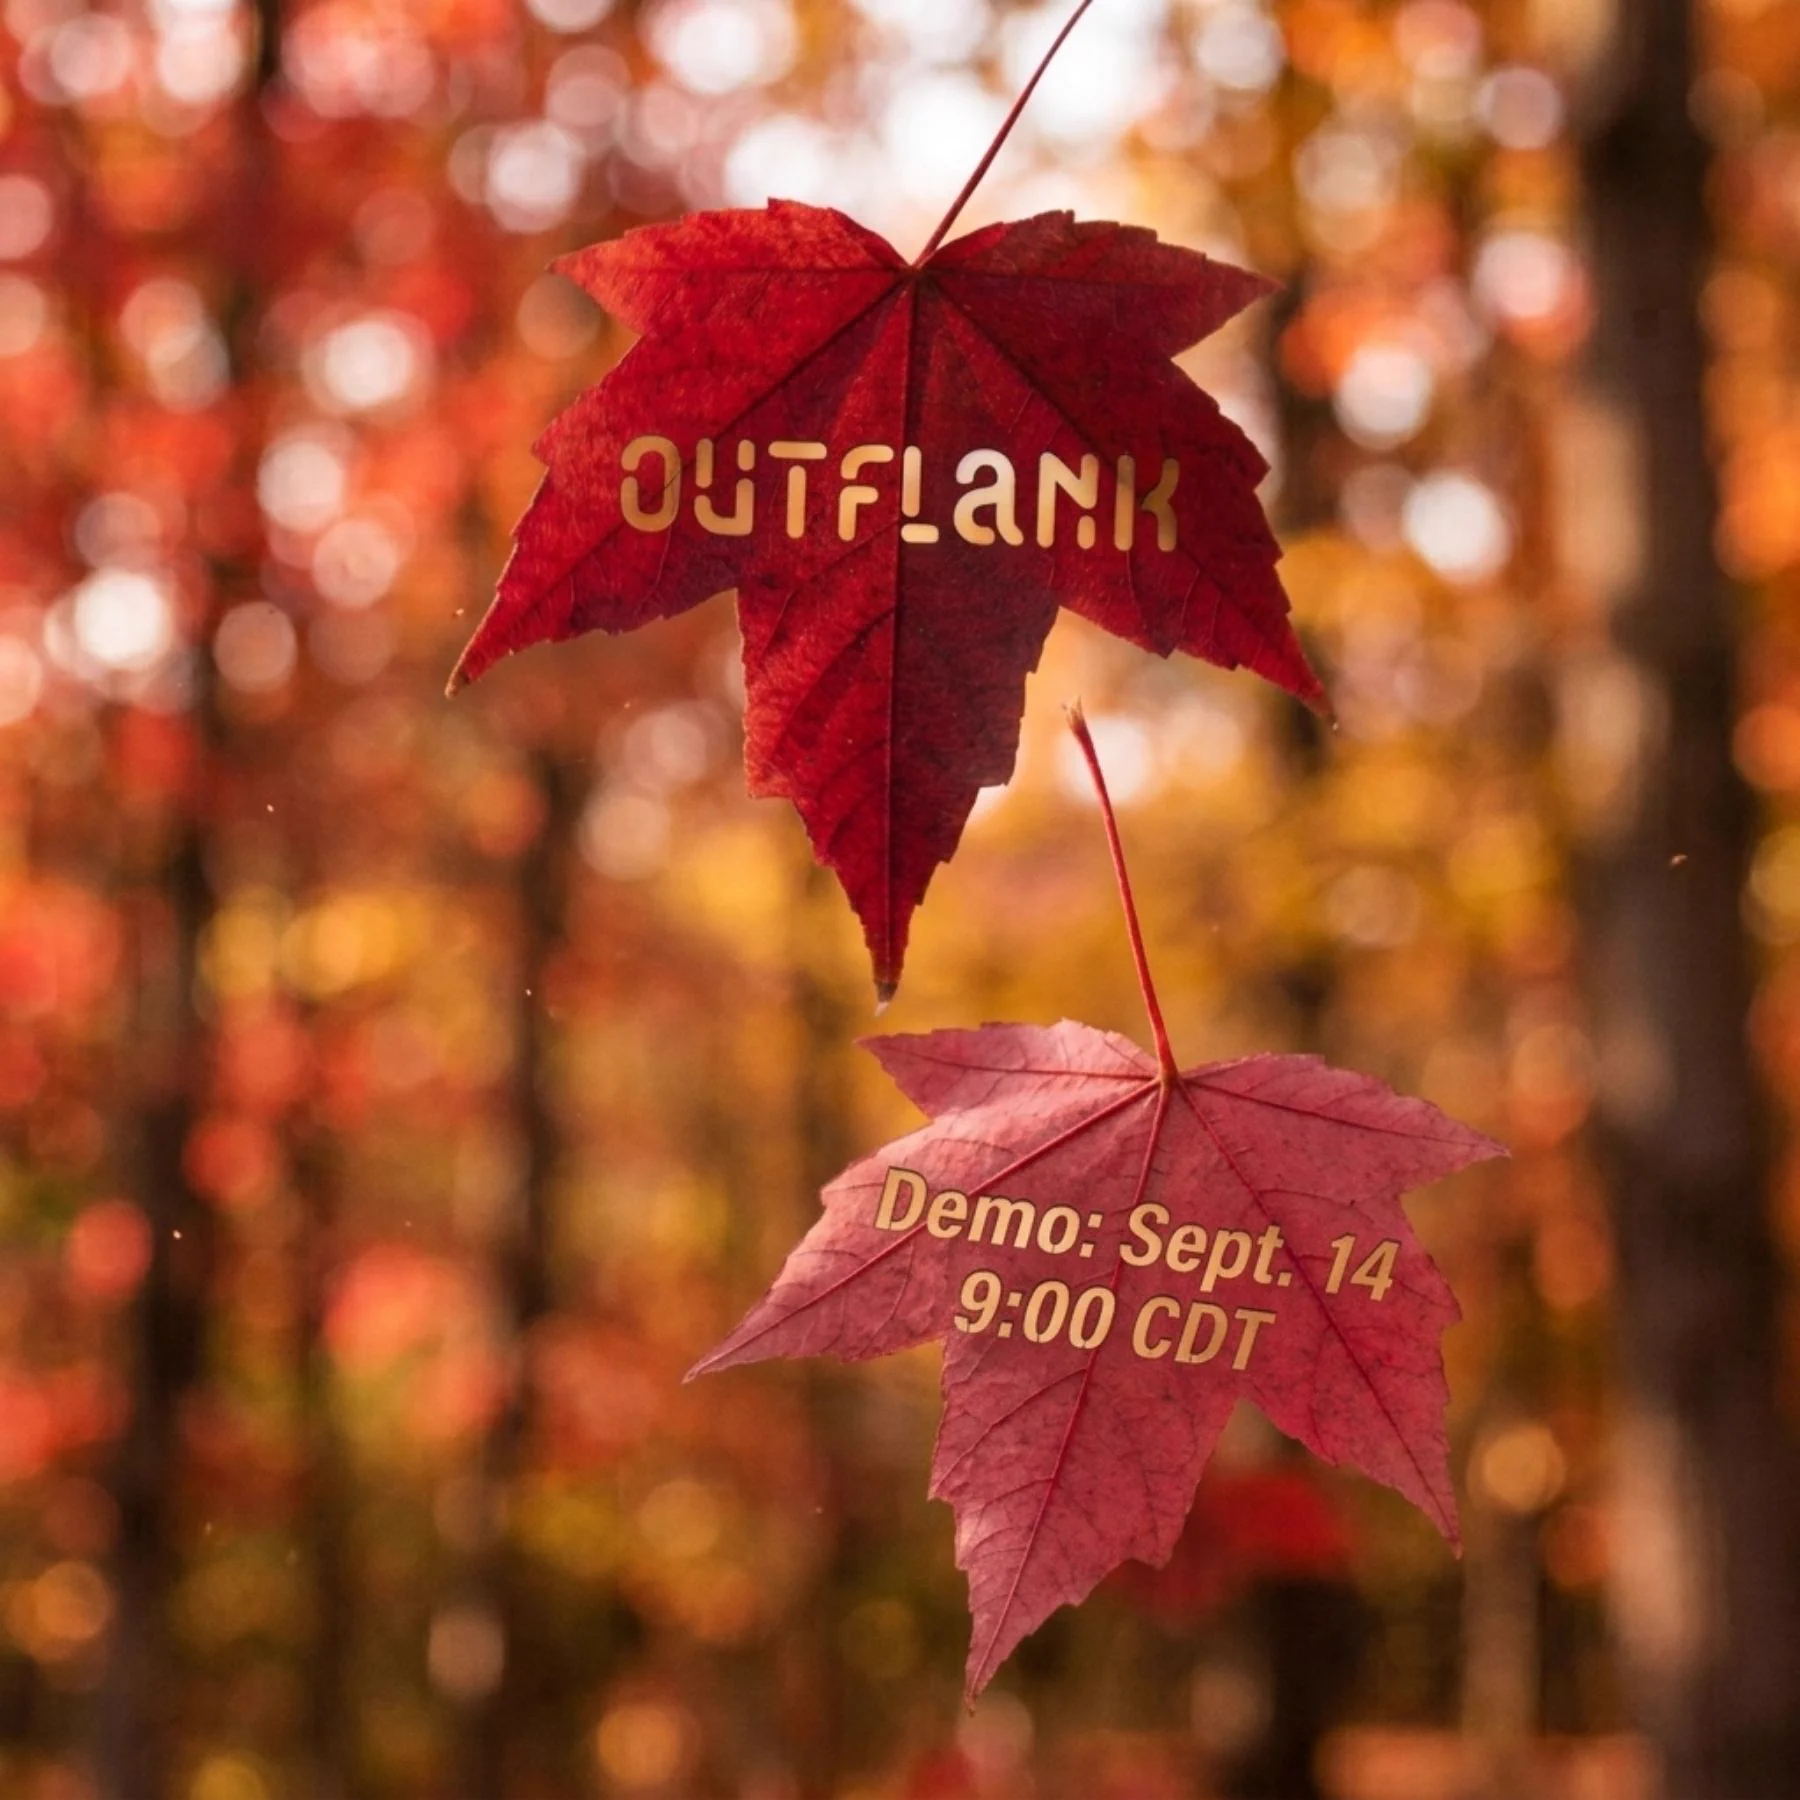
Autumn leaves are changing, just like OST is always evolving. Join us on Sept 14 at 9:00am CDT for a live demo of Outflank Security Tooling. https:// register.gotowebinar.com/register/59662 44119537590364 …
tweet mediatweet media
@TheDFIRReport avatar
TheDFIRReport @TheDFIRReport
03 Sept, 16:00 · core
0.20
A huge thank you to the organizations supporting the upcoming DFIR Labs Digital Forensics Challenge! 🙌 🏆 Our Sponsors Hack lu - https:// hack.lu Botconf - https:// botconf.eu Arsenal Recon - https:// arsenalrecon.com DEATHCon - https:// deathcon.io Thanks to
tweet mediatweet media

Regular sources

3 items
1.00general · 03 Sept, 18:00microsoft.comAttack pathResearch

ASCII smuggling crosses over from AI prompt injection to phishing evasion

Invisible Unicode characters popularized for hiding instructions from AI models are now being used to obfuscate words before email filters parse them. The post ASCII smu…

1.00general · 03 Sept, 08:26thehackernews.comPoCTradecraft

Researcher Releases FalconFlank PoC Showing Privilege Escalation in CrowdStrike Falcon

The security researcher known as Chaotic Eclipse (aka INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse) has dropped a new zero-day dubbed FalconFlank, a privilege …

0.97critical · 03 Sept, 14:00cisa.govRCE

IXON VPN Client

View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to perform remote code execution on the computer running the client with elevated…