Official intelligence summary

HAIJA INTEL REPORT

Generated 20/08/2026, 09:39. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources6
Tweets / X9
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.

Tweets / X

9 items
@SpecterOps avatar
SpecterOps @SpecterOps
19 Aug, 18:50 · core
0.46
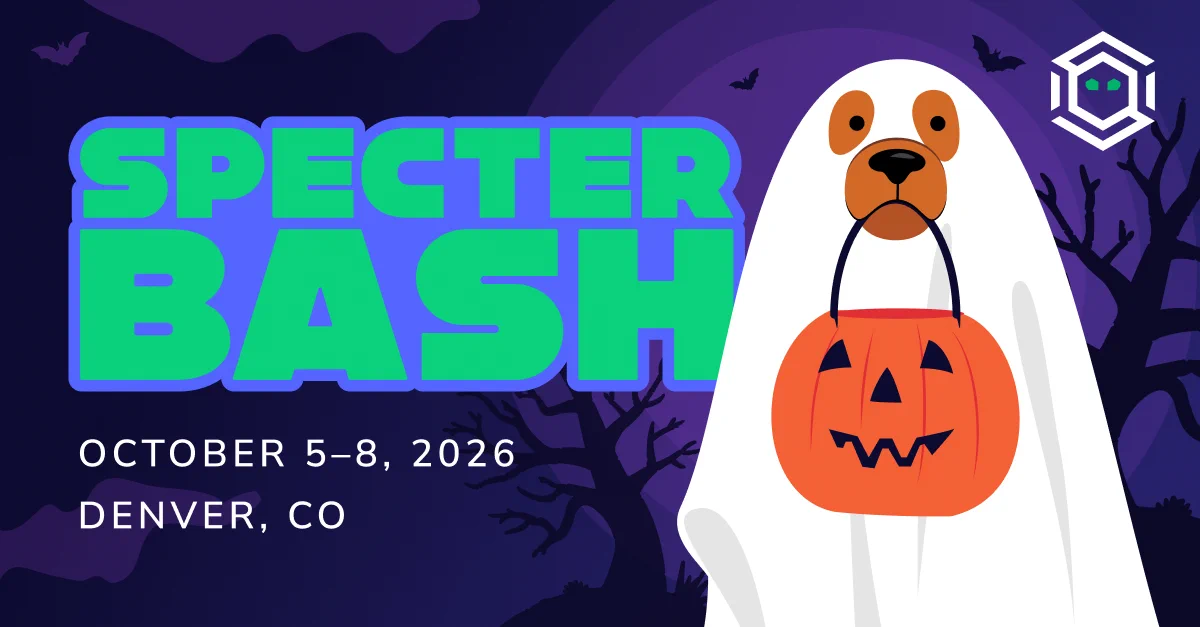
#SpecterBash is back! Join us October 5-8 in Denver, CO for four days of adversary tradecraft courses, evening events, and the most fun you’ll have leveling up your infosec skills. Registration is open: https:// ghst.ly/45COqlF
tweet mediatweet media
@SpecterOps avatar
SpecterOps @SpecterOps
19 Aug, 18:07 · core
0.34
Happening soon! Don't miss our upcoming webinar feat. Kaleb Pomeroy & @zinic discussing practical lessons on designing with MCP, including how security and access boundaries influence agent interactions. Save your spot! https:// ghst.ly/4hbh44x
tweet media
@Unit42_Intel avatar
Unit42_Intel @Unit42_Intel
19 Aug, 21:55 · secondary
0.32
Aeternum botnet leverages smart contracts on the Polygon blockchain to store and retrieve C2 instructions. Querying public RPC endpoints allows infected endpoints to execute immutable commands and evade takedowns. Read our full analysis: https:// bit.ly/45pDx6D
tweet mediatweet media
@SpecterOps avatar
SpecterOps @SpecterOps
19 Aug, 20:17 · core
0.32
"Can this role read that bucket?" and "Can it decrypt that key?" aren't the same question. @n0pe_sled 's latest blog post introduces AWSHound, free, self-hosted, turns AWS Orgs into real BloodHound CE attack paths. Check it out:
tweet media
@pdiscoveryio avatar
pdiscoveryio @pdiscoveryio
19 Aug, 18:01 · secondary
0.29
From Nuclei to Neo: Building AI for Cybersecurity Rishi shares how his experience as a security engineer led to the creation of Nuclei, how its open-source community shaped ProjectDiscovery, and why AI agents and LLMs represent the next step in vulnerability discovery. They
tweet media
@TalosSecurity avatar
TalosSecurity @TalosSecurity
19 Aug, 15:04 · secondary
0.22
What if we treated cyber attacks more like crime scenes? Learn how crime script analysis helps simplify complex threats for multi-level audiences and reveals new ways to stop attackers in their tracks: https:// cs.co/6015B1j08l
tweet media
@SpecterOps avatar
SpecterOps @SpecterOps
19 Aug, 23:36 · core
0.20
Don't miss our next #RedditAMA this Friday in the r/SpecterOpsCommunity subreddit! BloodHound Community member Tom O'Neill will answer your burning questions on DataHound and HoundTrainer. Submit your Qs https:// ghst.ly/4xdx9f4
tweet mediatweet media
@_xpn_ avatar
_xpn_ @_xpn_
19 Aug, 22:27 · core
0.20
Started Neuromancer on Audable before the Apple TV series starts, so many things in this book which I never knew originated from Gibson.. "Night City"
tweet media
@_RastaMouse avatar
_RastaMouse @_RastaMouse
19 Aug, 20:13 · core
0.20
Also. Quad bikes. Really fucking fun! Fun x.com/_rastamouse/st…
tweet media

Regular sources

6 items
1.00general · 19 Aug, 18:58darkreading.comAttack path

SilkParasite Threatens Central Asian Orgs With Flurry of RATs

A spear-phishing campaign by a Chinese-nexus group linked to FamousSparrow provides insight into geopolitical, technical, and strategic global moves by China's APTs.

1.00general · 19 Aug, 13:01thehackernews.comWild exploit

Critical macOS, SharePoint, vCenter, and Microsoft IKE Flaws Under Active Exploitation

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, sta…

1.00general · 19 Aug, 12:12bleepingcomputer.comRCE

Critical RCE flaw in Windows IKE Extension now actively exploited

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are exploiting a critical-severity remote code execution (RCE) flaw in the Windows I…

0.99general · 19 Aug, 11:03helpnetsecurity.com

Google’s AI security agents found 100+ critical software vulnerabilities in just two days

Google’s Mandiant has disclosed the workings of an internal tool that uses chains of AI agents to hunt for vulnerabilities in source code, saying it found over 100 verif…

0.84general · 19 Aug, 09:14helpnetsecurity.com

F5 enhances AI Gateway to control AI costs, access, and security

F5 has introduced enhancements to the F5 AI Gateway and integrated the solution into the F5 AI Security Platform. The enhanced F5 AI Gateway seamlessly enforces policies…