Generated 03/09/2026, 09:57. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources8
Tweets / X7
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
7 items
outflanknl @outflanknl
02 Sept, 20:30 · core
0.54
Outflank is proud to have collaborated with @SpecterOps on a new red team AI skills marketplace. This collection packages offensive security knowledge into reusable skills for AI agents. Read more on our blog:
🚨 On 9/1/26, #SonicWall disclosed 2 EITW vulns affecting SonicWall SMA1000 appliances. CVE-2026-83548 & CVE-2026-83549 can be chained to achieve unauthenticated RCE on affected appliances. Find mitigation guidance and …
Spring Ring is a social engineering operation targeting employees at 10 companies via external Microsoft Teams accounts. Attackers used voice phishing to deploy remote tools and attempt PetitPotam NTLM relay attacks against domain controllers: https:// bit.ly/4zK514Q
SSRF Fundamentals Discovery methodology. Parser bypasses. Blind exploitation chains. Cloud metadata attacks. Five chapters, one systematic path. This field runs deeper than most hunters ever go. https:// brutelogic.net/ebooks/ssrf-ma stery-series/fundamentals/ …
This looks genuinely cool! I've never done heavy research into recon (except accidentally via timing attacks), since it wasn't a viable standalone research target. This project may change that! Big news from Intigriti! 🎉 We're incredibly proud to introduce CrowdRecon! CrowdRecon
Day 1 of Fal.Con 2026 delivered. From major announcements on the keynote stage to a packed Hub, hands-on learning, live demos, Adversary Tradecraft, and plenty of competition, the Crowd came ready. And we’re just getting started. #FalCon2026
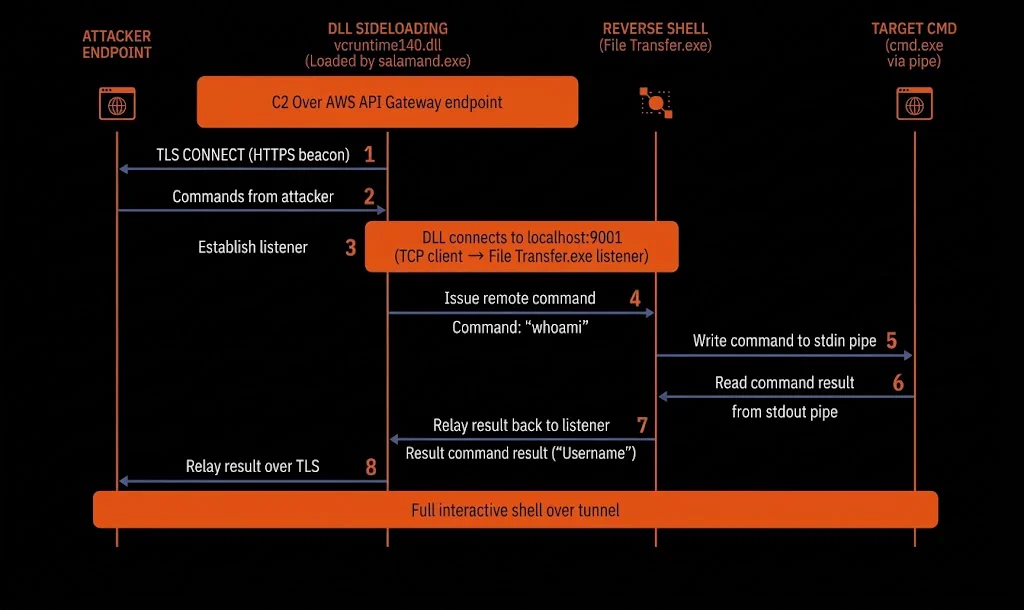
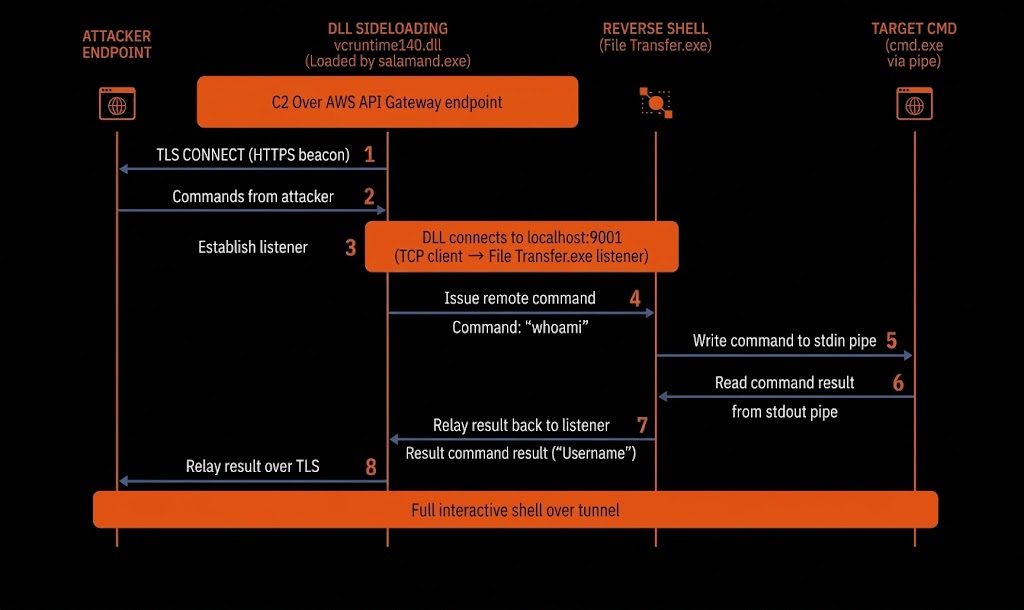
Fake IT support campaign delivers a malicious MSI that sideloads a trojanized DLL via a signed binary, then uses WMI to launch a custom reverse shell tunneled over a local port (localhost:9001) to an AWS API Gateway C2. Detection and indicators: https:// bit.ly/4ycFn7h
SonicWall SMA 1000 Zero-Days Enable Unauthenticated RCE
The exploitation activity follows attacks earlier this summer on two other zero-day vulnerabilities in the vendor's edge devices.
1.00exploit · 02 Sept, 16:24seclists.org
Multiple vulnerabilities in Jenkins and Jenkins plugins
Posted by Kevin Guerroudj on Sep 02 Jenkins is an open source automation server which enables developers around the world to reliably build, test, and deploy their softw…
1.00general · 02 Sept, 12:38securityweek.com
OpenAI’s Astra Crosses ‘Critical’ Cyber Threshold After Finding Zero-Days
The designation applies when a model can independently find and exploit zero-day vulnerabilities across many well-defended systems. The post OpenAI’s Astra Crosses ‘Crit…
Researchers Use Claude to Port Pre-Auth RCE Exploit From One PLC Model to Another
Forescout Research - Vedere Labs said it used Anthropic's Claude to port a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logi…
US charges Russian for infecting 80,000 freelancers with malware
A California federal grand jury has indicted a Russian national for his role in a phishing campaign that infected thousands of freelancers with TVRAT and DarkVNC malware…
0.89exploit · 02 Sept, 21:14seclists.org
Fwd: Vulnerabilities in golang.org/x/crypto
Posted by Alan Coopersmith on Sep 02 -------- Forwarded Message -------- https://pkg.go.dev/golang.org/x/crypto> in order to address the following security issues: ssh:.…
Posted by Sam James on Sep 02 Werner Koch writes: Hi Werner! Nono, it's OK, I very much understand. We are suffeirng the same and I nearly even wrote something about how…