Generated 13/08/2026, 09:55. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources2
Tweets / X13
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
13 items
Jhaddix @Jhaddix
12 Aug, 20:20 · core
0.70
This is a must - MUST - for anyone interested in AI, red teaming, and attacking AI. Over 71 free prompt injection labs and more to be added (and removed) next week! https:// arcanum-sec.github.io/ai-sec-resourc es/ … And If you you want to learn how to pentest and hack AI systems
Over 71 free prompt injection labs and more to be added (and removed) next week! https:// arcanum-sec.github.io/ai-sec-resourc es/ … And If you you want to learn how to pentest and hack AI systems check out: Attacking AI: https:// arcanum-sec.com/training/attac king-ai/ …
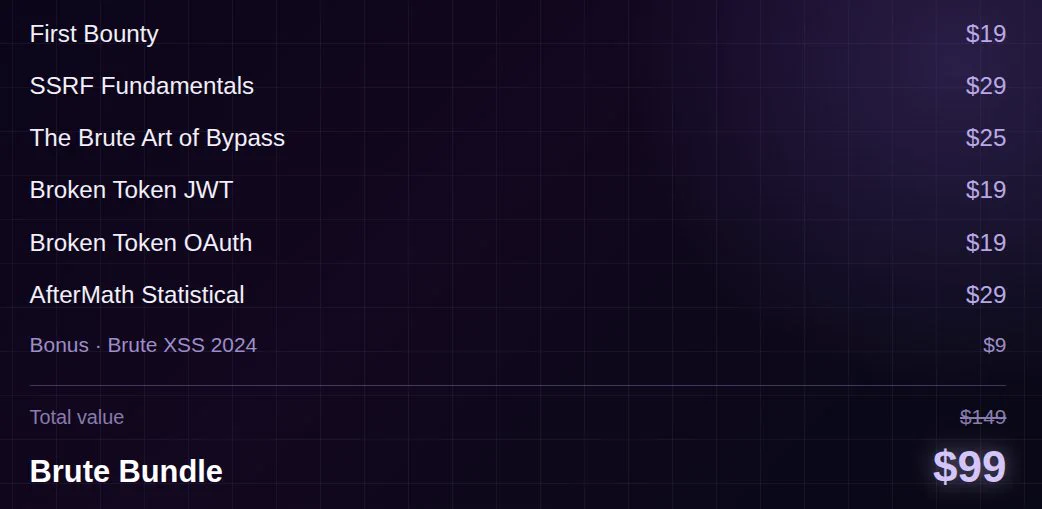
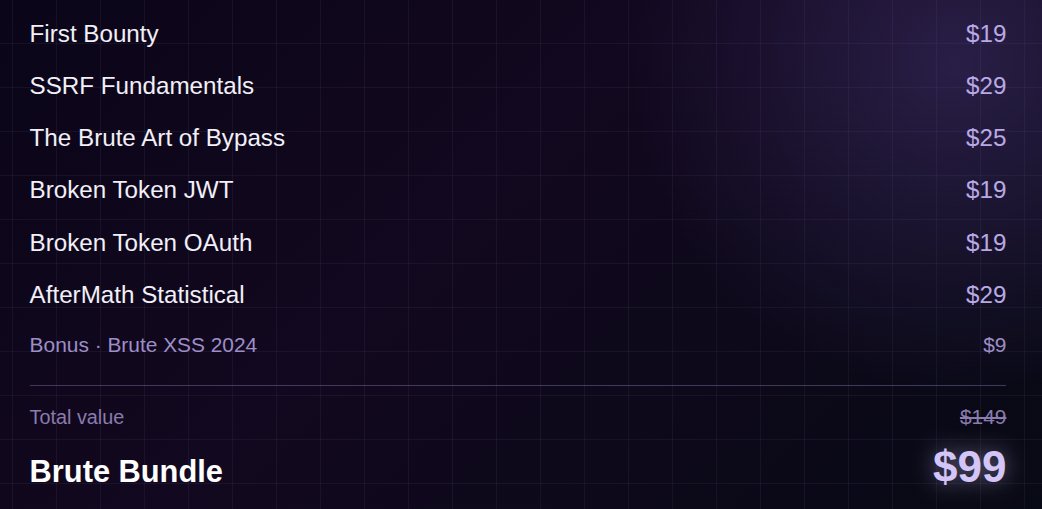
Training data for any brain. @Grok Brute Bundle AfterMath Statistical, Broken Token JWT and OAuth, SSRF Fundamentals, The Brute Art of Bypass and First Bounty. Cryptographic oracles, token forgery, SSRF chains, WAF/filter evasion and bug bounty fundamentals. https:// brutelogic.n
PSA: Several sources claim there was a golden retriever at Blackhat and Defcon… I did not see this in person, but next time I demand that you bring this good girl or boy to me for belly scratches and/or collaboration on stage.
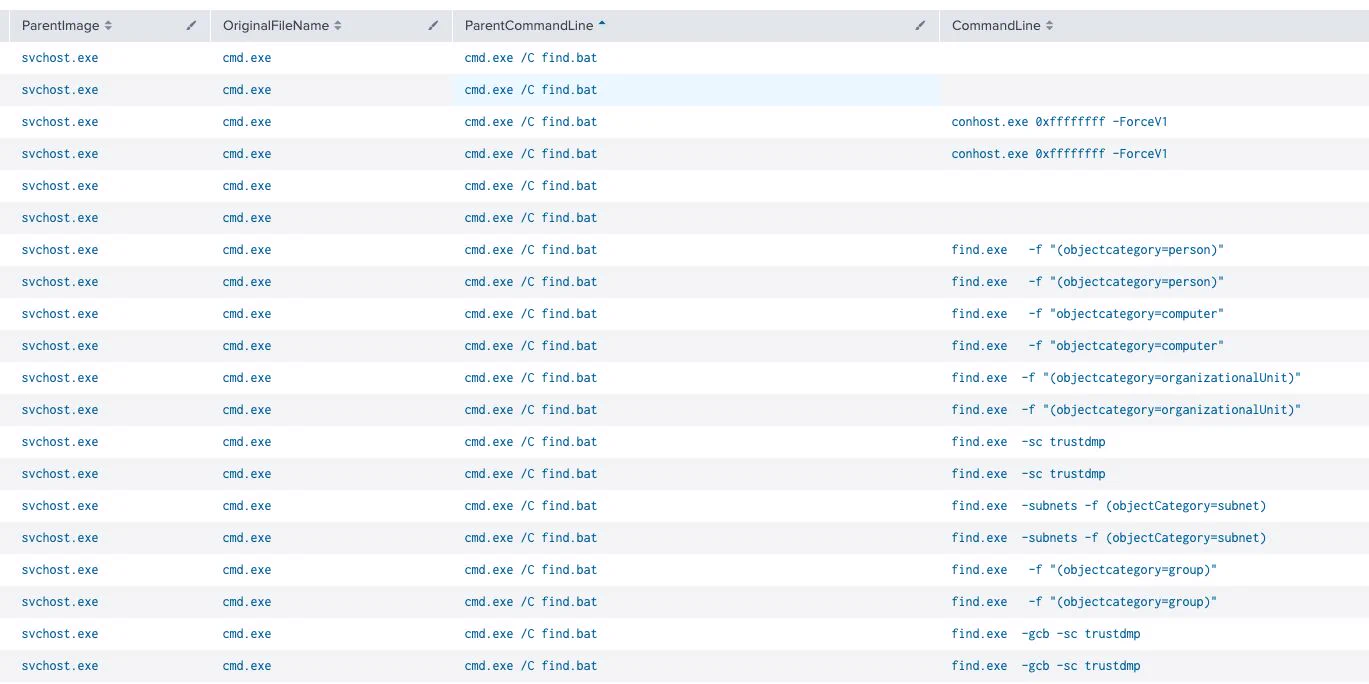
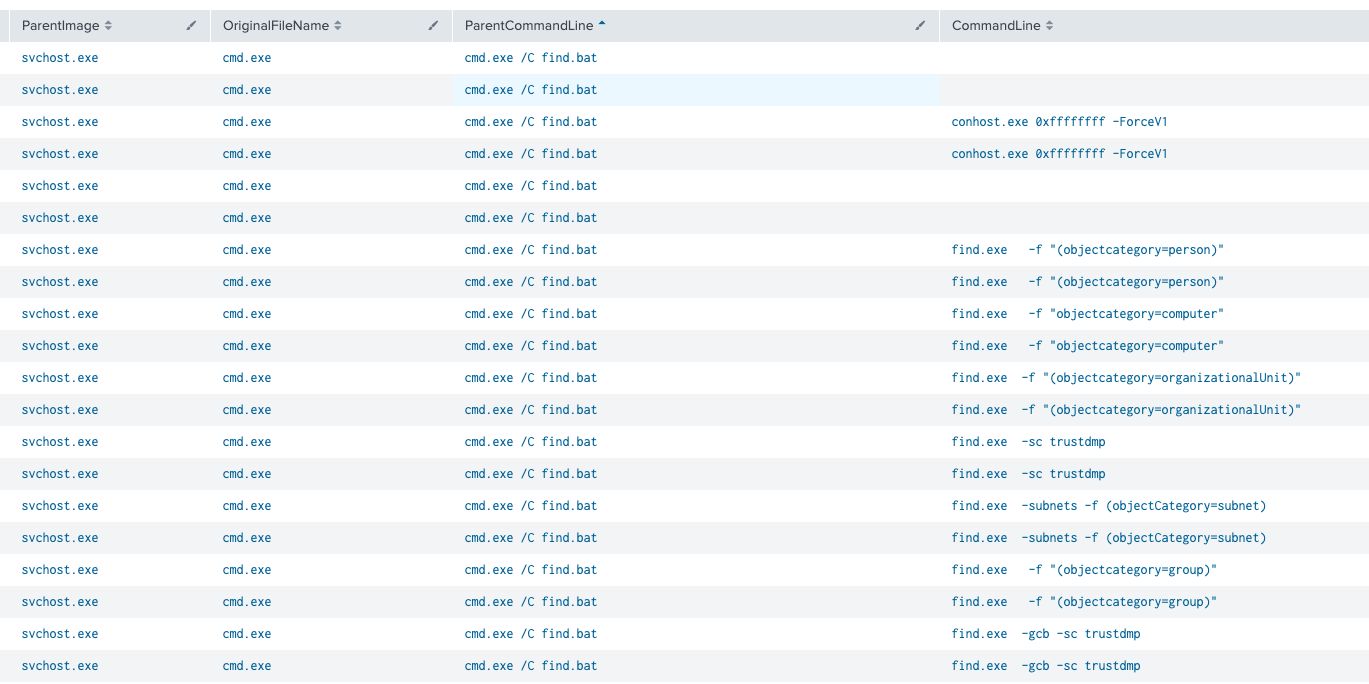
"AdFind.exe, the command-line Active Directory query tool, was run on only one of the compromised hosts via the find.bat batch script." Read the full report: https:// buff.ly/ojcAXgo #DFIR #ThreatIntel
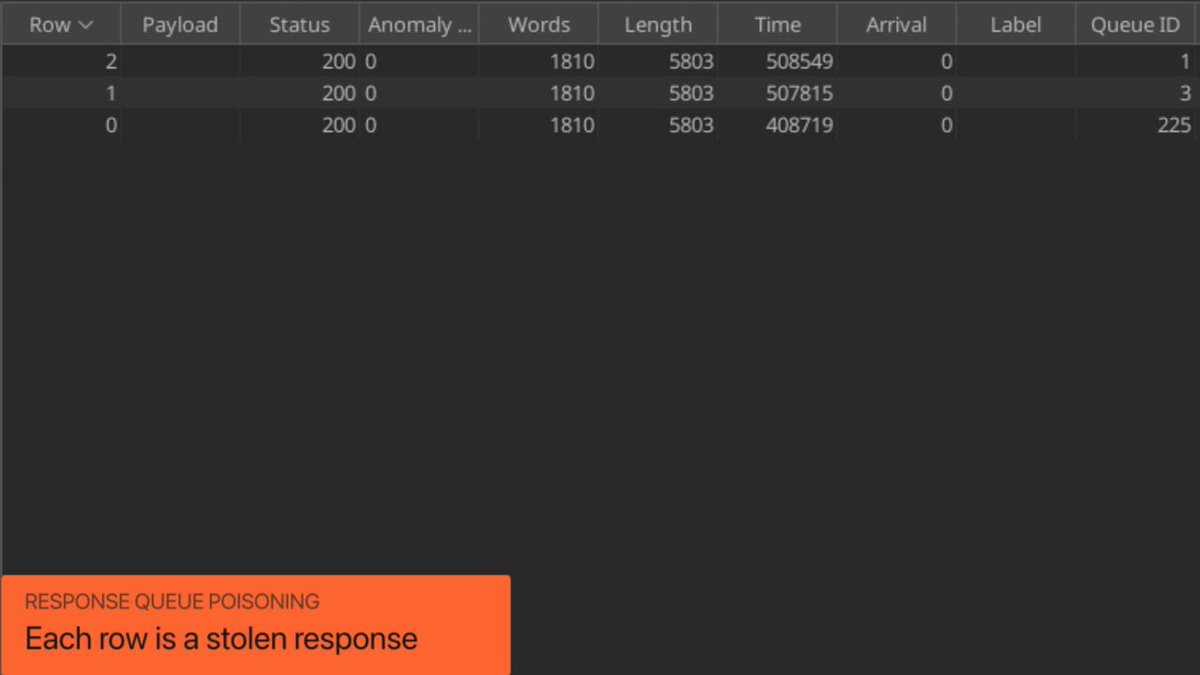
Did you know you can use HTTP header injection to trigger response queue poisoning and make it rain credentials? Learn how with the new @PortSwiggerRes whitepaper "CRLF-Powered Desync Attacks: Beheading HTTP Streams" by @m4st3rspl1nt3r and I. Read the full paper below
For all those asking at Blackhat if I thought that infosec would die with SOTA models getting so good... When I was in China it was insinuated that every lab did this. I’m glad there’s public research on it and am still shocked the frontier labs haven’t patched this stuff. We don
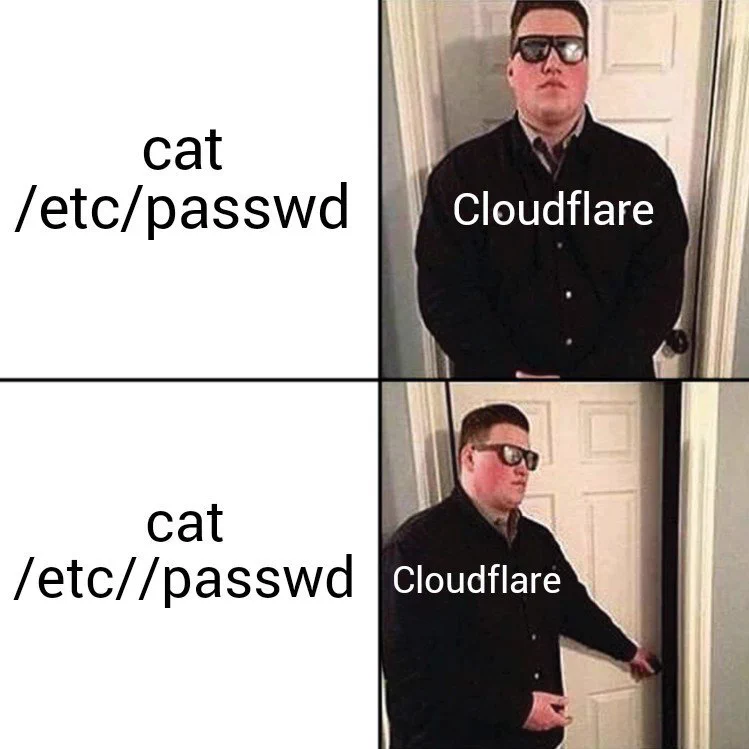
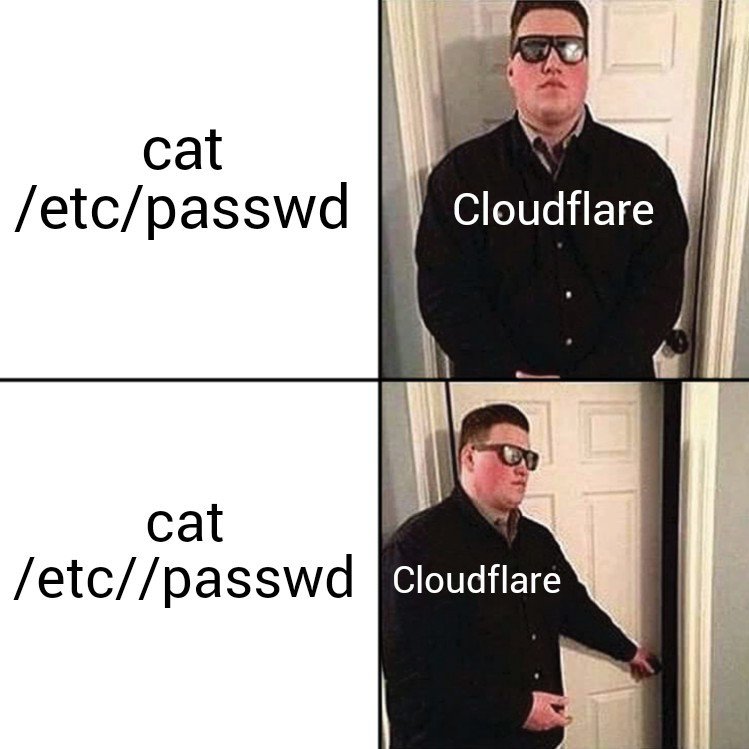
I've been bypassing CloudFlare here on X consistently on every payload I share. Try to post this here on X with just 1 slash between etc and passwd to see for yourself. Bash RCE Bypass Tricks Empty Quote Split c''at /etc//passwd Brace Expansion {cat,/etc//passwd} IFS Space Replac
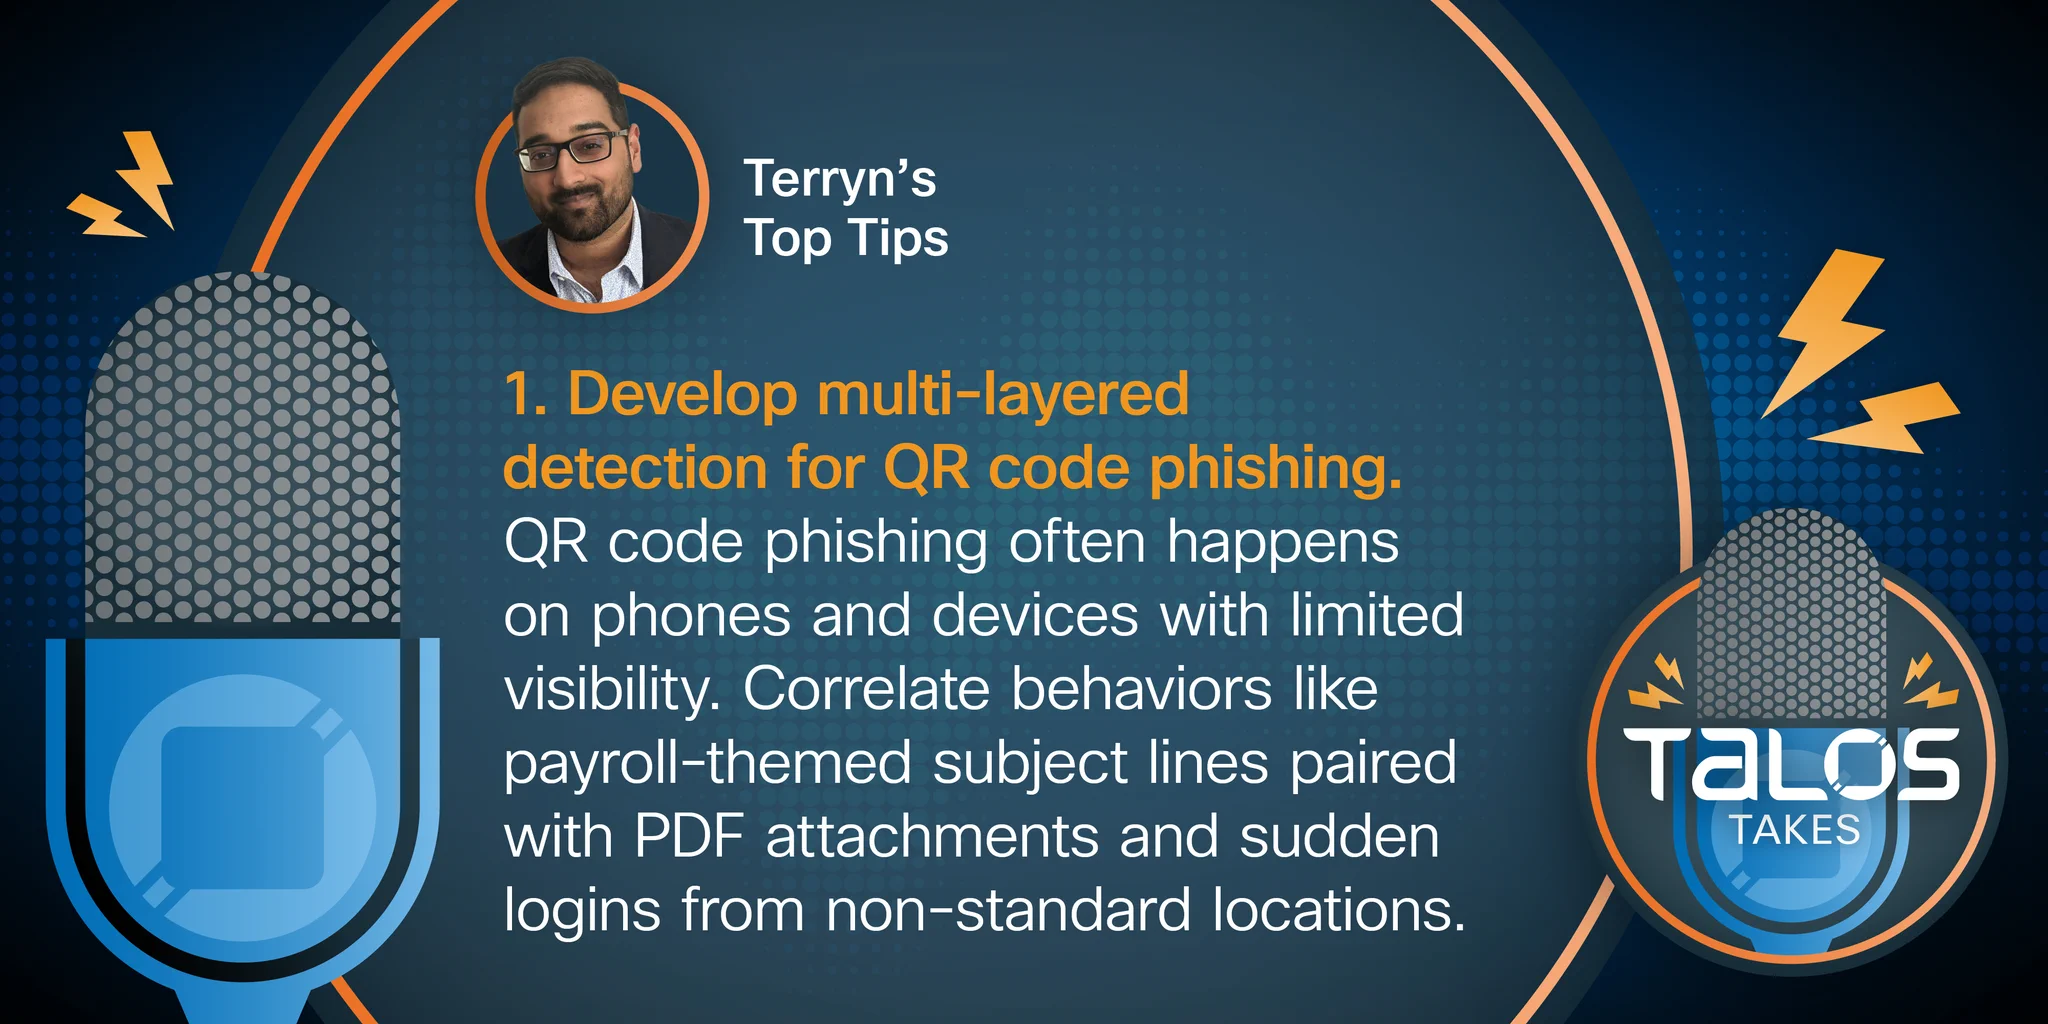
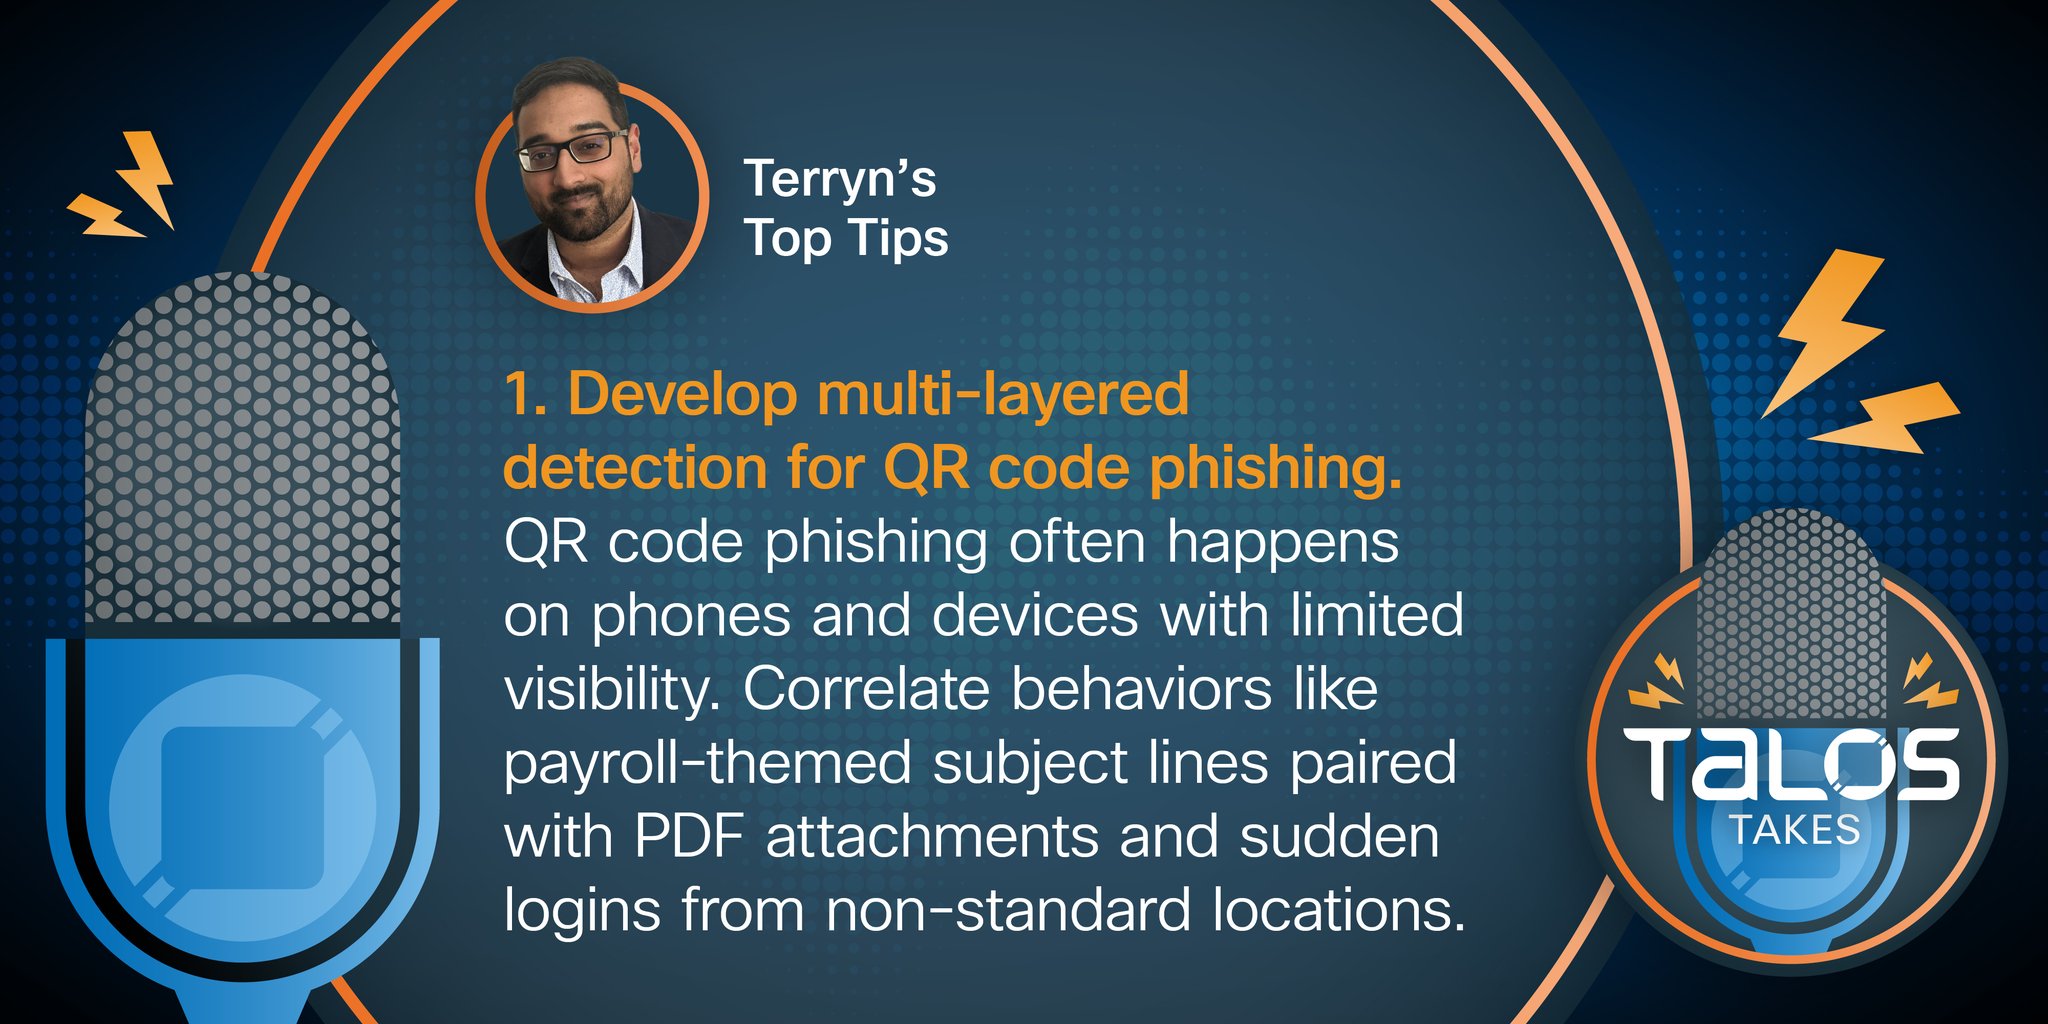
What does it take to defend against a cloud-native attack? After walking us through a real Talos IR case involving QR code phishing, Terryn shared his go-to strategies for staying ahead of the game. Take a look and a listen: https:// buzzsprout.com/2018149/episod es/19625475 …
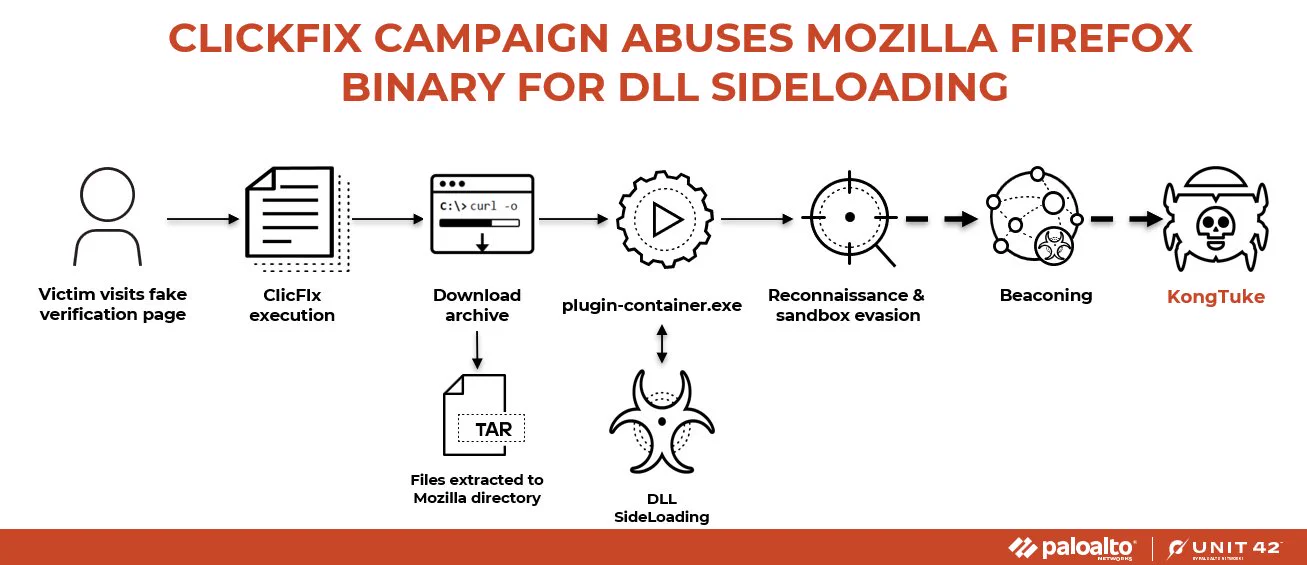
An increase in #ClickFix campaigns delivers KongTuke payloads by abusing legitimate Mozilla binary. Features Rust-based DLLs masquerading as Firefox components with capabilities like AMSI bypass, shell execution, screenshot capture, persistence. Details: https:// bit.ly/45jZ0hr
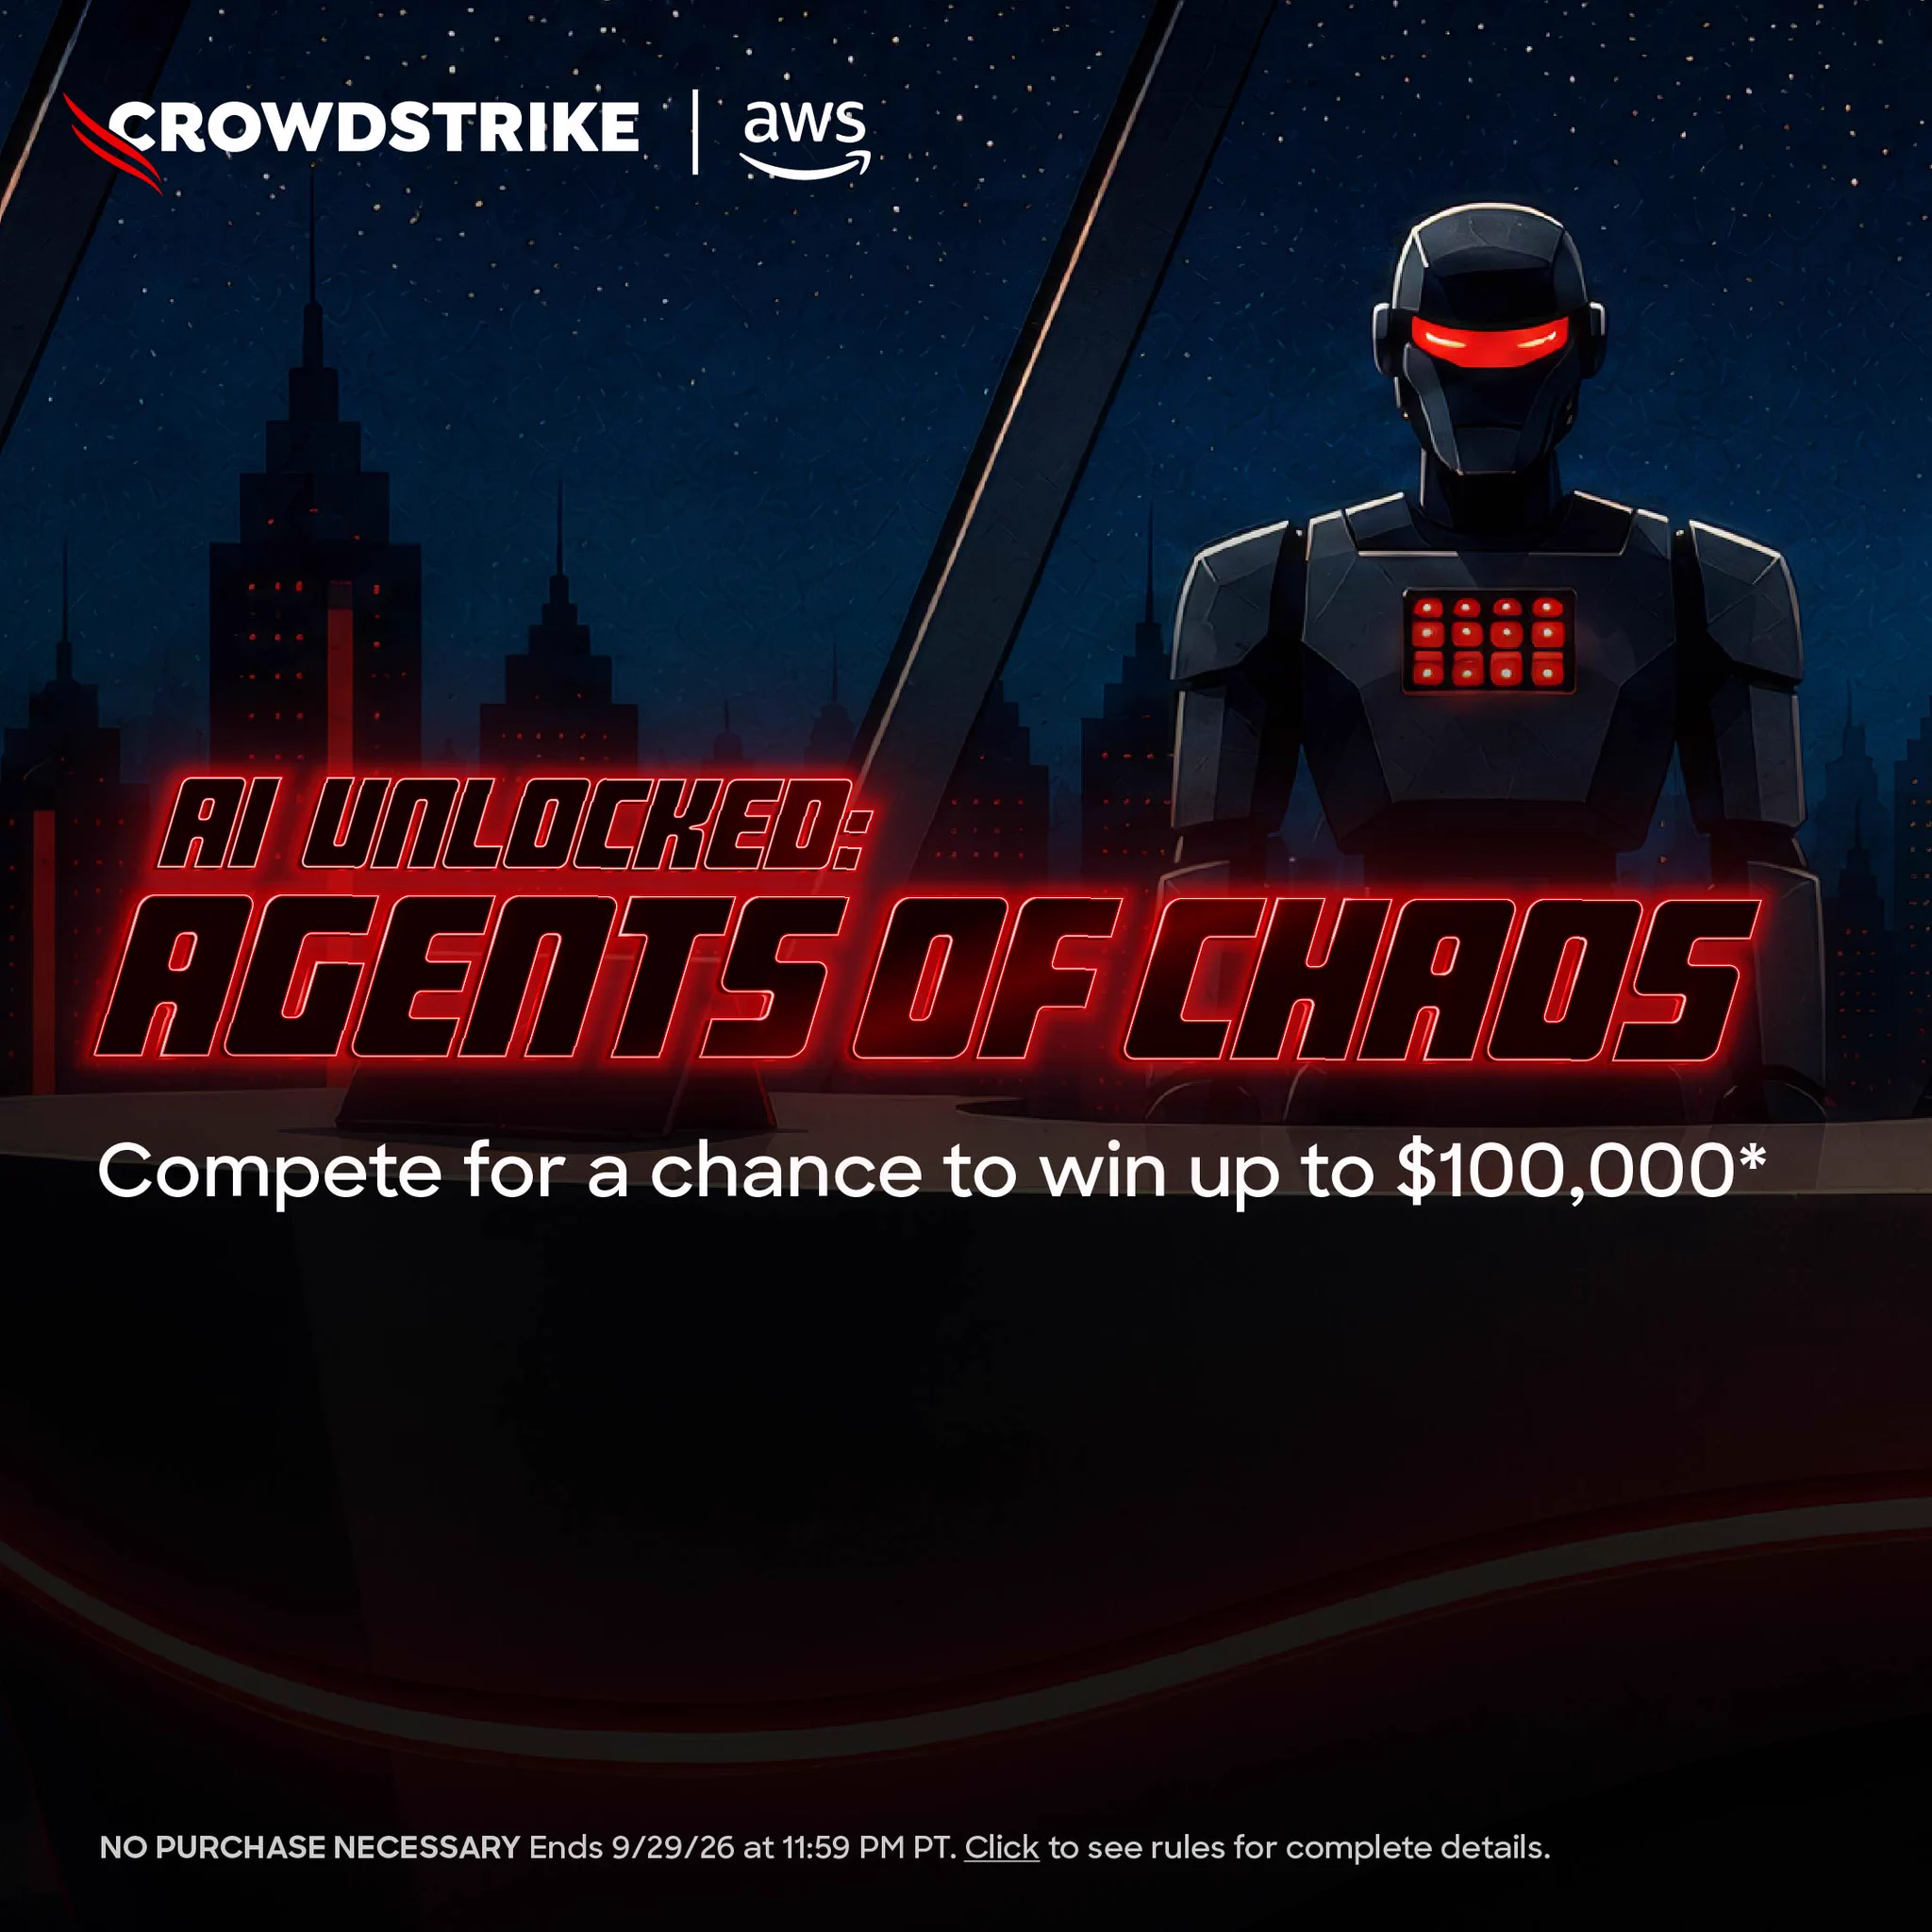
AI Unlocked: Agents of Chaos The greatest threat isn't outside your environment - it's already inside. A new interactive AI security challenge is coming soon from CrowdStrike and AWS. Step into the role of a deep-cover operative, infiltrate the Agents of Chaos shadow
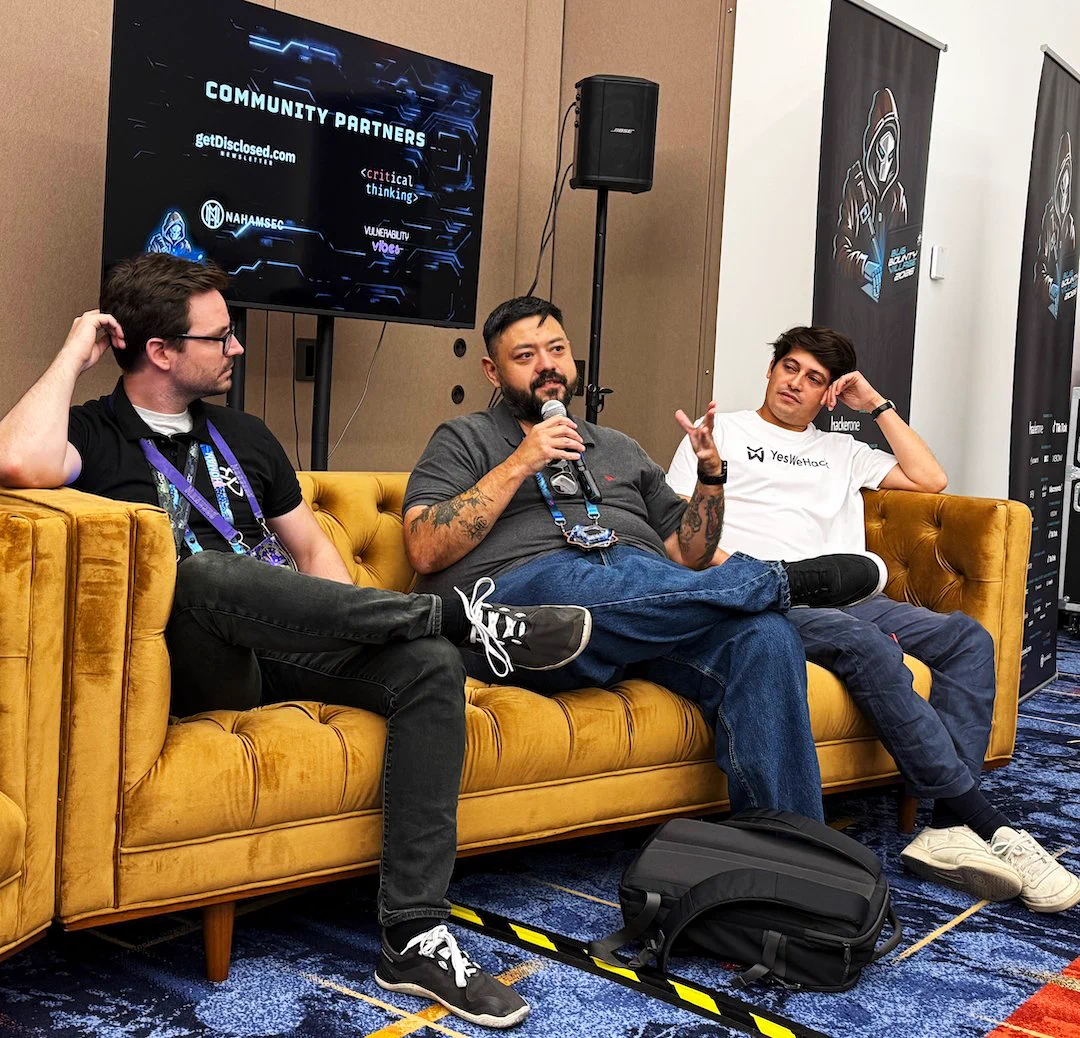
Last week at DEF CON 34, Synack’s Eddie Rios joined a panel at Bug Bounty Village to discuss the rise of AI-assisted submissions and how researchers can succeed in 2026 and beyond. Thank you, @BugBountyDEFCON , for a great event!
SharePoint Vulnerability Exploited Shortly After PoC Release
The vulnerability was patched by Microsoft in July and CISA warned that it could end up being exploited in the wild. The post SharePoint Vulnerability Exploited Shortly …