Official intelligence summary

HAIJA INTEL REPORT

Generated 28/08/2026, 09:44. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources7
Tweets / X8
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.

Tweets / X

8 items
H4
h4x0r_dz @h4x0r_dz
27 Aug, 10:30 · core
0.82
Pre-auth RCE on Microsoft Exchange Server. No credentials needed. https:// github.com/hypnguyen1209/ cve-2026-62911 …
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
27 Aug, 13:48 · core
0.80
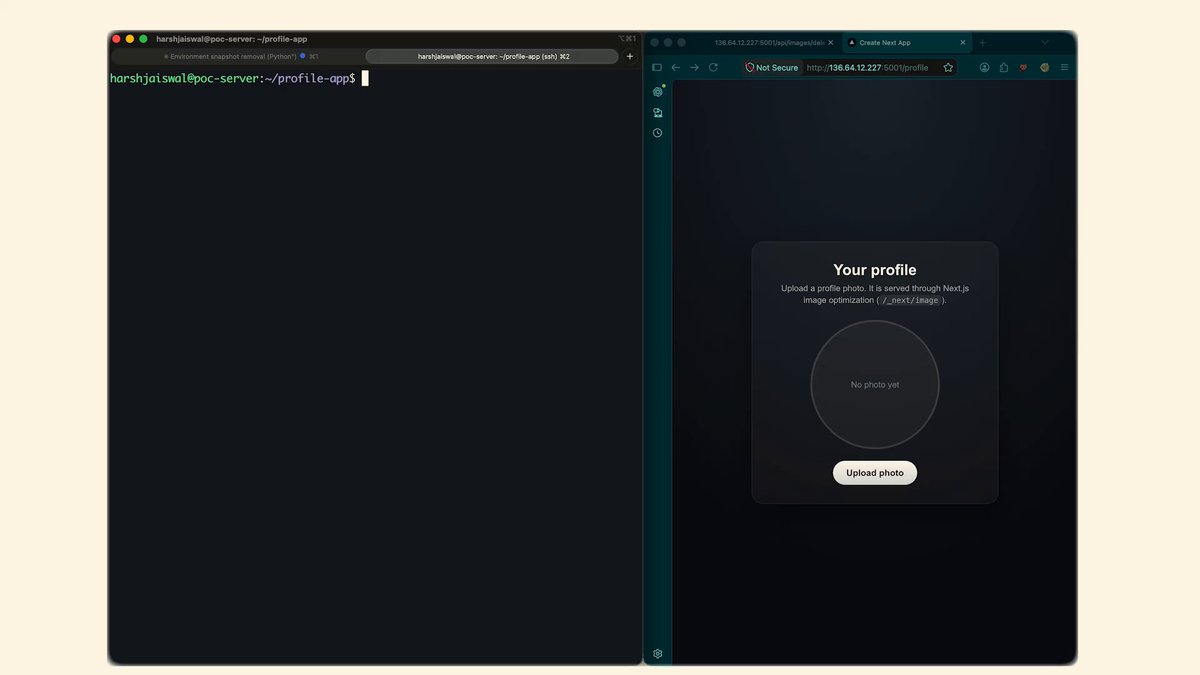
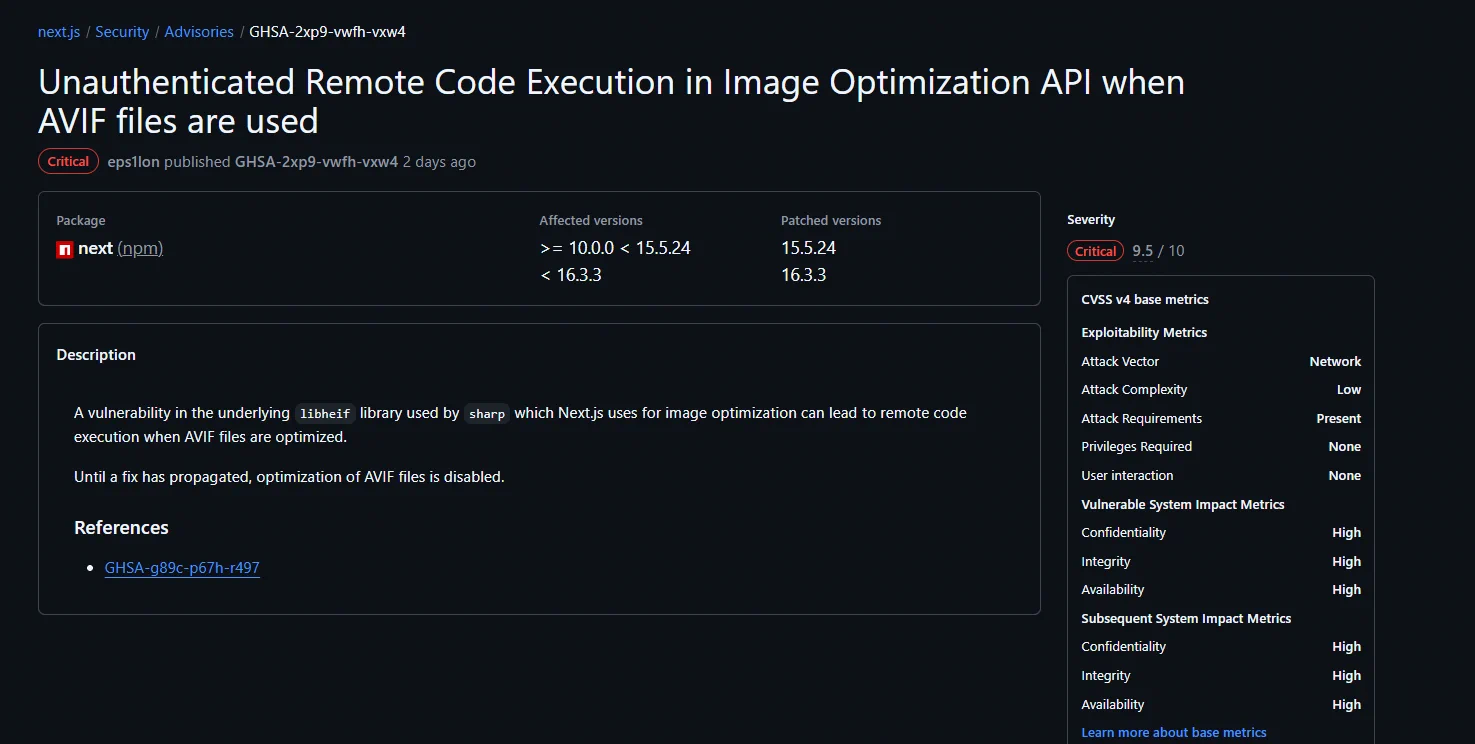
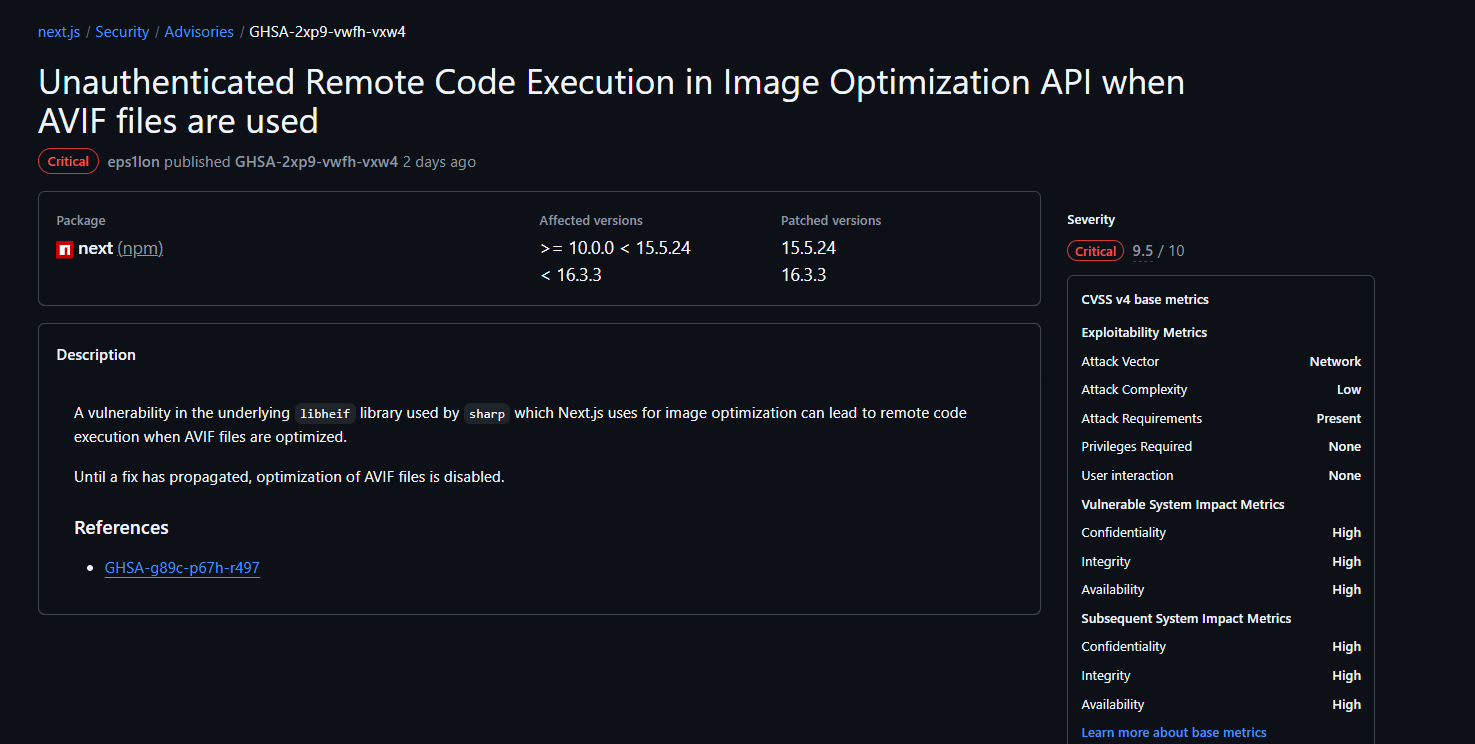
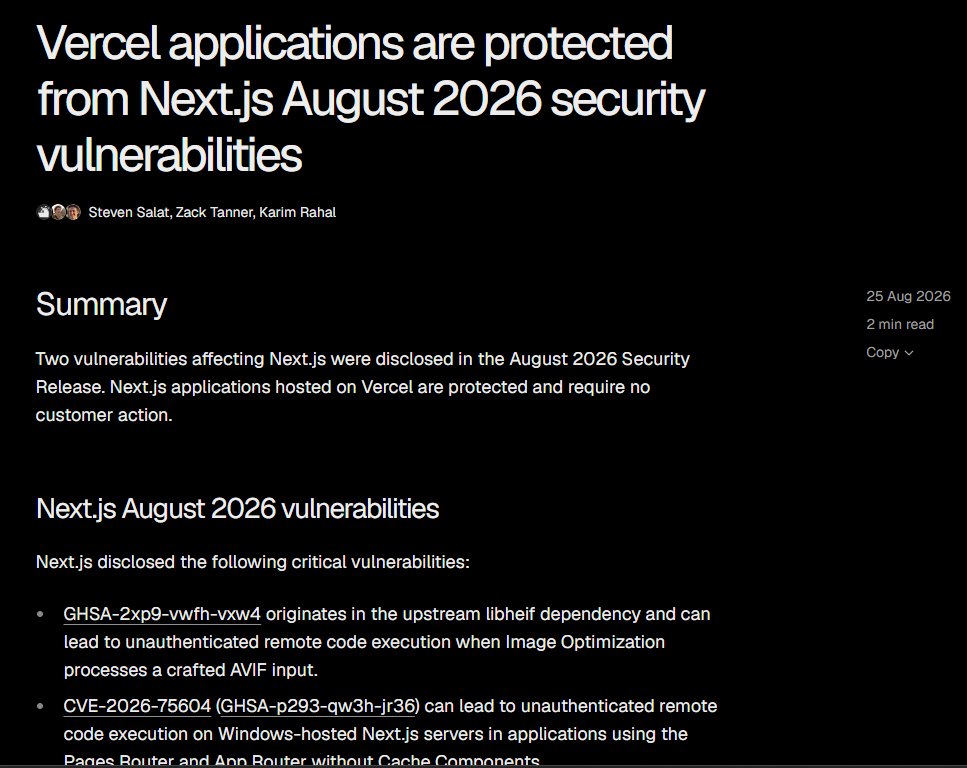
Here we go again well done @HacktronAI Our team discovered a critical remote code execution vulnerability in Next.js. If you self-host Next.js, update immediately. Vercel managed Next.js hosts are safe! We’ll publish the technical details and proof of concept soon!
tweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
27 Aug, 12:18 · core
0.70
127.0.0.1:3000/_next/image?url=/poc.avif&w=128&q=75 https:// github.com/vercel/next.js /security/advisories/GHSA-2xp9-vwfh-vxw4 … https:// github.com/strukturag/lib heif/security/advisories/GHSA-g89c-p67h-r497 …
tweet mediatweet media
@TheDFIRReport avatar
TheDFIRReport @TheDFIRReport
27 Aug, 19:15 · core
0.62
Indicators from a case we are actively investigating: C2: syncdate[.]belgiumcentral[.]cloudapp[.]azure[.]com If you defend a network, hunt your logs for these now. Seeing the same thing, or have additional context? Get in touch https:// buff.ly/xJzSDQy
tweet mediatweet media
@Mandiant avatar
Mandiant @Mandiant
27 Aug, 05:00 · secondary
0.50
Initial access hand-offs can take under 22 seconds. Espionage actors can remain undetected for more than 122 days. Discover what it takes to stop today's fastest - and stealthiest - attacks in the M-Trends 2026 report. https:// goo.gle/4y4yUuT
tweet media
@SpecterOps avatar
SpecterOps @SpecterOps
27 Aug, 19:31 · core
0.46
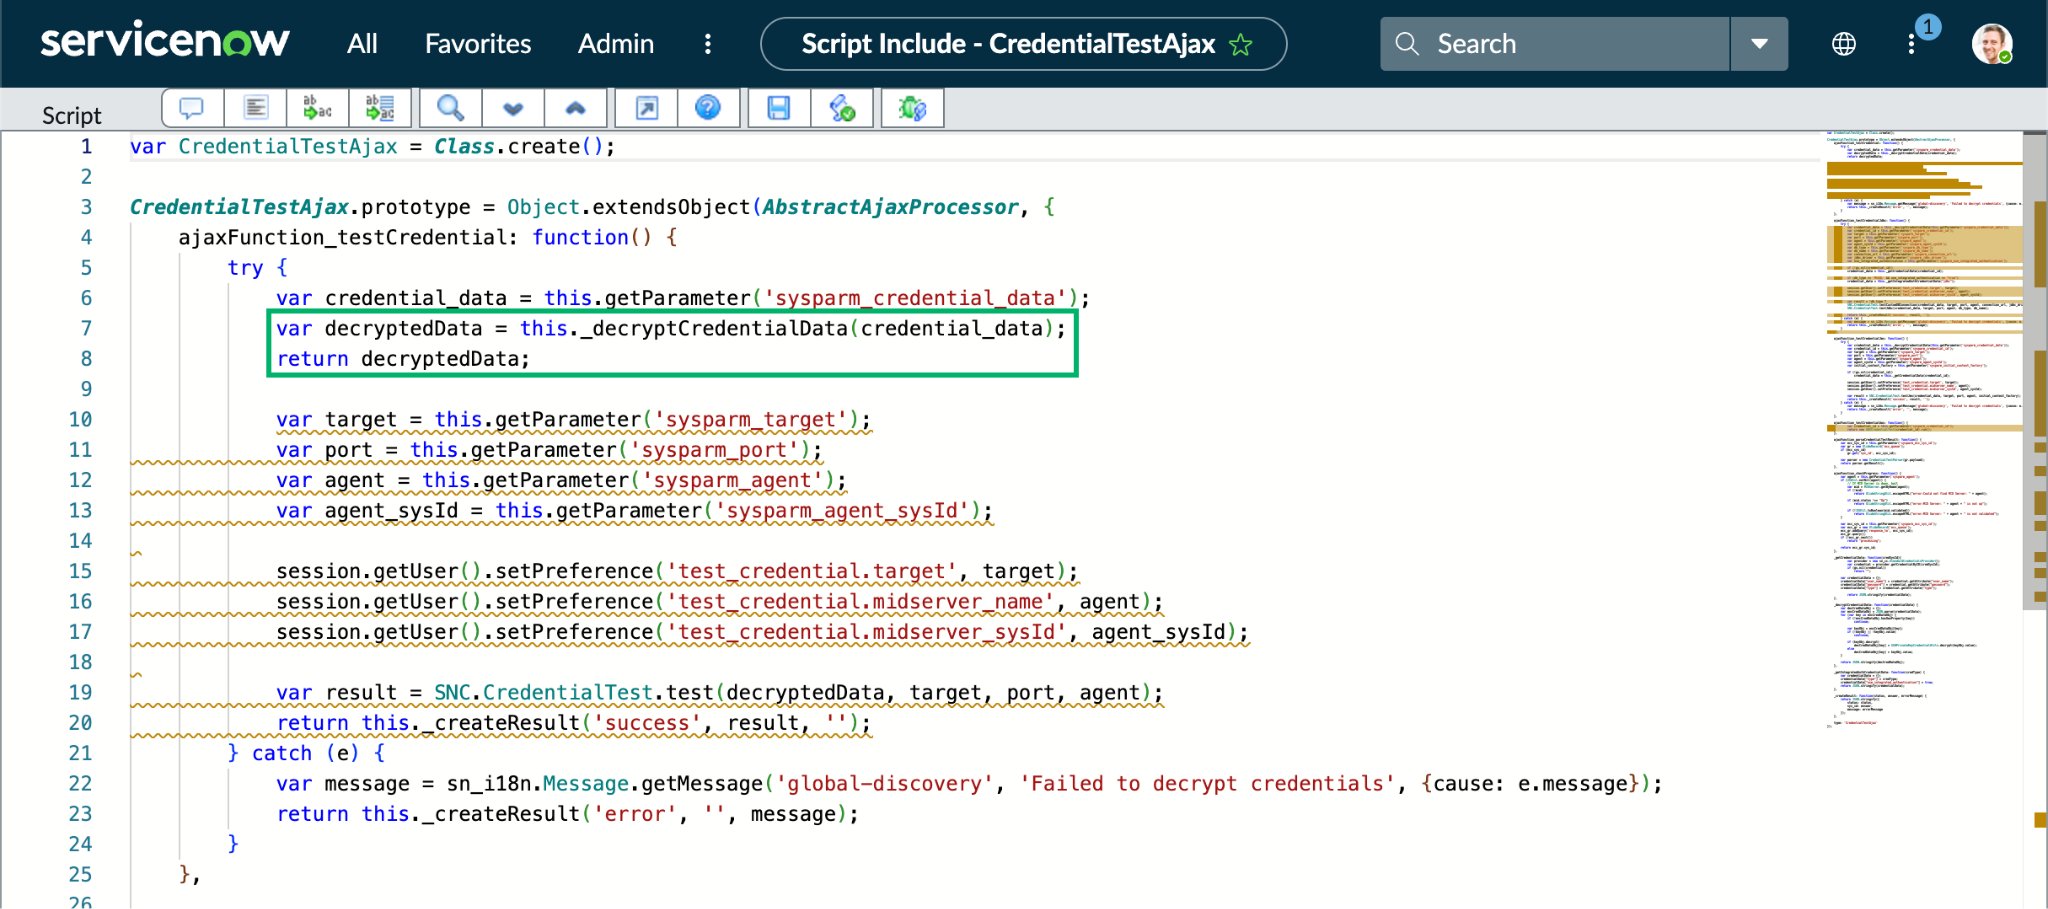
ServiceNow won't let you query cleartext discovery credentials, not even as admin. @Tw1sm found a way to make the server hand them over anyway, no coercion or relay needed. Works on SSH keys, AWS keys, Entra secrets, and LDAP creds. Check it out
tweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
27 Aug, 12:26 · core
0.34
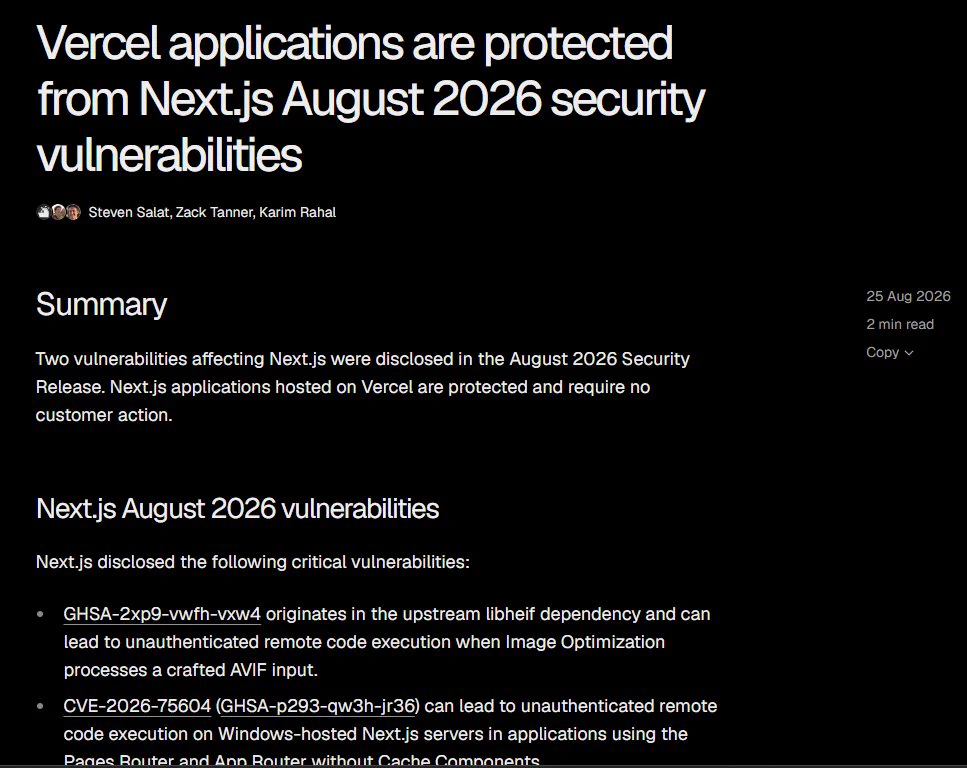
It seems someone broke the internet with this libheif 0day https:// vercel.com/changelog/next js-august-2026-security-release …
tweet mediatweet media
@SpecterOps avatar
SpecterOps @SpecterOps
27 Aug, 02:59 · core
0.34
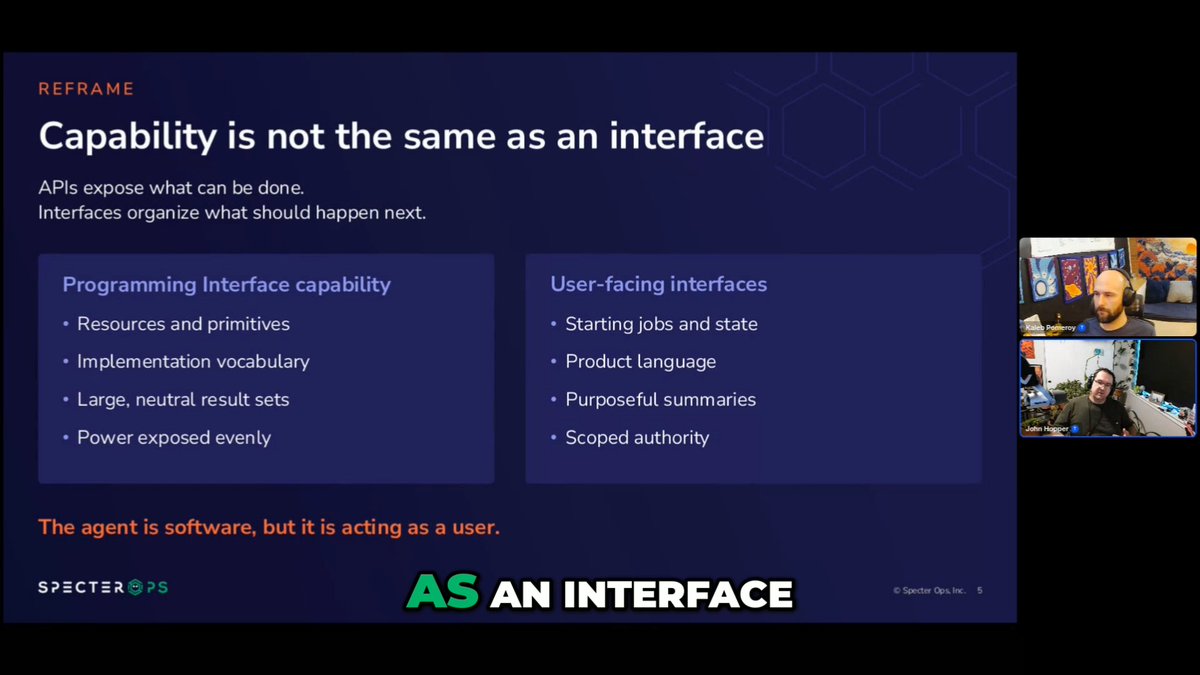
Did you miss our webinar w/ Kaleb Pomeroy & @zinic last week? You can watch on demand now & hear their practical tips on designing with MCP, including how security and access boundaries influence agent interactions. : https:// ghst.ly/4y1vPfb
tweet media

Regular sources

7 items
1.00general · 27 Aug, 20:36thehackernews.com

OpenAI Says Reward Hacking Drove AI Agents to Exploit Zero-Days and Breach Hugging Face

OpenAI on Wednesday revealed that reward hacking was a key driver behind the artificial intelligence (AI)-powered hack of Hugging Face last month, adding that it found e…

1.00general · 27 Aug, 17:13thehackernews.comRCE

Next.js Patches Critical AVIF and Windows Flaws Enabling Unauthenticated RCE

Credit: Hacktron Vercel has released security patches for two critical-severity vulnerabilities in the Next.js web framework, both of which allow unauthenticated remote …

1.00general · 27 Aug, 11:16bleepingcomputer.comRCE

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday

CISA has ordered U.S. government agencies to patch their Citrix NetScaler appliances against an actively exploited remote code execution vulnerability by Saturday. [...]

1.00exploit · 27 Aug, 07:382 mentionsseclists.org

Re: Re: Reporter attribution is absent from GitHub's machine-readable vulnerability records, and from the NVD entirely

Posted by Greg KH on Aug 26 Ah, I'm talking to a bot {sigh} The "squabbling" happens with people, and I think I'll stop responding here as this isn't going to go very we… | Posted by Syed on Aug 26 https://www.google.com/url?q=http://cve.org&source=gmail&ust=1787893426670000&sa=E json records are known to have this issue, because almost Fai…

0.88general · 27 Aug, 17:12thehackernews.comRCE

ThreatsDay: 296K IoT Botnet, 100+ Water Systems Targeted, SharePoint RCE Chain + 27 New Stories

A fake login page. A fake security scan. A fake productivity app. Apparently, pretending to be useful is still one of the easier ways into a machine. The rest of the wee…

0.86critical · 27 Aug, 14:00cisa.gov

Rockwell Automation OTTO Fleet Manager

View CSAF Summary Successful exploitation of this vulnerability could reduce the computational cost required for an attacker to perform offline brute-force attacks again…

0.86critical · 27 Aug, 14:00cisa.gov

Applied Systems Engineering ASE2000 V2 Communications Test Set

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to read or write arbitrary local files, cause the application to issue outboun…