Generated 08/09/2026, 10:02. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources7
Tweets / X8
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
8 items
h4x0r_dz @h4x0r_dz
07 Sept, 12:53 · core
0.70
what a crazy chain here 🚨🚨🚨🚨🚨🚨 From Padding Oracle to Shell: Unauthenticated RCE in Telerik UI for ASP[.]NET AJAX https:// tantosec.com/blog/2026/09/t elerik-padding-oracle-to-shell/ … The vulnerabilities described in this post were discovered, analysed, and exploited with
i had AI read all 1,520 bug bounty reports i've submitted since 2014 and told it not to protect my feelings. Three things i didn't want to hear: - the bugs that built my career don't exist anymore - my dupe rate went UP over 12 years - 685 of those reports never paid me a
Had to change some wording, some people thought this was malware written by the Israel government. This malware is masquerading as an Israel government domain to try to convince people to execute a goop (malware) payload.
I looked at this goop masquerading as the Israel government. I don't know anything about Israeli stuff, so maybe someone can provide context on what these Threat Actors are trying to achieve. > israel[.]gov[.]2026[.]vercel[.]app > domain still live, don't shoot yourself in the
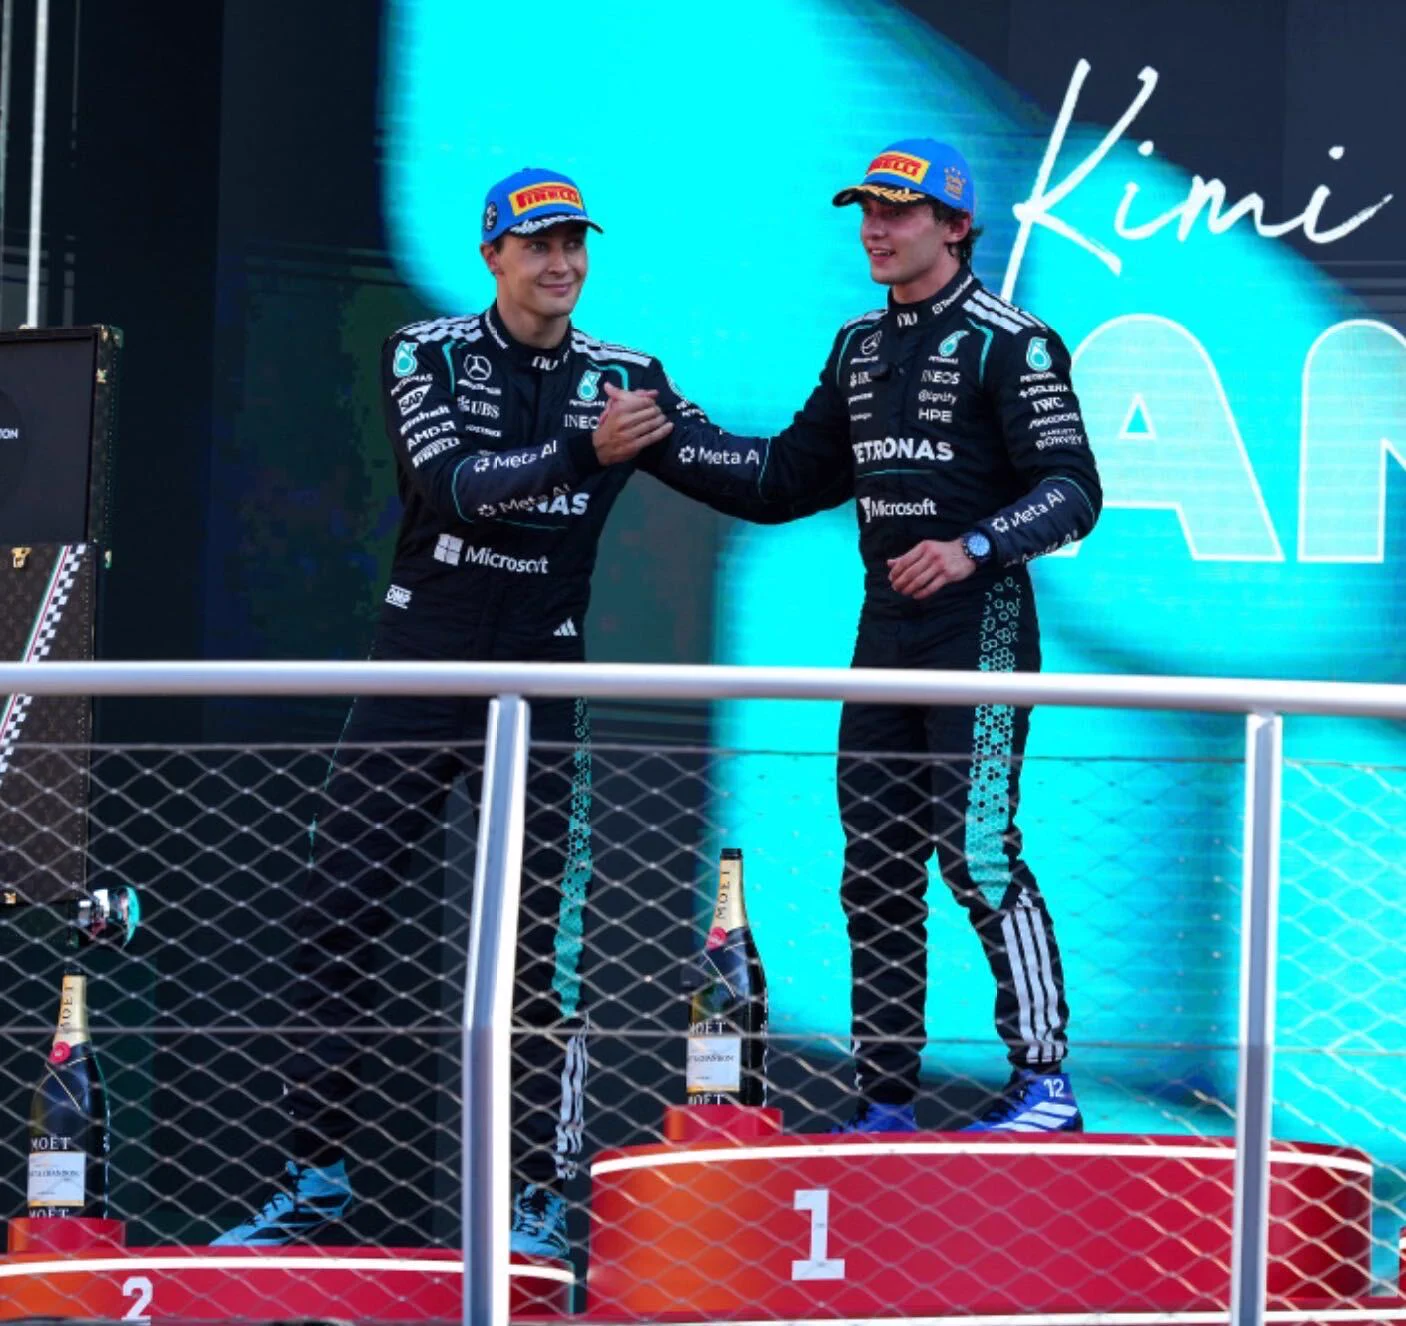
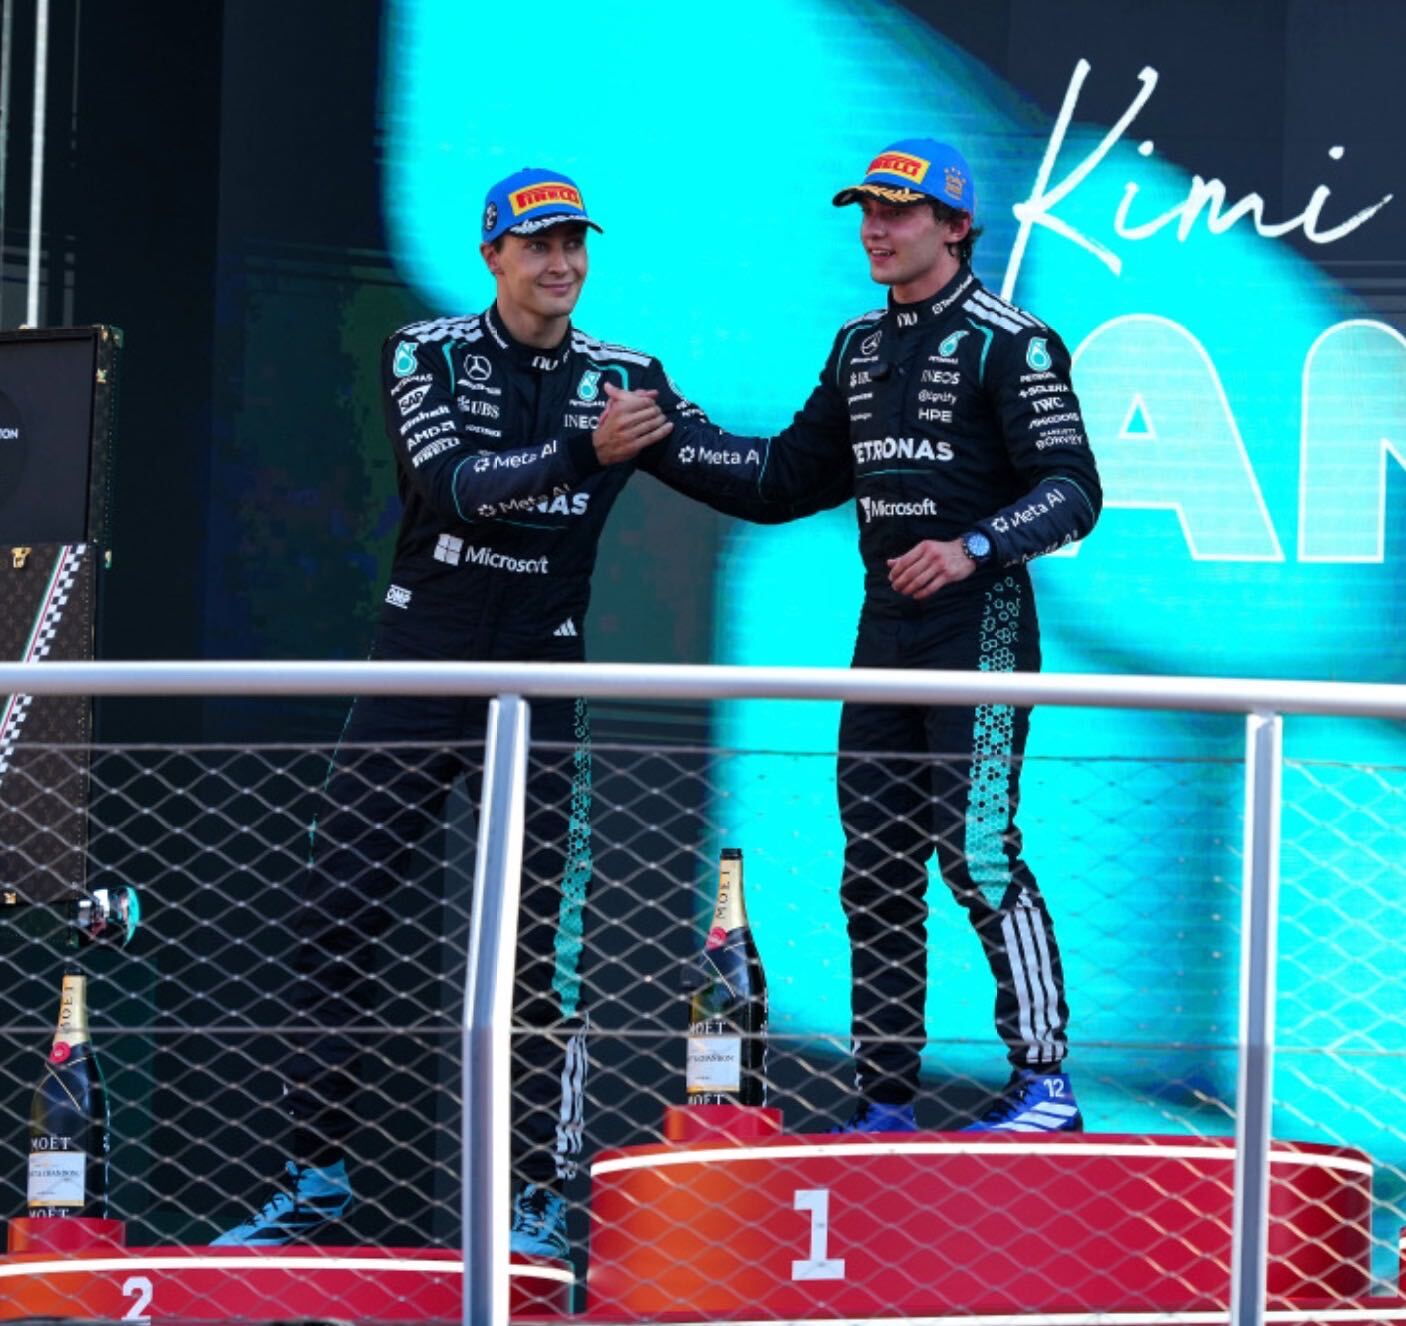
Congratulations to @MercedesAMGF1 , Kimi Antonelli and @GeorgeRussell63 on a brilliant 1 - 2 finish at the Italian Grand Prix. The “Temple of Speed” delivered a fantastic backdrop for the Silver Arrows to lock out the top two steps of the podium! 🏆
I think too many people are just yoloing code without understanding what or how their vibe coding is doing/working. Sometimes you can get to A to Z by vibe coding. But oftentimes you're getting (A to F) + (N to Z) and the model is telling you it did A to Z. And you're not
This #LaborDay, we’re celebrating the hard work and dedication of people everywhere who help their teams and communities thrive. Wishing everyone a safe and relaxing holiday with family and friends!
The proof-of-concept (PoC) exploits lead to privilege escalation, spawning a shell with System privileges. The post Nightmare Eclipse Drops CrowdStrike, Nvidia, Avast Ze…
N-able patches critical N-central zero-day exploited in the wild (CVE-2026-86218)
N-able released an emergency hotfix for CVE-2026-86218, a remote code execution (RCE) flaw affecting N-central, its remote monitoring and management (RMM) solution popul…
Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE - Public Exploit Released
A TantoSec proof-of-concept turns an AES-CBC "padding oracle" in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution - but only against applications i…
N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw
Every on-premises N-central build below 2026.3.1.14 - including servers updated to Hotfix 3 a day earlier - needs Hotfix 4. N-able's incident notice says the flaw has be…
N-able patches max severity N-central flaw amid ongoing attacks
N-able has released an emergency hotfix for a maximum-severity remote code execution (RCE) flaw affecting its N-central remote monitoring and management (RMM) platform. …
0.93general · 07 Sept, 18:50bleepingcomputer.com
Magento StyleSmuggler zero-day exploited to deploy Linux backdoor
A zero-day vulnerability dubbed "StyleSmuggler" affecting all versions of Magento and Adobe Commerce is being exploited in attacks to deploy a backdoor. [...]
0.93general · 07 Sept, 13:58securityweek.com
Adobe Commerce Zero-Day Exploited to Backdoor Online Stores
The StyleSmuggler zero-day allows attackers to execute code and deploy a stealthy backdoor on Adobe Commerce and Magento stores. The post Adobe Commerce Zero-Day Exploit…