Generated 14/08/2026, 09:37. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources6
Tweets / X9
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.
Tweets / X
9 items
Mandiant @Mandiant
13 Aug, 01:00 · secondary
0.43
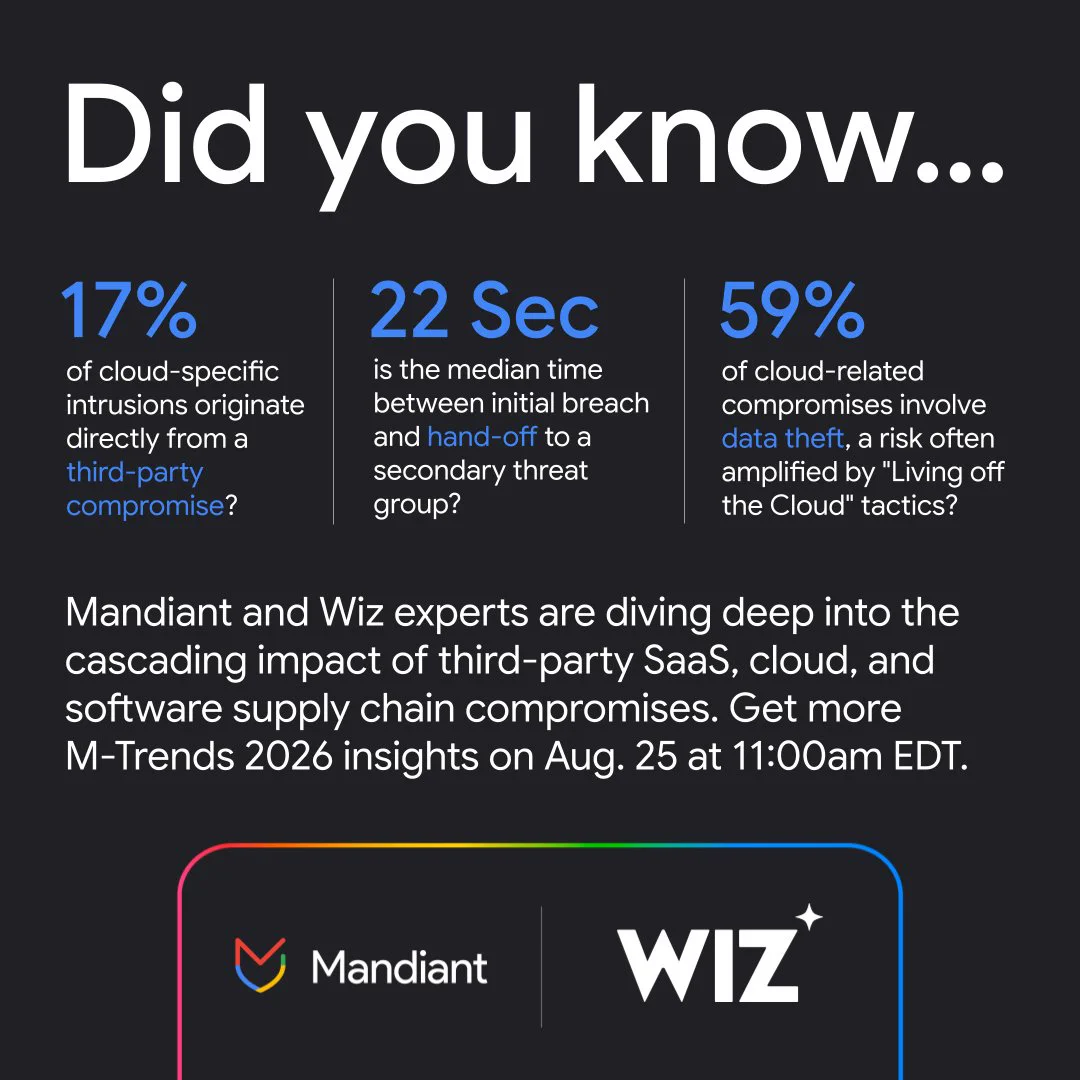
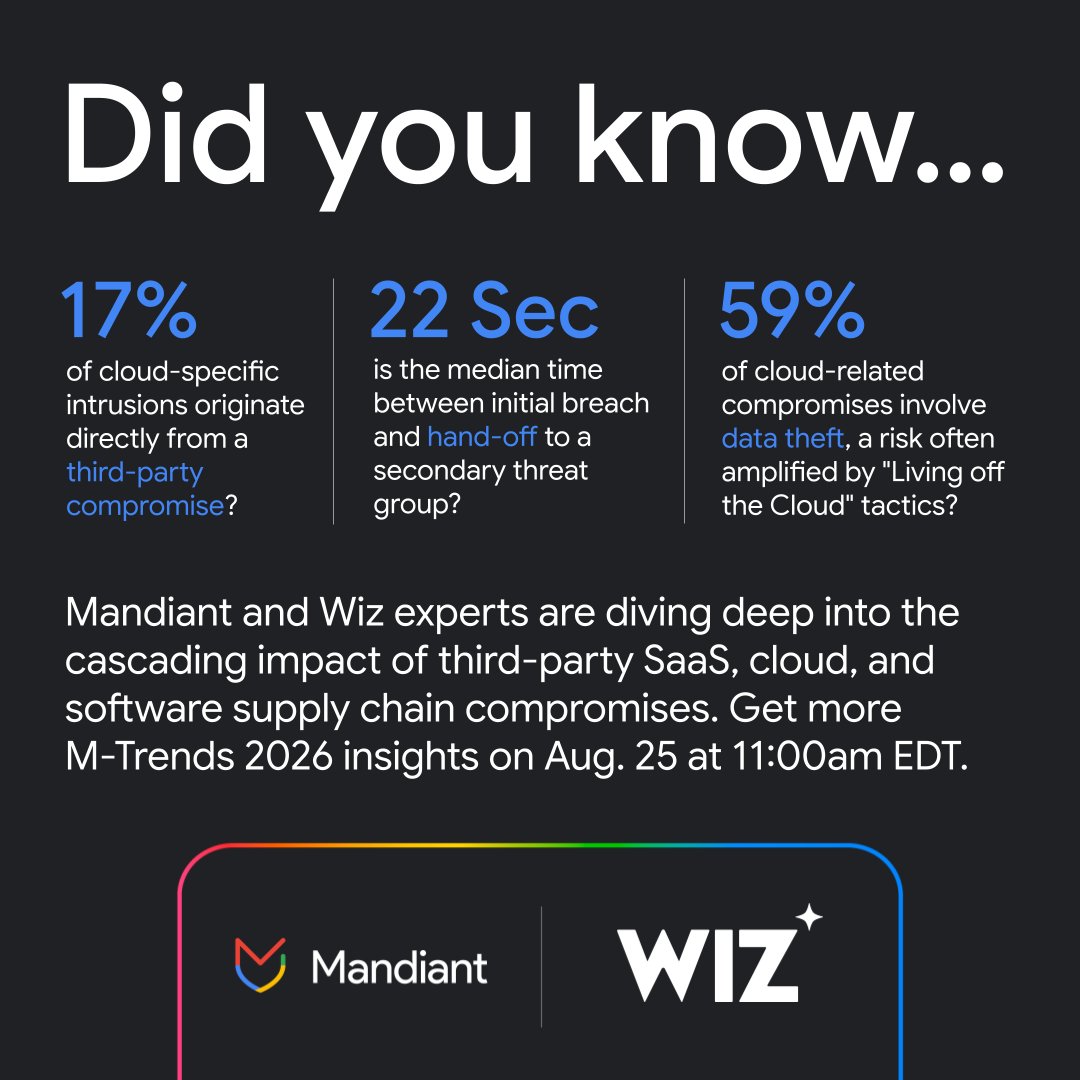
Adversaries are exploiting cloud services and open-source supply chains to launch large-scale attacks. How do you defend? We're diving deeper with @wiz_io during the final session of our M-Trends 2026 Virtual Series. Register: https:// goo.gle/4qdw4kF
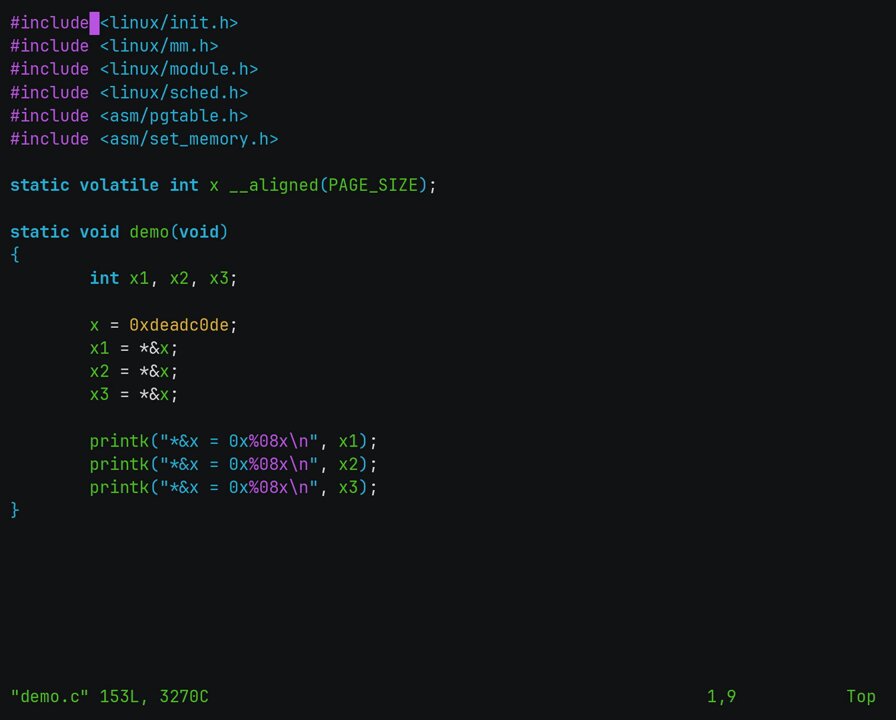
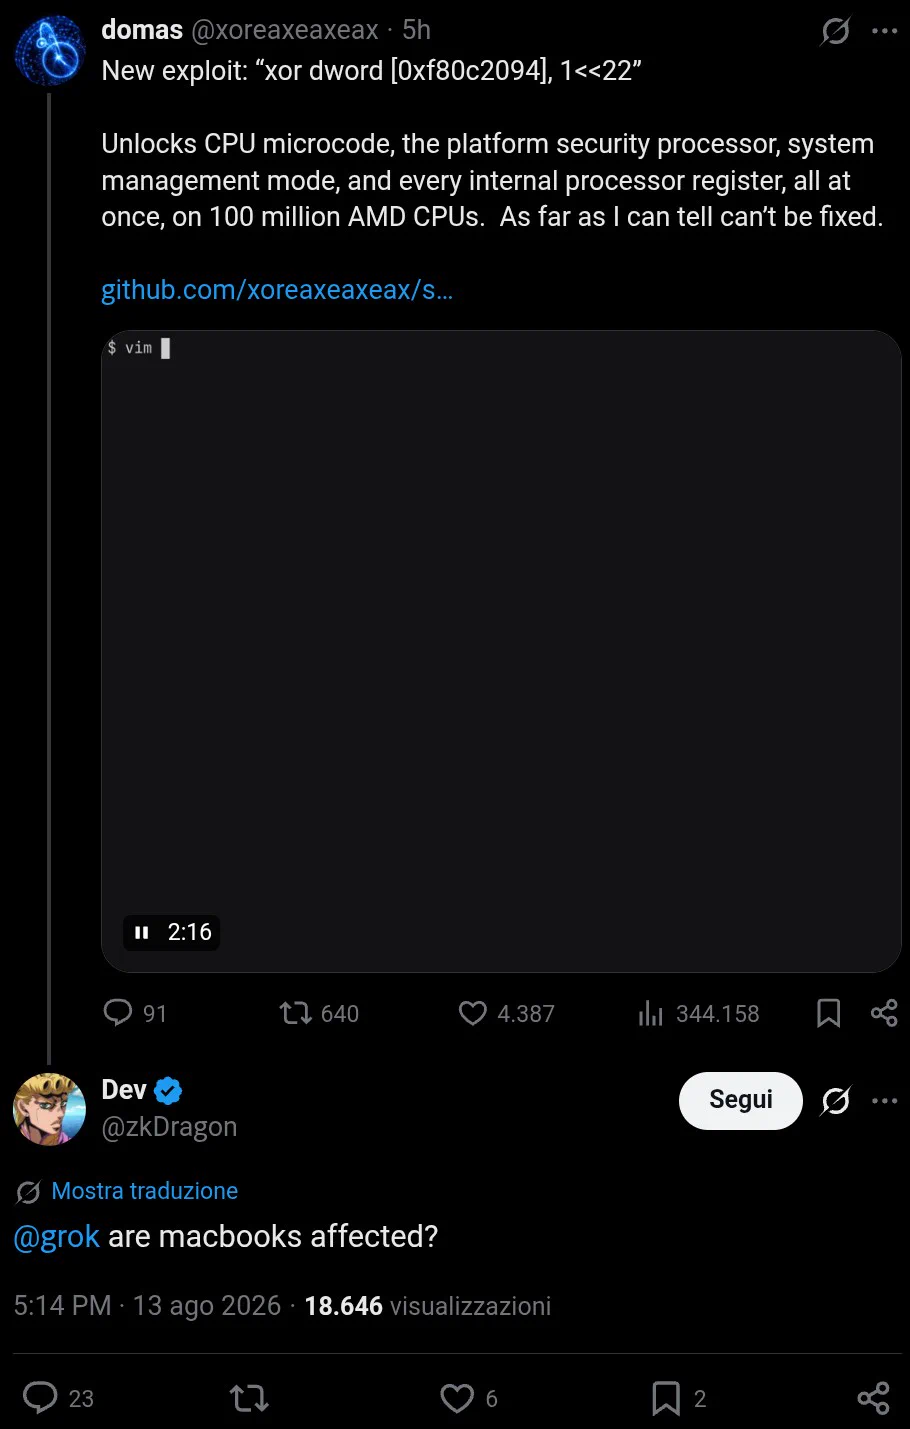
some of the craziest shit ive seen while also simultaneously being the simplest shit ive ever seen New exploit: “xor dword [0xf80c2094], 1<<22” Unlocks CPU microcode, the platform security processor, system management mode, and every internal processor register, all at once, on 1
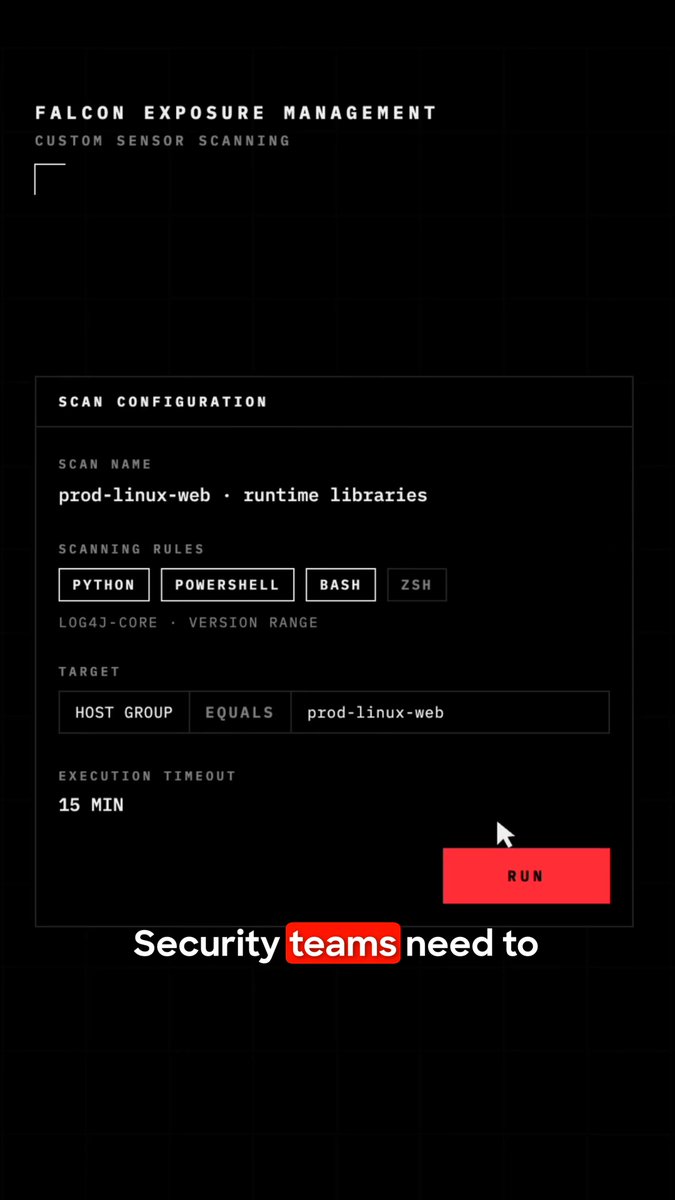
Not every vulnerability arrives with a CVE. Zero-days, emerging supply chain issues, and proprietary software risks can demand validation before standardized detection content exists. Custom Sensor Scanning in Falcon Exposure Management gives organizations the
Your browser is a C2 agent waiting to happen. @KingOfTheNOPs shows how to silently sideload a Chromium extension, no prompts or GUI, and turn Chrome/Edge into a persistent implant with SOCKS, cookie theft, and OS access. Read more
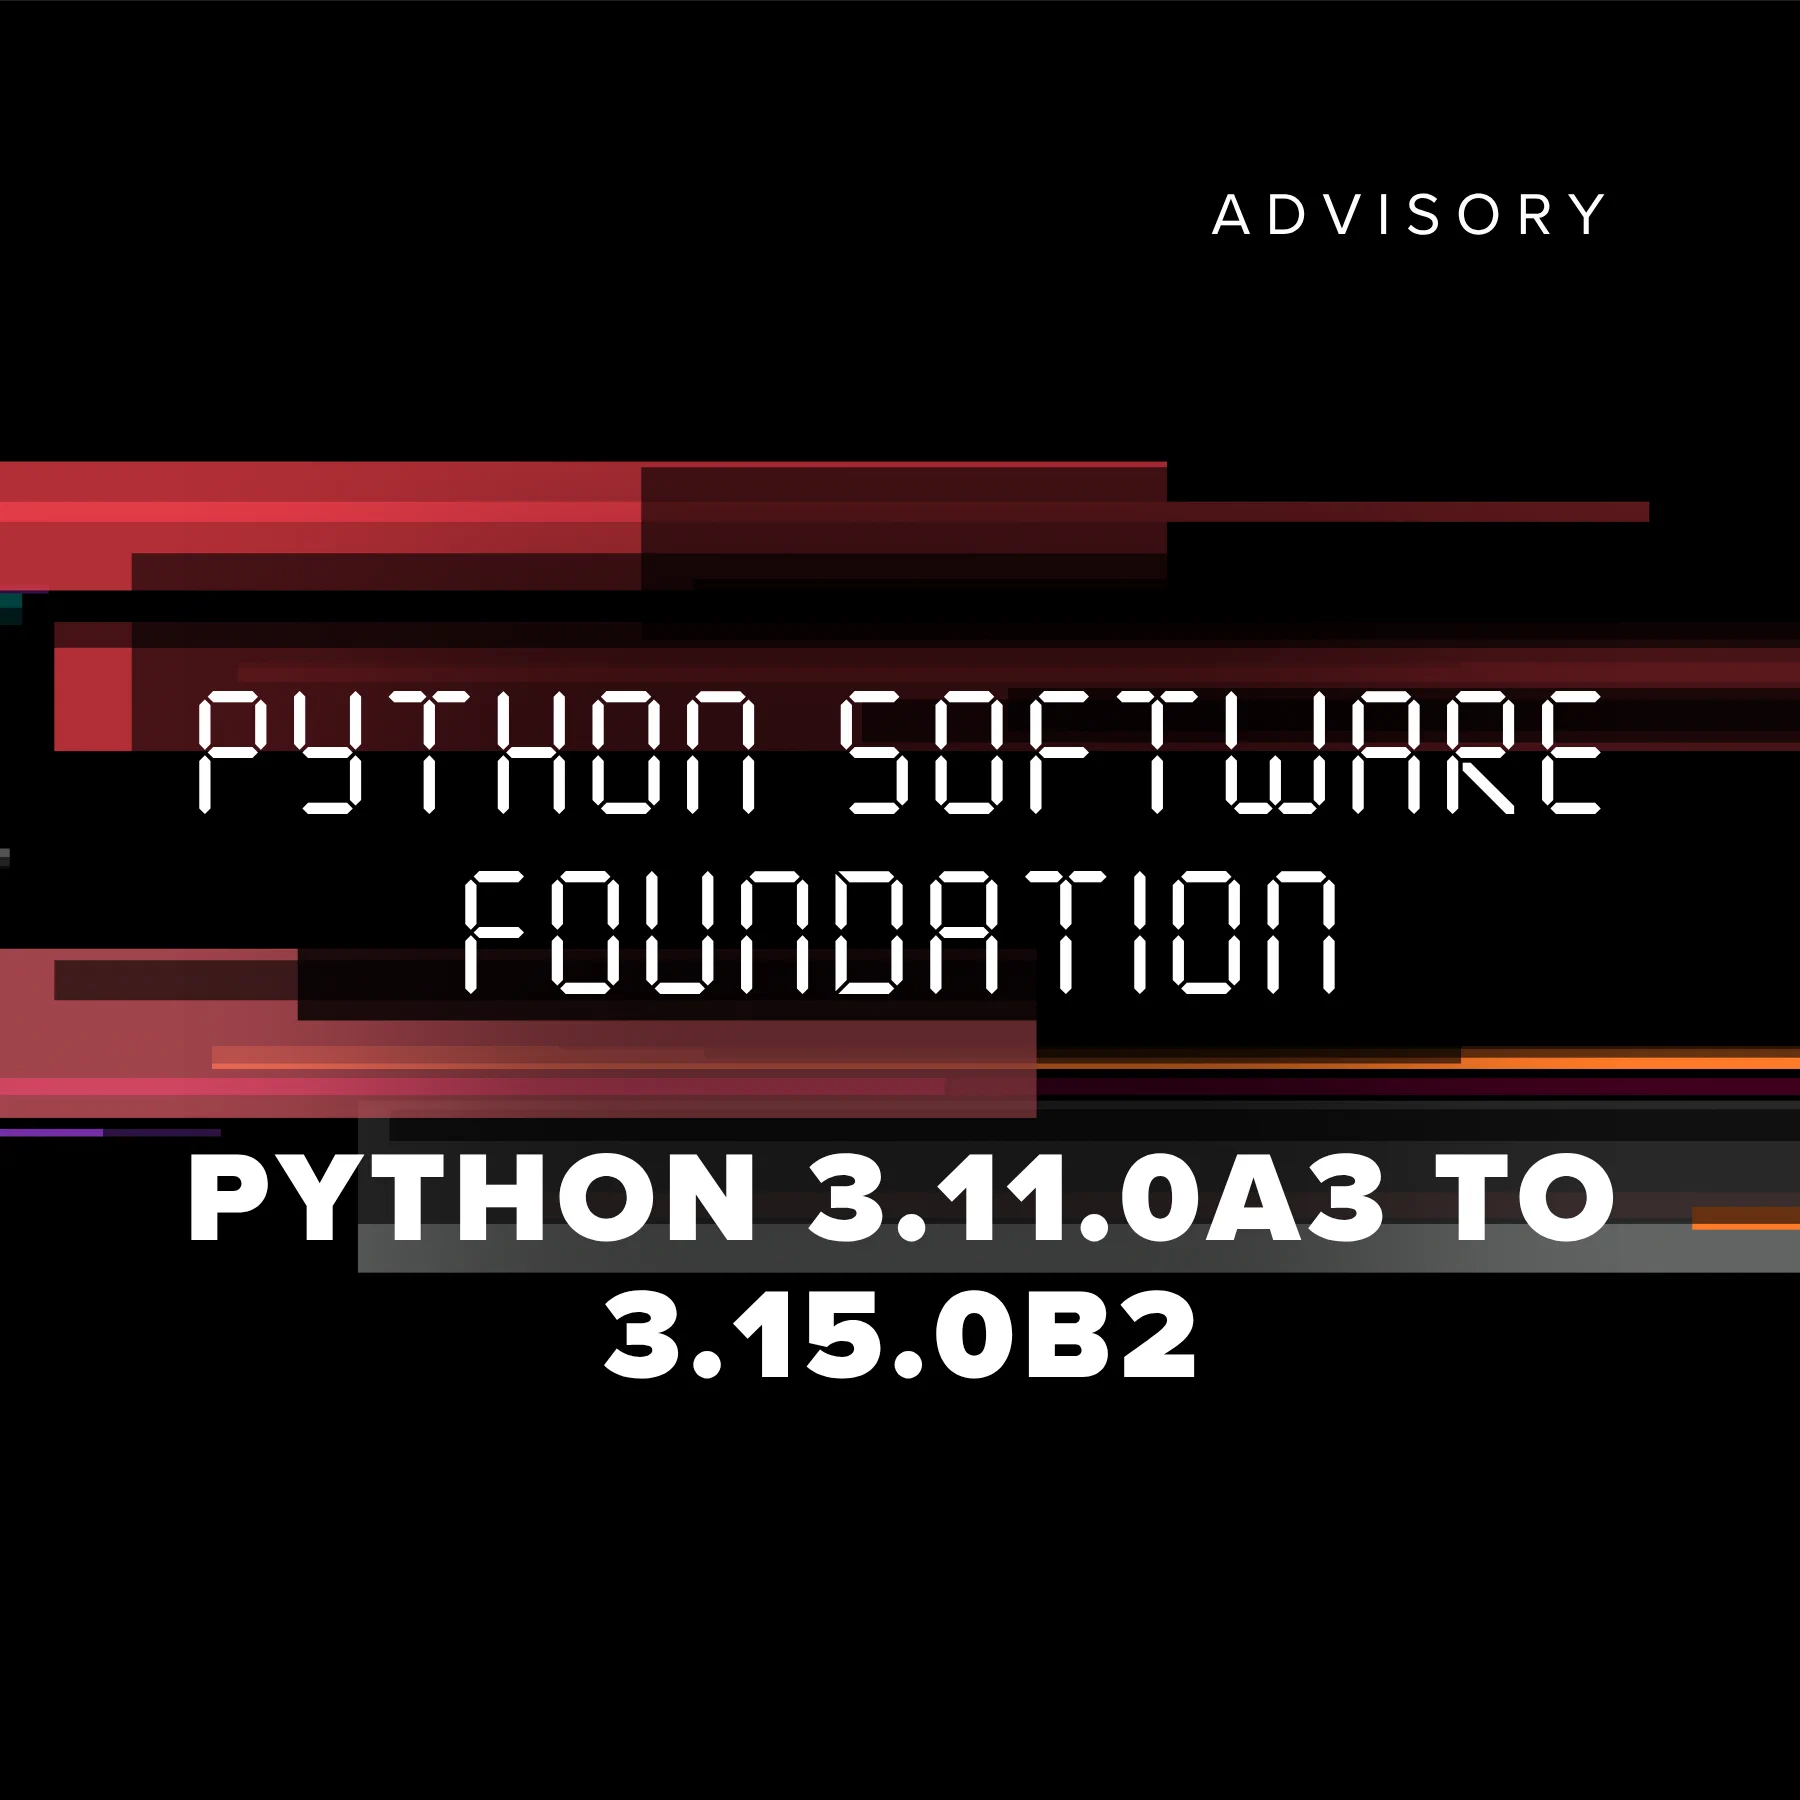
New advisory: CVE-2026-12003 Bishop Fox found a Windows-specific Python vulnerability affecting versions 3.11 - 3.15 that can allow local privilege escalation under the right conditions.
Cybersecurity is a team sport, and the best solutions often come from a mix of perspectives. Check out the latest Threat Source newsletter to hear William reflect on making Hazel a hacker: https:// cs.co/6017B1Oskx
This week on Hacktics and Telemetry, @fulmetalpackets & @_CryptoCat are joined by @stephenfewer to take you behind the scenes of Pwn2Own - the world's premier 0-day competition. Video on YouTube: https:// r-7.co/3TUAot6 Audio on Spotify: https:// r-7.co/4cBHMQo
Every organization has debt. Unpatched code. Governance that never caught up. Skills pipelines quietly hollowed out. For years, that debt was manageable. Exploitation was expensive. But not anymore. AI made exploitation cheap and the bills are due. https:// okt.to/8pArLt
Agents don't know what's out of scope. They just know they haven't hit the goal yet. @ehrishiraj joined Application Security Weekly to talk about what keeps AI pentesters on task prompts help, but environmental boundaries, classifiers, and step limits do the real work. If
[OSSN-0107] Ironic-Python-Agent: Container HardwareManager Security Model Misimplemented
Posted by Jay Faulkner on Aug 13 Ironic Python Agent Container HardwareManager Security Misimplemented --- ### Summary ### Ironic Python Agent's ContainerHardwareManager…
1.00general · 13 Aug, 19:33bleepingcomputer.com
AI 'watermark removers' flood the web. Almost none can prove they work.
Multiple 'watermark removers' have surfaced days after Anthropic began watermarking text generated by Claude, including an open source project with over 4,500 GitHub sta…
0.89exploit · 13 Aug, 23:54seclists.org
APPLE-SA-08-06-2026-2 macOS Sequoia 15.7.9
Posted by Apple Product Security via Fulldisclosure on Aug 13 APPLE-SA-08-06-2026-2 macOS Sequoia 15.7.9 https://support.apple.com/en-us/148171. https://support.apple.co…
Posted by Apple Product Security via Fulldisclosure on Aug 13 APPLE-SA-08-06-2026-3 macOS Sonoma 14.8.9 https://support.apple.com/en-us/148172. https://support.apple.com…
View CSAF Summary Siveillance Video Management Servers contains a vulnerability that could allow a Remote Code Execution attack. Siemens has released new versions for th…