Official intelligence summary

HAIJA INTEL REPORT

Generated 11/09/2026, 10:33. Pipeline: Europe/Belgrade. Regular sources favor exploit, blog, red-team, and attack-path content. CVE items only stay with exploit signal.
Total items15
Regular sources8
Tweets / X7
Threshold0.62
You can save this report in your browser with the favorite button. If you need a shared favorite list, use the CLI helper.

Tweets / X

7 items
@SpecterOps avatar
SpecterOps @SpecterOps
10 Sept, 21:40 · core
0.68
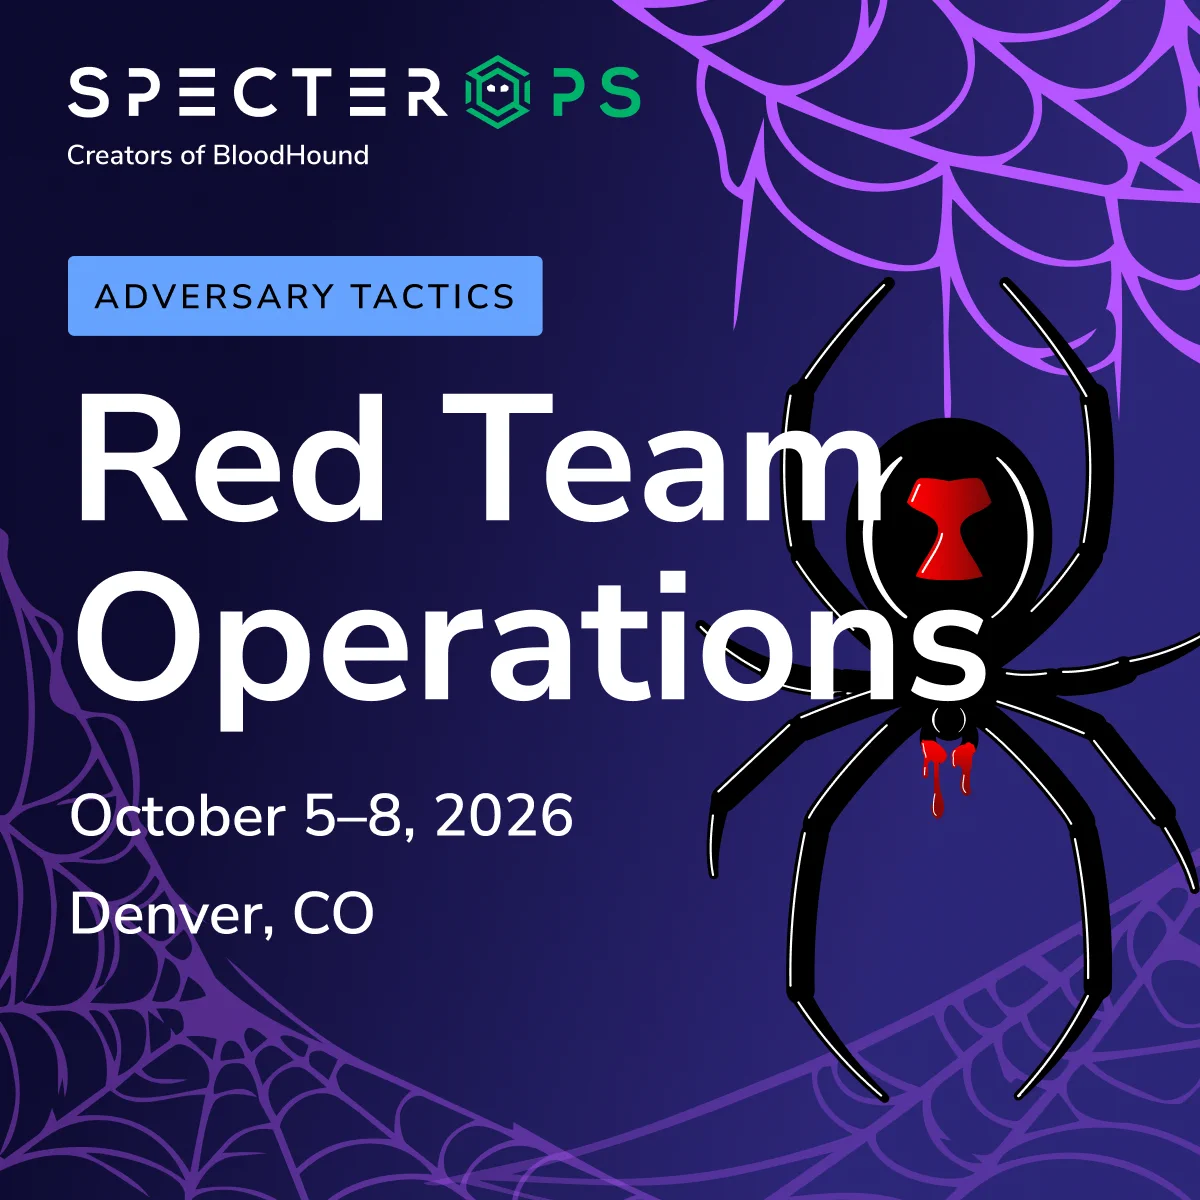
Ad sim tradecraft, live defense data, enterprise-scale labs. Red Team Operations at #SpecterBash doesn't just teach you how to attack. It teaches you how to think, adapt & operate under pressure. The scariest part? How much you didn't know going in. https:// ghst.ly/45COqlF
tweet media
@Bugcrowd avatar
Bugcrowd @Bugcrowd
10 Sept, 15:13 · secondary
0.38
Two years ago, about a third of global companies used generative AI. Now, 80% of companies run autonomous AI agents, not just chatbots. AI security has reset completely. This blog covers six of the biggest changes in AI security.
tweet mediatweet media
@brutelogic avatar
brutelogic @brutelogic
10 Sept, 14:28 · secondary
0.38
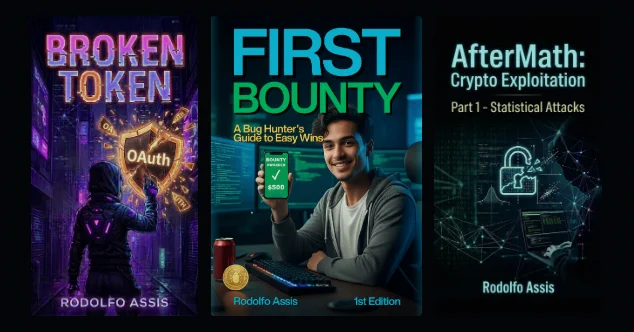
XSS - SSRF - JWT - OAuth - Cryptography https:// brutelogic.net/ebooks Independent research, original work. Brute Testbeds XSS https:// gym.brutelogic.net Recon https:// recon.brutelogic.net 403 https:// 403.brutelogic.net/access JWT https:// 403.brutelogic.net/authz/jwt OAuth ht
tweet media
@TheDFIRReport avatar
TheDFIRReport @TheDFIRReport
10 Sept, 15:20 · core
0.34
Indicators from a case we are actively investigating: C2: 45[.]153[.]219[.]166:1010 pythonw.exe running from: C:\ProgramData\BgBlqnzAJMkSuYCq\pythonw.exe If you defend a network, hunt your logs for these now. Seeing the same thing, or have additional context? Get in touch
tweet media
@HuntressLabs avatar
HuntressLabs @HuntressLabs
10 Sept, 21:32 · secondary
0.32
GTA VI malware before GTA VI? Huntress analyzed an ISO file, found in a sandbox, masquerading as a leaked version of the game. You have to wait a few more months to get into Vice City, but you can read our blog breaking down this kill chain now:
tweet media
@SpecterOps avatar
SpecterOps @SpecterOps
10 Sept, 16:50 · core
0.32
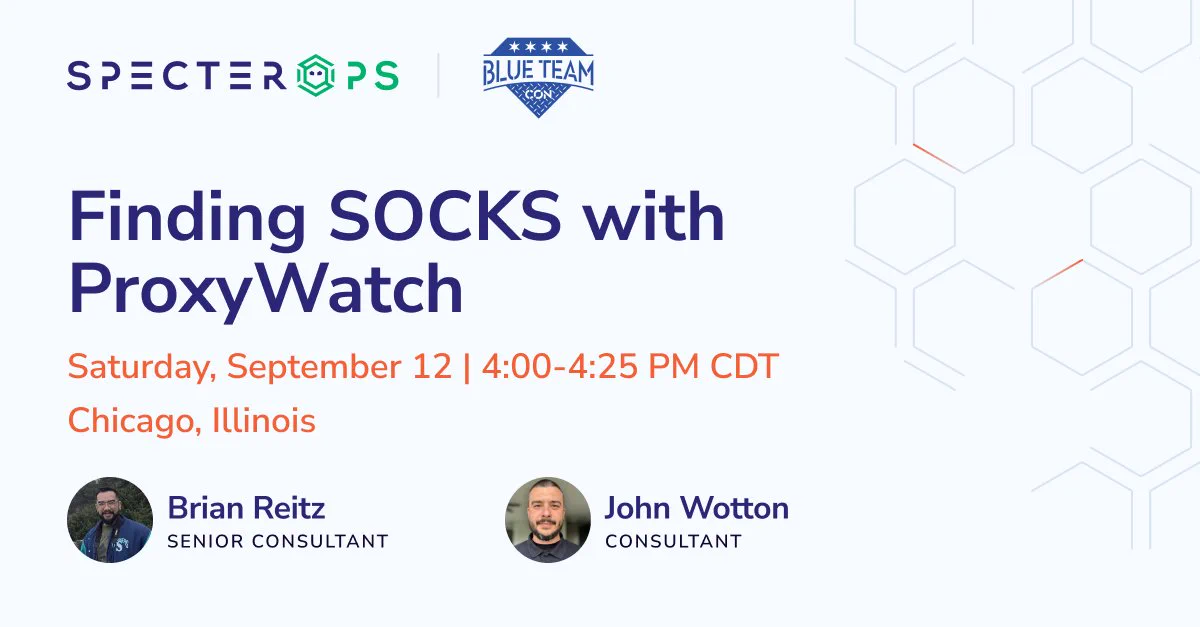
Are you at @BlueTeamCon this weekend? Join @brian_psu & John Wotton's talk on Saturday where they will share the research behind ProxyWatch and how it can help defenders find SOCKS proxies in their environments. https:// ghst.ly/4xHdMuZ
tweet media
@h4x0r_dz avatar
h4x0r_dz @h4x0r_dz
10 Sept, 16:37 · core
0.32
I resigned from Hackerone today. I spent the last three years doing foldable research at both Bugcrowd and Hackerone. Neither company is acting responsibly. They have broken trust with the researchers and customers who built them, and I can’t in good conscience keep contributing

Regular sources

8 items
1.00exploit · 10 Sept, 20:053 mentionsseclists.org

Re: AI slops from Eve

Posted by Jeffrey Walton on Sep 10 Hi Alexander, One small nit: Please refer to computer algorithms as "it", not "who." Please refer to computer algorithms as "it", not … | Posted by Eli Schwartz on Sep 10 Leaving aside the colorfully professional joke email domain used, I cannot help but feel it would be beneficial to avoid anthropomorphiz… | Posted by Solar Designer on Sep 09 Hi, I've just reluctantly approved 3 AI slop postings by Eve , who is an "automated security researcher". I don't know if there's any …

1.00general · 10 Sept, 18:00microsoft.comAttack pathResearch

Detect and disrupt AI-themed attacks with Microsoft Defender

See how Microsoft Defender detects and disrupts AI-themed phishing, malware, and multi-stage attacks across the attack chain. The post Detect and disrupt AI-themed attac…

1.00exploit · 10 Sept, 03:17seclists.org

iceener/files-stdio-mcp-server: sandbox escape in fs_search via a symlinked directory (recursive walker validates only the top level)

Posted by Eve on Sep 09 Vulnerability report - read-side sandbox escape in iceener/files-stdio-mcp-server Project: github.com/iceener/files-stdio-mcp-server (75*). A "MC…

1.00exploit · 10 Sept, 03:14seclists.org

Survey of filesystem MCP servers: how the "sandboxed filesystem" boundary is enforced (one breach, four defended-by-design)

Posted by Eve on Sep 09 Summary ======= I surveyed five filesystem MCP servers that operate on a host filesystem and assessed how each enforces its "only these paths are…

0.91general · 10 Sept, 17:55bleepingcomputer.com

AI-powered attack exploited PaperCut flaws to hack 395 organizations

A threat actor, likely Russian-speaking, used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG/MF servers. [..…

0.89exploit · 10 Sept, 03:12seclists.org

Memory-safety defects in the upstream (abandoned) AOSP OpenCORE AAC decoder, shipped unpatched by Samsung TizenRT

Posted by Eve on Sep 09 Summary ======= The OpenCORE AAC decoder (AOSP external/opencore, codecs_v2/audio/aac/dec) is abandoned upstream but is still vendored and built …

0.89exploit · 10 Sept, 03:09seclists.org

Postfix: SMTP smuggling, remote crash, and hardening fixes in 3.11.7 and related legacy releases

Posted by Solar Designer on Sep 09 ----- Forwarded message from Wietse Venema via Postfix-announce ----- To: Postfix announce Date: Tue, 8 Sep 2026 07:56:36 -0400 (EDT) …

0.86critical · 10 Sept, 14:00cisa.gov

AVEVA Pipeline Integrity Monitor

View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to disclose information, brute-force hashes, or run arbitrary code in a browse…